The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

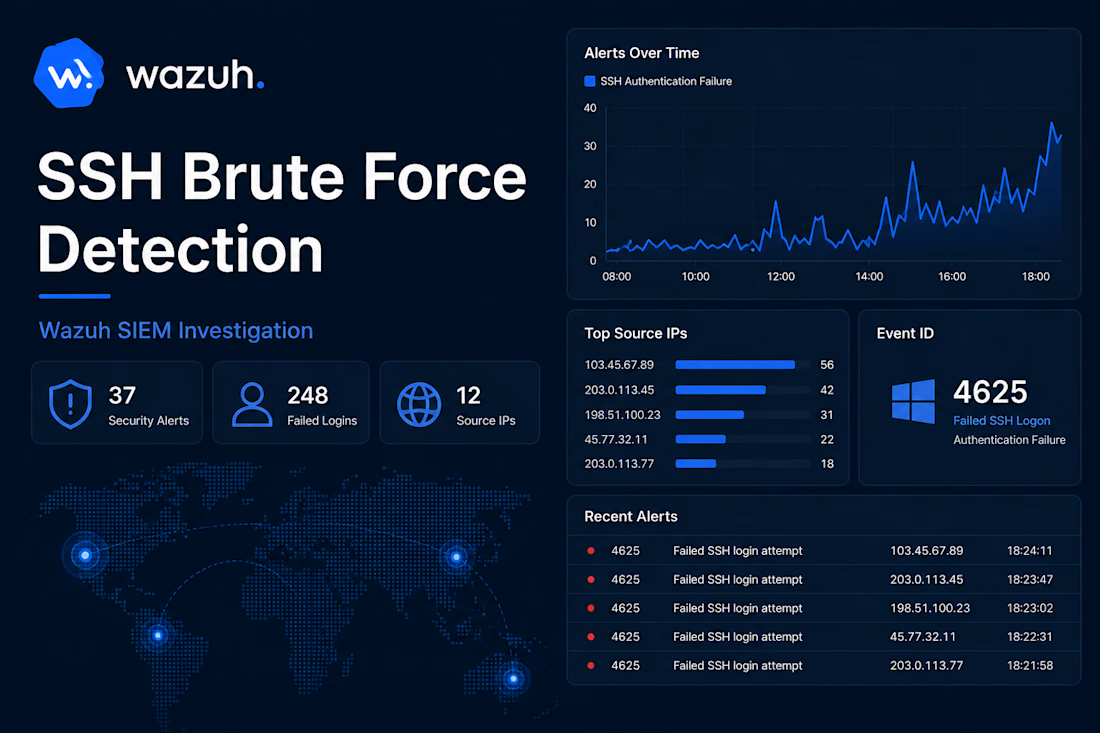
Just Published: Windows SSH Brute-Force Triage & Root Cause Analysis Case Study 🛡️
A few weeks ago, I wrapped up a comprehensive technical assessment lab documenting a multi-platform threat simulation, and I’ve published the full technical triage workflow on my portfolio.
What’s inside the project:
• The Stack: Deployed a centralized Wazuh SIEM Manager on Ubuntu tracking a Windows Endpoint Agent.
• The Scenario: Simulated adversarial reconnaissance (Nmap) followed by a low-volume, stealthy dictionary attack via Hydra using a minimal password set (9 credentials) to mimic a targeted probing sequence.
• The Triage Analysis: Deep-dive log correlation tracking how even a low-noise, 9-attempt sequence generated distinct Windows Event ID 4625 (Logon Failure / Logon Type 8) entries before transitioning to Event ID 4624 (Logon Success / Logon Type 3), marking initial remote CLI access.
• The Deliverables: Complete Indicator of Compromise (IOC) mapping and enterprise-aligned mitigation strategies.
If you are a business owner or an IT team leader looking to secure your infrastructure logging baseline or minimize alert noise, check out the full case study directly on my services page below!
👇 See the Telemetry & Full Breakdown Here:
https://contra.com/p/366OZNqW-wazuh-triage-ssh-bruteforce-lab?r=alkhal_vio107rc
#Cybersecurity #SIEM #Wazuh #LogAnalysis #SystemsEngineering #DataAnalysis
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started




Related posts


MySecret: Zero-Knowledge Encryption Engine & Biometric Security for Obsidian

Check out my latest case: a 40-second launch film for Arch, a platform that lets you borrow against crypto without selling it. I handled it end - to - end, from concept and script to 3D, animation, and edit. Chrome objects, the real app, and one calm beat per idea.
Would love to hear what you think.


This is cool! Great job 🙌


