PAILABS GRC — Governance, Risk & ComplianceShiju Viswanthampi
PAILABS GRC — Governance, Risk & Compliance
PAILABS GRC — Governance, Risk & Compliance
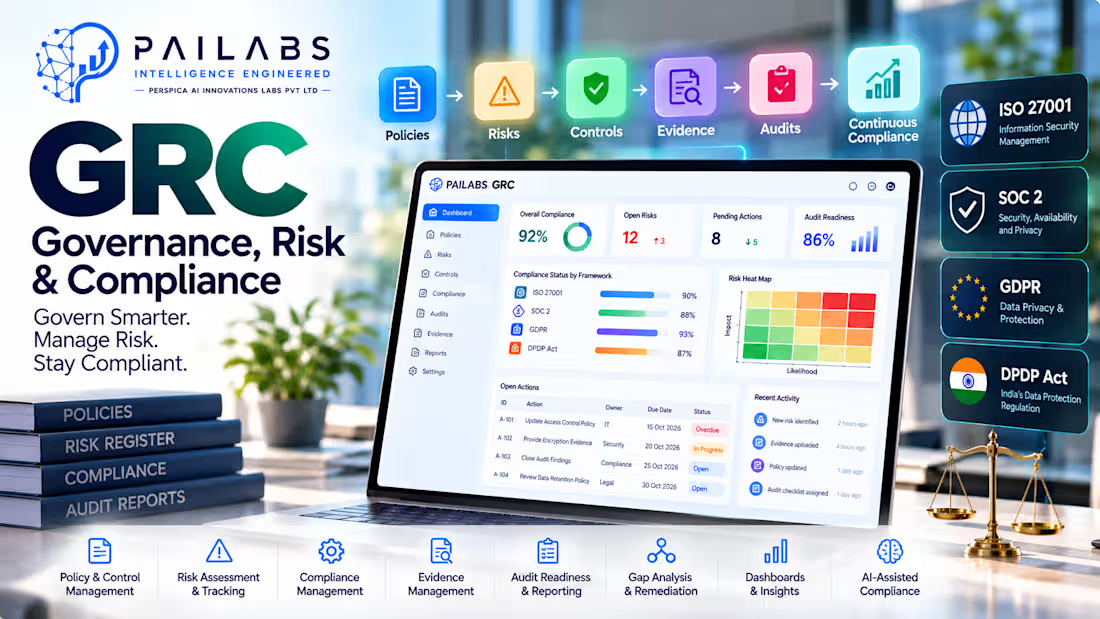
Govern Smarter. Manage Risk. Stay Compliant.
PAILABS GRC is an AI-enabled Governance, Risk and Compliance solution designed to help organizations simplify compliance management, strengthen governance and maintain continuous visibility into organizational risks and controls.
Instead of managing compliance through disconnected spreadsheets, documents, emails and manual follow-ups, PAILABS GRC provides a centralized approach for managing policies, risks, controls, evidence, assessments, audits and remediation activities.
The solution can support organizations working toward or maintaining compliance with frameworks and regulations such as ISO 27001, SOC 2, GDPR and India's DPDP Act, while being adaptable to additional regulatory and organizational requirements.
What we can build
PAILABS can implement GRC capabilities covering policy and control management, risk registers, compliance assessments, evidence management, audit readiness, remediation tracking, dashboards and AI-assisted compliance workflows.
A typical workflow is:
Framework / Regulation → Requirements → Controls → Evidence → Assessment → Gaps & Risks → Remediation → Audit Readiness → Continuous Monitoring
Key capabilities
Compliance Management — Organize regulatory and framework requirements in a centralized environment.
Control Management — Define controls, assign ownership, track implementation and maintain supporting evidence.
Risk Management — Identify, assess, categorize and monitor organizational risks and mitigation actions.
Policy Management — Centralize policies, manage versions, assign owners and support periodic reviews.
Evidence Management — Collect and organize compliance evidence against applicable controls.
Gap Assessment — Identify missing controls, incomplete evidence and areas requiring remediation.
Audit Readiness — Maintain organized controls, documentation and evidence to support internal and external audits.
Corrective Action Tracking — Assign remediation actions, owners and due dates and track them through closure.
Compliance Dashboards — Provide management visibility into compliance status, open risks, overdue actions and audit readiness.
AI-Assisted Compliance — Use AI to analyze policies and documents, identify relevant requirements, summarize gaps and assist compliance teams with large volumes of information.
Multi-framework compliance
A major opportunity for PAILABS GRC is common-control mapping.
Instead of maintaining essentially the same security control independently for ISO 27001, SOC 2, GDPR and other requirements, organizations can map a control and its evidence against multiple applicable frameworks.
For example:
Security Control → ISO 27001 requirement + SOC 2 criterion + privacy requirement → Common Evidence
This can reduce duplicated compliance work and make multi-framework governance easier to manage.
Ideal customers
PAILABS GRC can be positioned for SaaS companies, technology businesses, startups, GCCs, financial services, insurance organizations and other enterprises that need structured governance, security, privacy and compliance management.
Business value
The objective is to move organizations away from periodic, spreadsheet-driven compliance toward a more continuous, evidence-driven GRC model.
PAILABS GRC can help improve visibility, accountability and audit preparedness while reducing repetitive compliance administration.
Contact for pricing
Duration1 week
Tags
Audit Readiness
Compliance Management
DPDP Act
GDPR
ISO 27001
Policy Management ·
Risk Management
Security Compliance
SOC 2
Service provided by
Shiju Viswanthampi proChennai, India
- 1
- Followers
PAILABS GRC — Governance, Risk & ComplianceShiju Viswanthampi
Contact for pricing
Duration1 week
Tags
Audit Readiness
Compliance Management
DPDP Act
GDPR
ISO 27001
Policy Management ·
Risk Management
Security Compliance
SOC 2
PAILABS GRC — Governance, Risk & Compliance
PAILABS GRC — Governance, Risk & Compliance
Govern Smarter. Manage Risk. Stay Compliant.
PAILABS GRC is an AI-enabled Governance, Risk and Compliance solution designed to help organizations simplify compliance management, strengthen governance and maintain continuous visibility into organizational risks and controls.
Instead of managing compliance through disconnected spreadsheets, documents, emails and manual follow-ups, PAILABS GRC provides a centralized approach for managing policies, risks, controls, evidence, assessments, audits and remediation activities.
The solution can support organizations working toward or maintaining compliance with frameworks and regulations such as ISO 27001, SOC 2, GDPR and India's DPDP Act, while being adaptable to additional regulatory and organizational requirements.
What we can build
PAILABS can implement GRC capabilities covering policy and control management, risk registers, compliance assessments, evidence management, audit readiness, remediation tracking, dashboards and AI-assisted compliance workflows.
A typical workflow is:
Framework / Regulation → Requirements → Controls → Evidence → Assessment → Gaps & Risks → Remediation → Audit Readiness → Continuous Monitoring
Key capabilities
Compliance Management — Organize regulatory and framework requirements in a centralized environment.
Control Management — Define controls, assign ownership, track implementation and maintain supporting evidence.
Risk Management — Identify, assess, categorize and monitor organizational risks and mitigation actions.
Policy Management — Centralize policies, manage versions, assign owners and support periodic reviews.
Evidence Management — Collect and organize compliance evidence against applicable controls.
Gap Assessment — Identify missing controls, incomplete evidence and areas requiring remediation.
Audit Readiness — Maintain organized controls, documentation and evidence to support internal and external audits.
Corrective Action Tracking — Assign remediation actions, owners and due dates and track them through closure.
Compliance Dashboards — Provide management visibility into compliance status, open risks, overdue actions and audit readiness.
AI-Assisted Compliance — Use AI to analyze policies and documents, identify relevant requirements, summarize gaps and assist compliance teams with large volumes of information.
Multi-framework compliance
A major opportunity for PAILABS GRC is common-control mapping.
Instead of maintaining essentially the same security control independently for ISO 27001, SOC 2, GDPR and other requirements, organizations can map a control and its evidence against multiple applicable frameworks.
For example:
Security Control → ISO 27001 requirement + SOC 2 criterion + privacy requirement → Common Evidence
This can reduce duplicated compliance work and make multi-framework governance easier to manage.
Ideal customers
PAILABS GRC can be positioned for SaaS companies, technology businesses, startups, GCCs, financial services, insurance organizations and other enterprises that need structured governance, security, privacy and compliance management.
Business value
The objective is to move organizations away from periodic, spreadsheet-driven compliance toward a more continuous, evidence-driven GRC model.
PAILABS GRC can help improve visibility, accountability and audit preparedness while reducing repetitive compliance administration.
Contact for pricing