Codebase Rescue, Cleanup & AuditsSineth Madduma
Outcome
You find out where your repository actually stands: does it install, build and test, what's broken, and what to fix first. No guesswork and no open-ended bill.
What's included (Repository Health Review, $400)
One repository in one primary ecosystem (for example Node/TypeScript or Python)
Up to about 10,000 relevant source lines, or a boundary we agree in writing (vendored, generated and lock files don't count)
Dependency and install review from a clean clone
A build and test run, where it can run without your production services
A basic review of CI and documentation
Prioritised findings, each with its evidence: the file and line, or the command and its output
A written action plan
One small agreed repair, if it fits within an hour
A 30-minute walkthrough call
This is a review, not a full repair. I don't promise the repository will work at the end of it. I promise you'll know what's wrong and what it takes to fix.
Not included
Refactors, full dependency upgrades, rewrites, enterprise security assessments, penetration testing, CI/CD redesign, open-ended debugging and incident response. Paid CI minutes, tools or cloud resources needed to run the code are paid by you.
Delivery estimate
4 working days from when I have access.
What I need from you
Read access to the repository
Test values for any required environment variables, or a note that they aren't available
Ten minutes of context on what the code is supposed to do
Revisions
If a finding is unclear or its evidence doesn't hold up, I correct it. You have 7 days after delivery to ask questions about the findings. The one repair has a 14-day fix window.
Done when
Each finding cites its evidence (file and line, or a command and its output)
The scope and line count are stated at the top of the report
Every command I ran is listed, so the checks can be repeated
The plan names the next step and what it would cost
If it's bigger or more complicated
If the repository is over about 10,000 relevant lines, spans several ecosystems or can't run without production services, I tell you before I start: add a 10,000-line band ($250), agree a boundary, or move to the Detailed Technical Audit (from $750). If it needs more than the one small repair, the report says what it takes and which package fits. Nothing extra is done or billed without your agreement.
Larger packages
Detailed Technical Audit: from $750. Up to about 25,000 lines; findings ranked by severity, each marked as run or read; coverage, lint and type checks; a container build; before/after examples; a prioritised plan.
Remediation Sprint: from $1,000. About 9 hours of agreed fixes from a review or audit, as pull requests with tests for the code I touch.
Codebase Rescue: from $2,500. Installs, builds and passes CI from a clean clone; agreed high-severity findings fixed; a documented deploy path.
Ongoing Maintenance: custom monthly quote, starting from $200/month.
Add-ons
+10,000 relevant lines $250 · Extended testing $250 · Documentation pack $225 · Priority delivery +30% (when my calendar allows)
Example projects
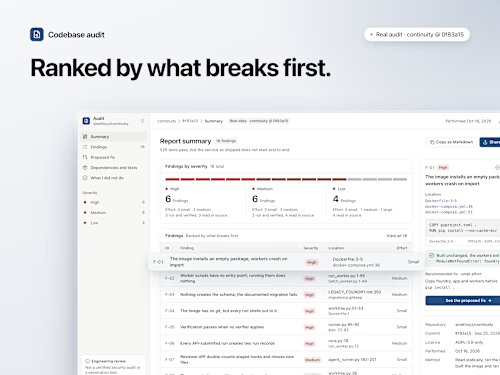
Codebase Audit of an Open-Source Python Runtime (Implemented: a real audit I performed on my own public repository, continuity @ 0f83a15, with 16 findings, each citing a file and line; data shown is real)
Next step
Buy the review, or message me on Contra with the repository's language, a rough size and what's going wrong. I'll reply within two working days.
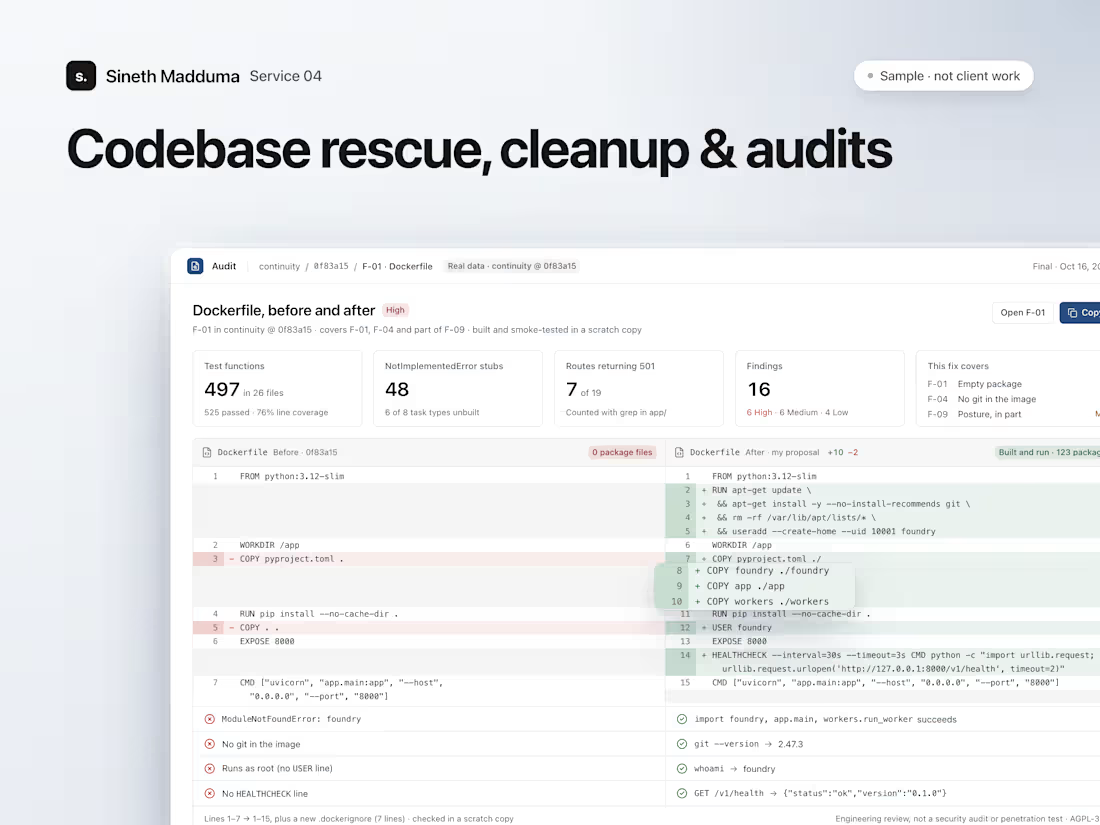
Cover: one real fix from my audit of my own public repo, not client work. Status: Implemented. I audited continuity @ 0f83a15 and found 16 issues: 6 High, 6 Medium and 4 Low. Its 525 tests pass, but the Docker image fails to start the worker. The cover shows my Dockerfile fix before and after. I built the fixed image and smoke-tested it: it runs as a non-root user, imports cleanly and the health check returns ok. The fix is a proposal and is not merged upstream. I did not run the full stack or a live model.
FAQs
Example work
Sineth 's other services
Starting at$400
Duration1 week
Tags
Docker
GitHub
Node.js
Python
TypeScript
Software Engineer
Service provided by
Sineth Madduma London, UK
- 1
- Followers
Codebase Rescue, Cleanup & AuditsSineth Madduma
Starting at$400
Duration1 week
Tags
Docker
GitHub
Node.js
Python
TypeScript
Software Engineer
Outcome
You find out where your repository actually stands: does it install, build and test, what's broken, and what to fix first. No guesswork and no open-ended bill.
What's included (Repository Health Review, $400)
One repository in one primary ecosystem (for example Node/TypeScript or Python)
Up to about 10,000 relevant source lines, or a boundary we agree in writing (vendored, generated and lock files don't count)
Dependency and install review from a clean clone
A build and test run, where it can run without your production services
A basic review of CI and documentation
Prioritised findings, each with its evidence: the file and line, or the command and its output
A written action plan
One small agreed repair, if it fits within an hour
A 30-minute walkthrough call
This is a review, not a full repair. I don't promise the repository will work at the end of it. I promise you'll know what's wrong and what it takes to fix.
Not included
Refactors, full dependency upgrades, rewrites, enterprise security assessments, penetration testing, CI/CD redesign, open-ended debugging and incident response. Paid CI minutes, tools or cloud resources needed to run the code are paid by you.
Delivery estimate
4 working days from when I have access.
What I need from you
Read access to the repository
Test values for any required environment variables, or a note that they aren't available
Ten minutes of context on what the code is supposed to do
Revisions
If a finding is unclear or its evidence doesn't hold up, I correct it. You have 7 days after delivery to ask questions about the findings. The one repair has a 14-day fix window.
Done when
Each finding cites its evidence (file and line, or a command and its output)
The scope and line count are stated at the top of the report
Every command I ran is listed, so the checks can be repeated
The plan names the next step and what it would cost
If it's bigger or more complicated
If the repository is over about 10,000 relevant lines, spans several ecosystems or can't run without production services, I tell you before I start: add a 10,000-line band ($250), agree a boundary, or move to the Detailed Technical Audit (from $750). If it needs more than the one small repair, the report says what it takes and which package fits. Nothing extra is done or billed without your agreement.
Larger packages
Detailed Technical Audit: from $750. Up to about 25,000 lines; findings ranked by severity, each marked as run or read; coverage, lint and type checks; a container build; before/after examples; a prioritised plan.
Remediation Sprint: from $1,000. About 9 hours of agreed fixes from a review or audit, as pull requests with tests for the code I touch.
Codebase Rescue: from $2,500. Installs, builds and passes CI from a clean clone; agreed high-severity findings fixed; a documented deploy path.
Ongoing Maintenance: custom monthly quote, starting from $200/month.
Add-ons
+10,000 relevant lines $250 · Extended testing $250 · Documentation pack $225 · Priority delivery +30% (when my calendar allows)
Example projects
Codebase Audit of an Open-Source Python Runtime (Implemented: a real audit I performed on my own public repository, continuity @ 0f83a15, with 16 findings, each citing a file and line; data shown is real)
Next step
Buy the review, or message me on Contra with the repository's language, a rough size and what's going wrong. I'll reply within two working days.
Cover: one real fix from my audit of my own public repo, not client work. Status: Implemented. I audited continuity @ 0f83a15 and found 16 issues: 6 High, 6 Medium and 4 Low. Its 525 tests pass, but the Docker image fails to start the worker. The cover shows my Dockerfile fix before and after. I built the fixed image and smoke-tested it: it runs as a non-root user, imports cleanly and the health check returns ok. The fix is a proposal and is not merged upstream. I did not run the full stack or a live model.
FAQs
Example work
Sineth 's other services
$400