I will audit your AI agents and MCP servers for security risksHamza Ghebrich
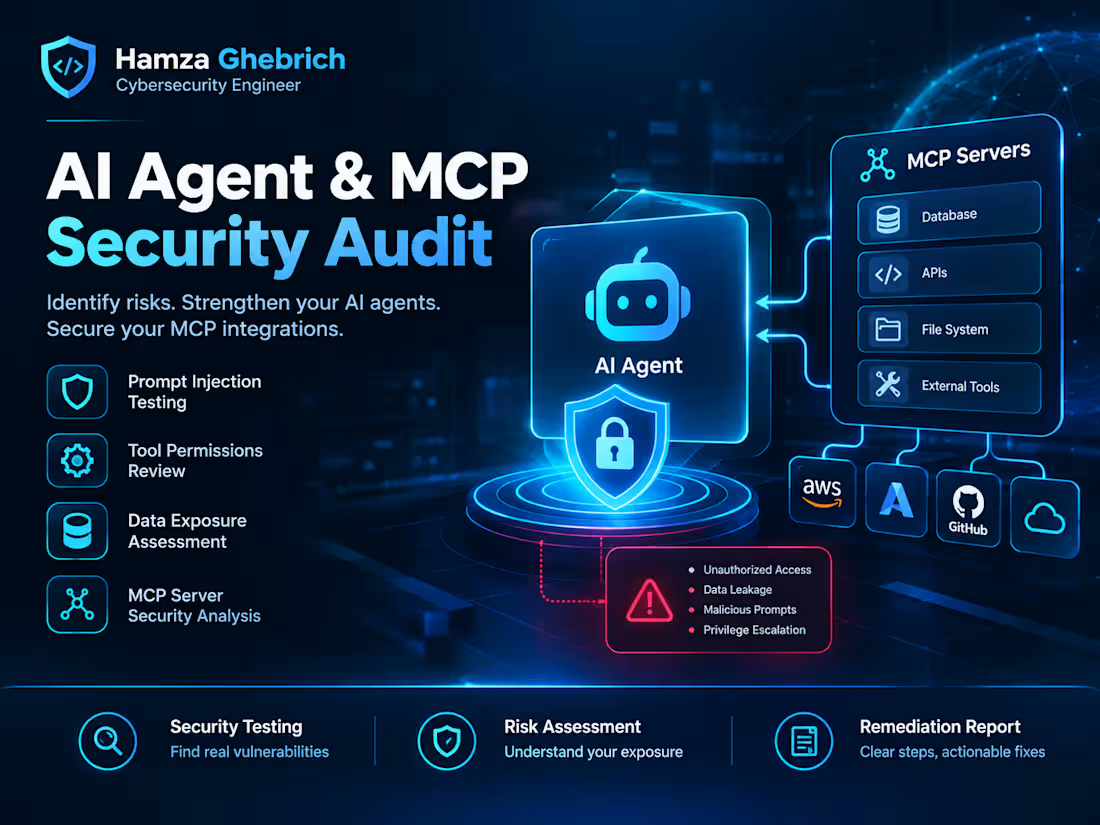
Is Your AI Agent Secure?
AI agents are increasingly connected to databases, APIs, internal documents, and external tools. These integrations introduce security risks that traditional application security scans may overlook.
I help startups, SaaS companies, and AI developers identify security weaknesses in their AI agents and Model Context Protocol (MCP) integrations.
🔐 What I Will Assess
1. Prompt Injection & Agent Manipulation
Test resistance to malicious instructions.
Evaluate unsafe agent behavior.
Identify potential instruction-handling weaknesses.
2. MCP Server & Tool Security
Review MCP server configurations.
Examine tool permissions and access controls.
Identify unsafe tool invocation paths.
3. Sensitive Data Exposure
Assess potential leakage of sensitive information.
Review how agents handle confidential context.
Examine relevant authentication and authorization controls.
4. Agent Security Controls
Evaluate security boundaries between agents and tools.
Review permission enforcement where supported.
Identify opportunities to strengthen security controls.
📦 What You Will Receive
✅ Security assessment of one agreed AI-agent application or MCP integration.
✅ Documented findings with severity ratings.
✅ Reproducible evidence for confirmed issues.
✅ Practical remediation recommendations.
✅ Professional PDF security report.
✅ One follow-up discussion to explain the findings.
🛠️ My Technical Background
I'm a Cybersecurity Engineer specializing in AI Security, DevSecOps, and security automation.
I develop open-source security projects, including:
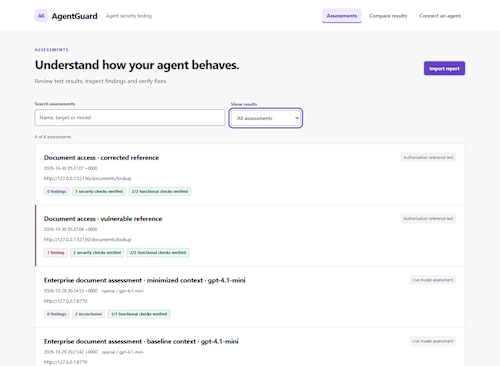
AgentGuard: AI-agent security assessment and testing.
MCP Security Auditor: MCP integration security analysis.
SafeShell: Secure command execution and policy enforcement research.
My approach combines automated checks with manual security analysis to produce actionable results.
⏱️ Scope & Delivery
Starter assessment:
One small AI-agent application or MCP integration.
Up to 3 agreed security test scenarios.
Estimated delivery: 3–5 business days.
One written security report.
One follow-up discussion.
Additional integrations, complex architectures, and extended testing require a custom quote.
🚀 Let's Secure Your AI Application
Send me a message describing your AI-agent architecture, MCP integrations, and security concerns.
I'll help define an assessment scope that matches your needs.
All testing is performed only with explicit authorization and within an agreed scope. An assessment does not guarantee that an application is free of vulnerabilities.
FAQs
Contact for pricing
Duration1 week
Tags
API Security
Python
Application Security
Cybersecurity Specialist
LLM
Penetration Testing
Artificial Intelligence
AI Security
Security Auditing
Service provided by
Hamza Ghebrich Paris, France
- 1
- Followers
I will audit your AI agents and MCP servers for security risksHamza Ghebrich
Contact for pricing
Duration1 week
Tags
API Security
Python
Application Security
Cybersecurity Specialist
LLM
Penetration Testing
Artificial Intelligence
AI Security
Security Auditing
Is Your AI Agent Secure?
AI agents are increasingly connected to databases, APIs, internal documents, and external tools. These integrations introduce security risks that traditional application security scans may overlook.
I help startups, SaaS companies, and AI developers identify security weaknesses in their AI agents and Model Context Protocol (MCP) integrations.
🔐 What I Will Assess
1. Prompt Injection & Agent Manipulation
Test resistance to malicious instructions.
Evaluate unsafe agent behavior.
Identify potential instruction-handling weaknesses.
2. MCP Server & Tool Security
Review MCP server configurations.
Examine tool permissions and access controls.
Identify unsafe tool invocation paths.
3. Sensitive Data Exposure
Assess potential leakage of sensitive information.
Review how agents handle confidential context.
Examine relevant authentication and authorization controls.
4. Agent Security Controls
Evaluate security boundaries between agents and tools.
Review permission enforcement where supported.
Identify opportunities to strengthen security controls.
📦 What You Will Receive
✅ Security assessment of one agreed AI-agent application or MCP integration.
✅ Documented findings with severity ratings.
✅ Reproducible evidence for confirmed issues.
✅ Practical remediation recommendations.
✅ Professional PDF security report.
✅ One follow-up discussion to explain the findings.
🛠️ My Technical Background
I'm a Cybersecurity Engineer specializing in AI Security, DevSecOps, and security automation.
I develop open-source security projects, including:
AgentGuard: AI-agent security assessment and testing.
MCP Security Auditor: MCP integration security analysis.
SafeShell: Secure command execution and policy enforcement research.
My approach combines automated checks with manual security analysis to produce actionable results.
⏱️ Scope & Delivery
Starter assessment:
One small AI-agent application or MCP integration.
Up to 3 agreed security test scenarios.
Estimated delivery: 3–5 business days.
One written security report.
One follow-up discussion.
Additional integrations, complex architectures, and extended testing require a custom quote.
🚀 Let's Secure Your AI Application
Send me a message describing your AI-agent architecture, MCP integrations, and security concerns.
I'll help define an assessment scope that matches your needs.
All testing is performed only with explicit authorization and within an agreed scope. An assessment does not guarantee that an application is free of vulnerabilities.
FAQs
Contact for pricing