AWS Security Governance, S3 Lifecycle & Attack ReconstructionLeonardo Romero
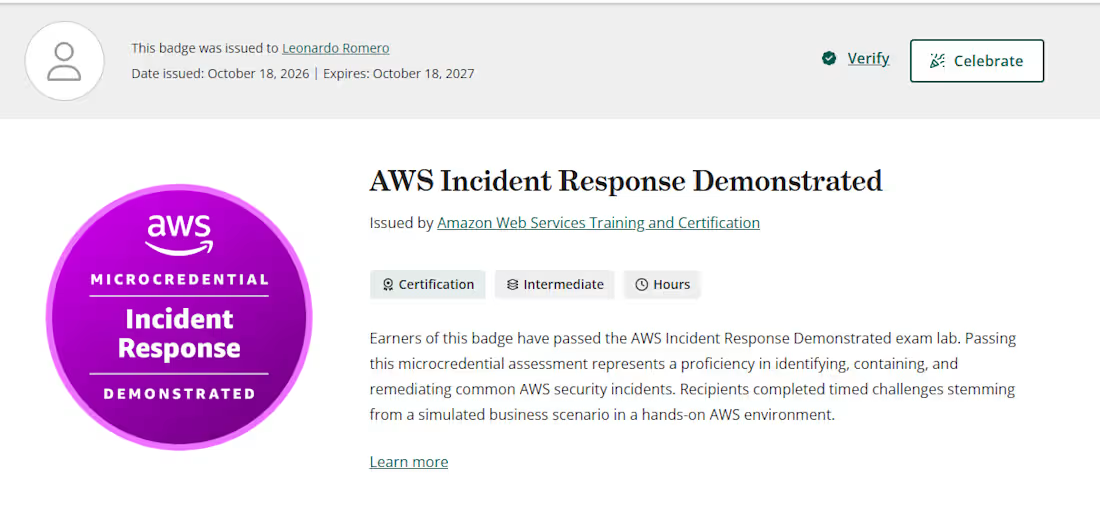
I help teams improve AWS security through scoped cloud governance tasks, S3 lifecycle configuration, IAM policy reviews, and attack reconstruction based on available evidence.
What's included:
Cloud governance: Review of account-level security settings and governance requirements.
Amazon S3 lifecycle management: Configure or document bucket lifecycle rules for object expiration and retention, based on client requirements.
Security policies: Review IAM policies and selected security configurations to identify excessive permissions or potential misconfigurations.
Security tooling: Assist with reviewing relevant AWS security tools and their configurations within the agreed scope.
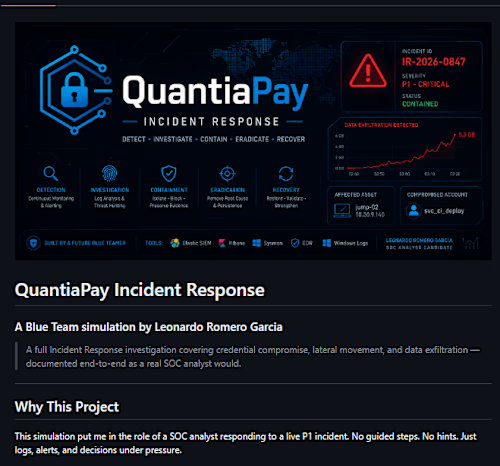
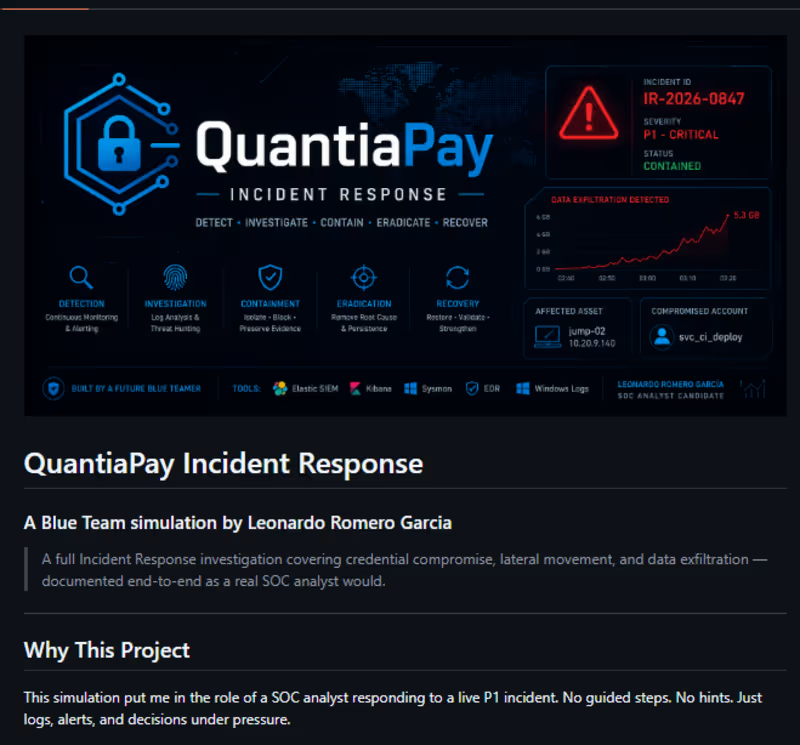
Attack reconstruction: Build an evidence-based incident timeline from available CloudTrail events, logs, alerts, and other authorized artifacts.
Findings and recommendations: Deliver a structured report explaining observations, risks, and recommended remediation steps.
Deliverables: A configuration summary, documented findings, an incident timeline when applicable, and prioritized recommendations.
Each engagement has a clearly defined scope. Changes to production accounts, access permissions, retention requirements, and remediation actions must be approved by the client. Attack reconstruction is limited to conclusions supported by the available evidence.
This service does not include penetration testing, guaranteed incident attribution, or a guarantee that an AWS environment is fully secure.
Example work
Starting at$55
Duration1 week
Tags
AWS
AWS S3
AWS VPC

Amazon Web Services
Cloud Security Engineer
Cloud Governance
Digital Forensics
IAM Policies
Security Audit
Service provided by
Leonardo Romero Jiutepec, Mexico
AWS Security Governance, S3 Lifecycle & Attack ReconstructionLeonardo Romero
Starting at$55
Duration1 week
Tags
AWS
AWS S3
AWS VPC
Amazon Web Services
Cloud Security Engineer
Cloud Governance
Digital Forensics
IAM Policies
Security Audit
I help teams improve AWS security through scoped cloud governance tasks, S3 lifecycle configuration, IAM policy reviews, and attack reconstruction based on available evidence.
What's included:
Cloud governance: Review of account-level security settings and governance requirements.
Amazon S3 lifecycle management: Configure or document bucket lifecycle rules for object expiration and retention, based on client requirements.
Security policies: Review IAM policies and selected security configurations to identify excessive permissions or potential misconfigurations.
Security tooling: Assist with reviewing relevant AWS security tools and their configurations within the agreed scope.
Attack reconstruction: Build an evidence-based incident timeline from available CloudTrail events, logs, alerts, and other authorized artifacts.
Findings and recommendations: Deliver a structured report explaining observations, risks, and recommended remediation steps.
Deliverables: A configuration summary, documented findings, an incident timeline when applicable, and prioritized recommendations.
Each engagement has a clearly defined scope. Changes to production accounts, access permissions, retention requirements, and remediation actions must be approved by the client. Attack reconstruction is limited to conclusions supported by the available evidence.
This service does not include penetration testing, guaranteed incident attribution, or a guarantee that an AWS environment is fully secure.
Example work
$55