Freelancers using Ollama in Mumbai
Freelancers using Ollama in Mumbai
Sign Up
Post a job
Sign Up
Log In
Filters
2
Projects
People
Anurag Nagare
Mumbai, India
I’m an AI & Machine Learning engineer with expertise in deve
Follow
Message
I’m an AI & Machine Learning engineer with expertise in deve
0
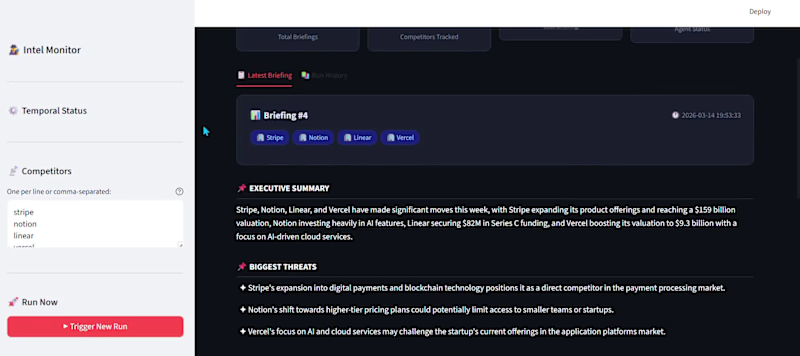
It all started on a Sunday at the AWS User Group Mumbai meetup. I wasn't expecting to walk away with a new obsession, but then the speaker introduced me to Temporal and everything changed. Temporal is a durable execution engine that solves one of the hardest problems in agentic AI what happens when your LLM workflow crashes mid-run? Normally you lose everything So I went home and built this: an agent that monitors your competitors around the clock tracking pricing changes, product launches, hiring signals, and strategic moves. Every 24 hours it uses Mistral (running fully on-device via Ollama) to analyze the data and synthesize a structured executive briefing delivered straight to your inbox. Sometimes the best projects start with a Sunday conversation. https://github.com/AnuragNagare/Agentic-AI-.git
0
77
0
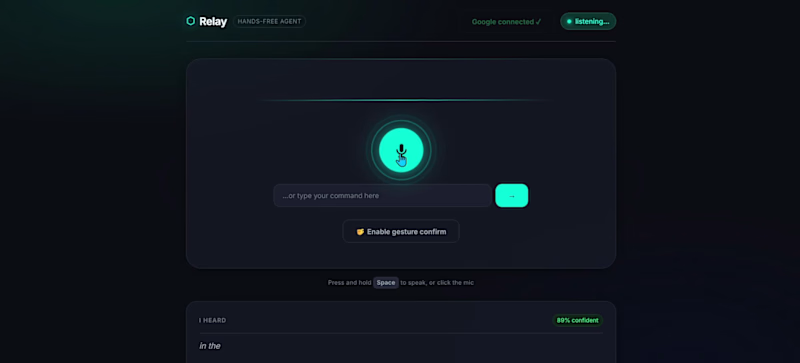
One Gate: Voice-controlled Gmail, Calendar, and Drive that can't fire the wrong thing Every "AI agent" demo shows a voice command turning into a sent email like magic, but almost nobody shows the part that actually matters: what stops it from sending the wrong thing. I built proof: an agent that runs your Gmail, Calendar, Contacts, and Drive by voice reply to a thread, schedule a meeting, archive an email, find a file hands-free end to end, but never fires anything irreversible without you saying so. The honest hard part isn't getting an LLM to sound smart, it's this: a transcript goes to LLM against a strict JSON schema and comes back as an ordered plan, every step tagged reversible or not and exactly one thing in the whole system is allowed to check that flag. Finding a thread, drafting a reply, creating a calendar event: those just run. The result covers real ground without ever feeling like it's guessing: forward or reply to email with the original quoted underneath, archive/label/trash, resolve a name to a real address through your Contacts first and your mail history as fallback, schedule an event that creates quietly and only emails the invite after a second confirmation, answer "what did John say" or "what's on my calendar Thursday" grounded in content actually fetched from your account not hallucinated. No backend, no server anywhere in the loop
0
28
0
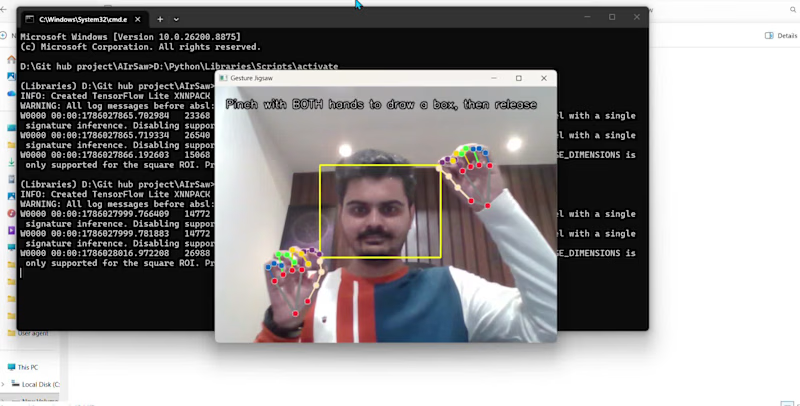
What every "AI gesture control" demo quietly leaves out Everyone films a hand waving at a screen and calls it AI. Almost nobody shows what's underneath that there's usually no gesture model at all. A "grab" is one distance crossing a line. Here's proof. I built a jigsaw puzzle you solve with your bare hands no mouse, no controller, no gesture classifier, no training.
0
58
2
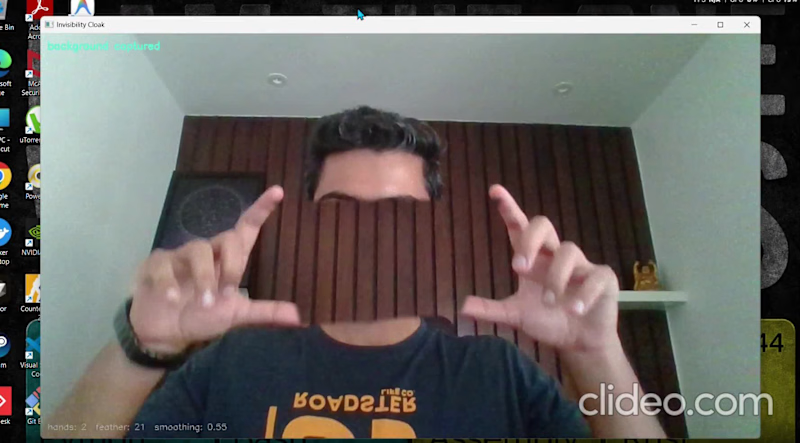
Everyone's building AR filters and calling it "computer vision magic." Almost nobody's asking what's actually happening underneath — that most of these effects are just clever masking, not detection. Here's proof. I built an invisibility cloak that runs entirely in the browser, no green screen, no chroma key, no model training. https://github.com/AnuragNagare/Ghost-frame
4
2
273
Ollama
(1)
Follow
Message
Gyanranjan Jha
Mumbai, India
Cybersecurity Engineer , Full stack Web Developer.
New to Contra
Follow
Message
Cybersecurity Engineer , Full stack Web Developer.
0
I am excited to share a project I've been working on: the_almighty, a deterministic web-vulnerability scanner built entirely in Go. Unlike traditional black-box scanners that rely on simple payload spraying, the_almighty is designed with high signal-to-noise ratio in mind. Findings are only reported when verified by a Go oracle (e.g., verbatim reflection, error signature, time delay, or an out-of-band callback). Key Capabilities: 🔹 OOB Correlation: Captures blind/stored XSS, SSRF, and command injections via tokenized out-of-band callbacks. 🔹 Grey-box IAST: Server-side PHP and JS agents locate tainted input reaching dangerous sinks with file and line numbers. 🔹 Headless Browser Crawler: Leverages a pooled headless Chrome instance to crawl modern single-page applications. 🔹 AI-Powered Payload Widening: Uses local LLMs (via Ollama) to dynamically generate and expand test payloads, keeping validation deterministic. 🔹 Observation Engine: Correlates, deduplicates, and scores results into SQLite (WAL) for a clean, prioritized list. Engineered with a strict scope guard and per-host rate limiters to guarantee scanning stays safe and within boundaries. Stack: Go 1.26, Cobra, chromedp, SQLite, and Ollama. #ApplicationSecurity #SoftwareEngineering #GoLang #IAST #PenetrationTesting #DevSecOps
0
61
0
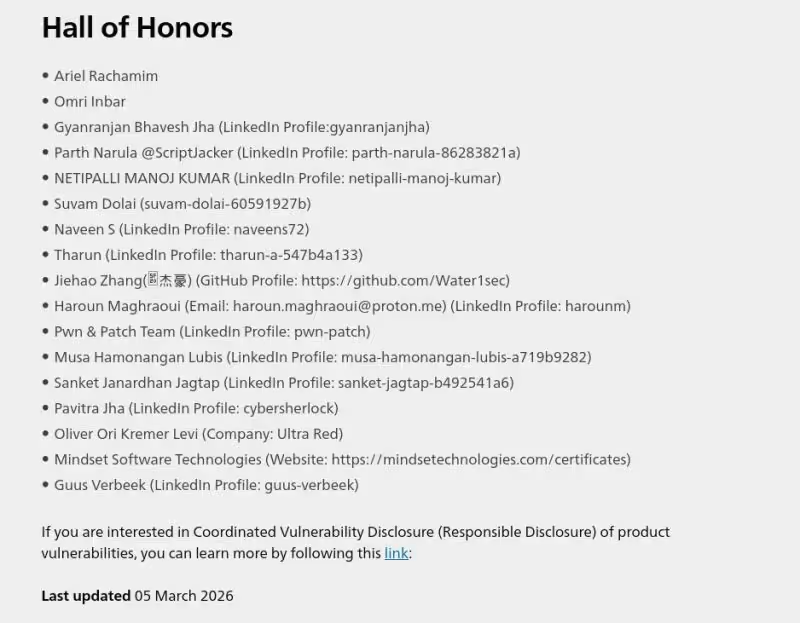
Happy to share that I’ve been recognized on the Signify (https://www.linkedin.com/company/signifycompany/) Hall of Fame for responsibly reporting a security vulnerability discovered during independent security research. Appreciate the Signify (https://www.linkedin.com/company/signifycompany/) security team for their professional handling of the report and dedication to improving security. Responsible disclosure is an important part of strengthening the security ecosystem, and I’m glad to contribute. https://www.signify.com/global/product-security/coordinated-vulnerability-disclosure/hall-of-fame #CyberSecurity (https://www.linkedin.com/search/results/all/?keywords=%23cybersecurity&origin=HASH_TAG_FROM_FEED) #BugBounty (https://www.linkedin.com/search/results/all/?keywords=%23bugbounty&origin=HASH_TAG_FROM_FEED) #ResponsibleDisclosure (https://www.linkedin.com/search/results/all/?keywords=%23responsibledisclosure&origin=HASH_TAG_FROM_FEED) #EthicalHacking (https://www.linkedin.com/search/results/all/?keywords=%23ethicalhacking&origin=HASH_TAG_FROM_FEED) #SecurityResearch (https://www.linkedin.com/search/results/all/?keywords=%23securityresearch&origin=HASH_TAG_FROM_FEED)
0
53
0
Security research update Happy to share that I’ve been recognized in the Philips Coordinated Vulnerability Disclosure Hall of Fame (2026) for responsibly reporting a security vulnerability. During security testing, I identified a vulnerability and reported it through Philips’ coordinated disclosure program. After verification by their security team, the issue was acknowledged and addressed. Moments like this highlight why responsible disclosure and collaboration between researchers and organizations are so important. Security research is not just about finding bugs — it’s about helping strengthen systems that people depend on every day. Grateful to the Philips security team for the acknowledgment and for supporting a transparent vulnerability disclosure process. On to the next bug. https://lnkd.in/dukTVr6t (https://lnkd.in/dukTVr6t)#CyberSecurity (https://www.linkedin.com/search/results/all/?keywords=%23cybersecurity&origin=HASH_TAG_FROM_FEED) #BugBounty (https://www.linkedin.com/search/results/all/?keywords=%23bugbounty&origin=HASH_TAG_FROM_FEED) #EthicalHacking (https://www.linkedin.com/search/results/all/?keywords=%23ethicalhacking&origin=HASH_TAG_FROM_FEED) #ResponsibleDisclosure (https://www.linkedin.com/search/results/all/?keywords=%23responsibledisclosure&origin=HASH_TAG_FROM_FEED) #SecurityResearch (https://www.linkedin.com/search/results/all/?keywords=%23securityresearch&origin=HASH_TAG_FROM_FEED) #AppSec (https://www.linkedin.com/search/results/all/?keywords=%23appsec&origin=HASH_TAG_FROM_FEED) #Infosec (https://www.linkedin.com/search/results/all/?keywords=%23infosec&origin=HASH_TAG_FROM_FEED)
0
69
0
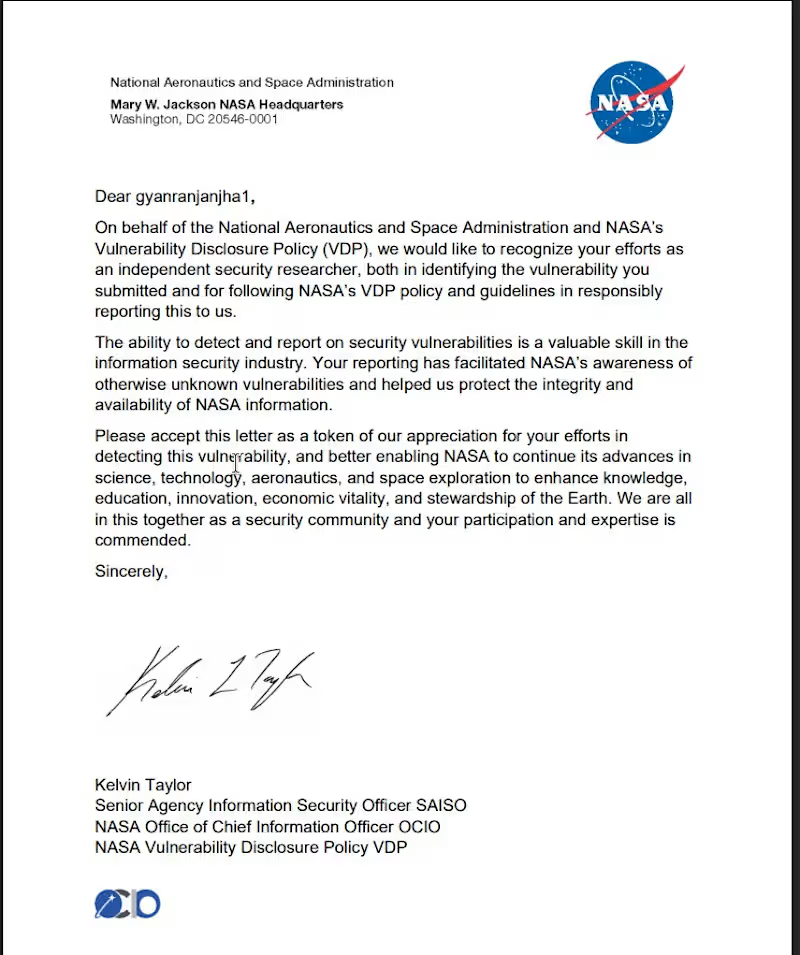
Grateful to be recognized in NASA's Vulnerability Disclosure Program Hall of Fame on Bugcrowd. As someone still early in my security research journey, this means a lot. Found a reflected XSS vulnerability, reported it, and it was accepted. Simple as that. Still a lot to learn, but this is a good reminder to keep going.Letter of Recognition should arrive after some time.
0
82
Ollama
(1)
Follow
Message
Rushikesh Sagar
Mumbai, India
"ML Engineer | RAG Pipelines · LLM Fine-Tuning · RL
New to Contra
Follow
Message
"ML Engineer | RAG Pipelines · LLM Fine-Tuning · RL
0
Financial RAG System — Fine-Tuned LLM, 100% Citation Rate
0
8
0
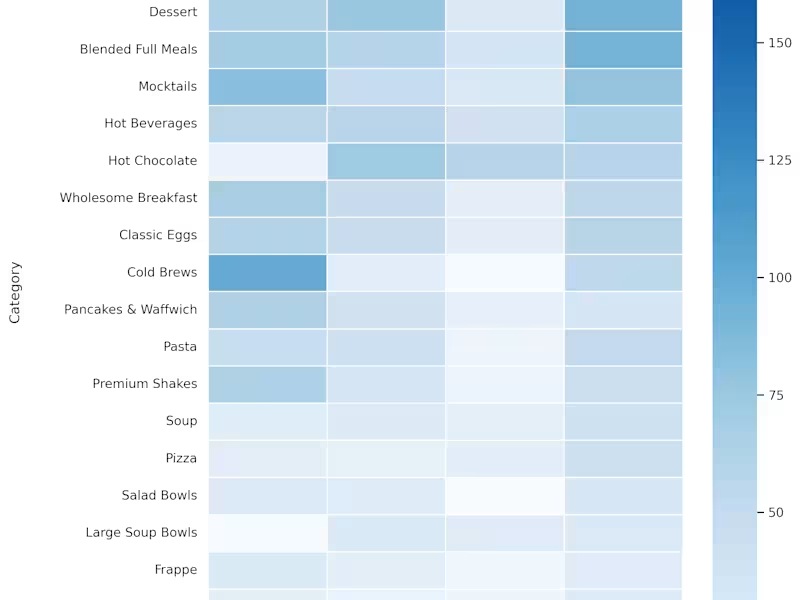
Blend Café Dynamic Pricing Recommendation Engine
0
7
0
Crypto Regime Detection — LSTM + GNN + PPO, 13 Assets
0
13
0
PokerForge — Full-Stack AI Poker Platform with PPO Bots
0
6
Ollama
(1)
Follow
Message
Explore people