Security Engineering Projects in London
Security Engineering Projects in London
Sign Up
Post a job
Sign Up
Log In
Filters
2
Projects
People
Message
0
Jason Smyth
pro
Microsoft Sentinel & Splunk ES Engineer for up to 6 months
0
13
Message
0
Guillaume Strohecker
I recently completed a security hardening pass on an AI-enabled mobile product. The most important issues weren’t exotic vulnerabilities. They were practical deployment risks: password reset race conditions missing abuse controls weak retention guarantees mobile backup exposure logging and CI gaps Each confirmed finding was fixed and backed by regression tests before the security baseline was marked PASS. One lesson stood out: security reviews are most useful when they produce evidence and actionable fixes, not just scanner output. I’m now offering focused 24-hour AI Agent Security Mini-Audits for founders and small teams. https://contra.com/s/2Z7YgYXU-ai-agent-security-mini-audit?r=guillaume_strohecker_6m06cchc
0
36
Message
0
Dimitris Pallis
Penetration Tester
0
47
Message
0
Aivar R.
Autonomous agents are dangerous without a custody layer. The Iron Wolf Advisor dock and OMNI Terminal allow for controlled, human-gated intake of new tasks. No workflow starts without explicit operator authority, and every intent is funnelled through a strict Service Gateway with non-bypass able decision manifests.
0
48
Message
0
Moyosore Ogunjale
Zero Trust Security Hardening
0
23
Message
0
Deval G
Cost Optimization Managed Service
0
7
Message
0
Guillaume Strohecker
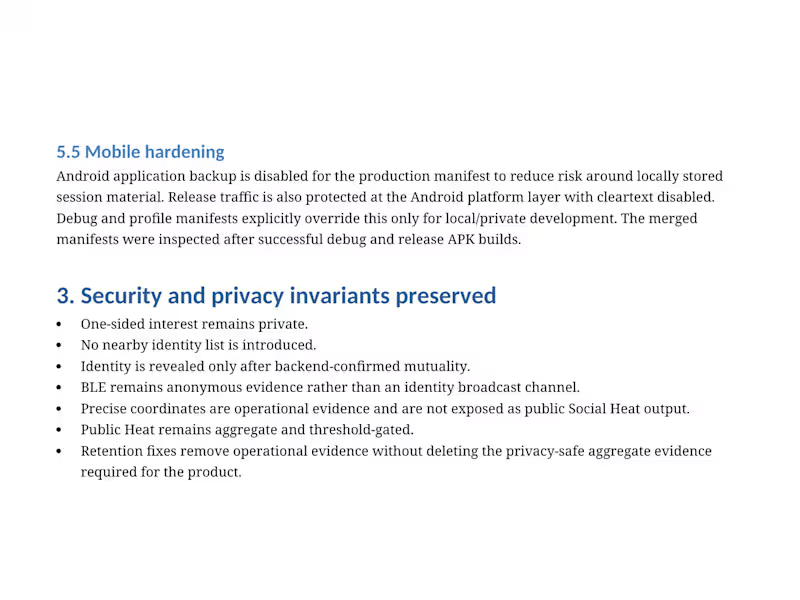
Mobile Security & Privacy Hardening Security hardening focused on mobile platform protections and privacy-preserving behavior. Android application backup was disabled to reduce risk around locally stored session material, and release builds were hardened to block cleartext traffic while keeping local development support isolated to debug/profile builds. The review also verified that BLE remains anonymous, one-sided interest stays private, precise coordinates are not exposed publicly, and Social Heat remains aggregate and threshold-gated.
0
19
Message
0
Dimitris Pallis
Offensive Security Engineer
0
44
Message
0
Aivar R.
Regulated sectors need to know exactly what an AI agent did and why it was authorized. This Evidence Vault displays a fully orchestrated proof chain - from browser snapshot to data transformation to client report - each step hash-verified and cryptographically linked. It provides the immutable audit trail that CISOs and regulators demand.
0
73
Message
0
Moyosore Ogunjale
SSO & SCIM Rollout
0
34
Message
0
Guillaume Strohecker
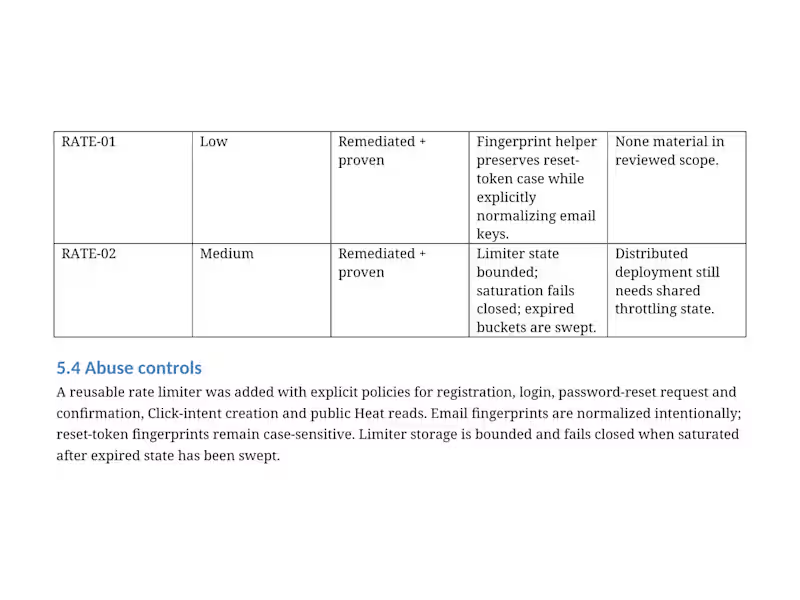
API Rate Limiting & Abuse Protection Security hardening focused on API abuse resistance. Rate limits were added to registration, login, password-reset request and confirmation, Click Intent creation, and public Heat reads. The limiter was designed with bounded state, explicit email normalization, case-sensitive reset-token fingerprints, expiry sweeping, and fail-closed behavior under saturation. Regression tests verified throttling behavior and recovery.
0
26
Message
0
Dimitris Pallis
Penetration Testing Expert
0
25
Message
0
Aivar R.
This is not a reporting tool. This is a read-only command center that provides real-time observability over a multi-department AI pipeline. It manages worker health, intake queues, and runtime control, ensuring that every AI agent action is governed by human-gated approvals and append-only audit ledgers.
0
93
Message
0
Guillaume Strohecker
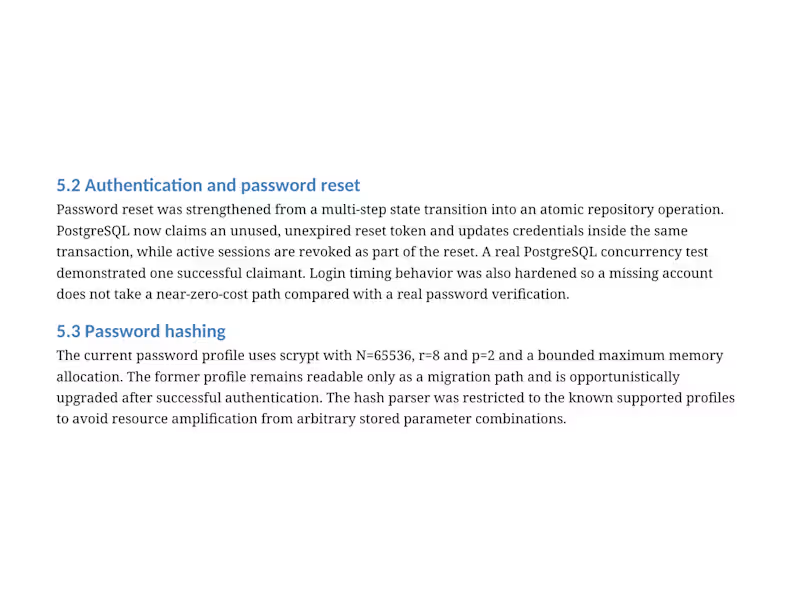
Authentication & Password Reset Hardening Security hardening focused on authentication and account recovery. The work included stronger scrypt password hashing, legacy-hash migration, login timing protections, atomic password-reset token consumption, and session revocation after reset. PostgreSQL concurrency and regression tests verified that a reset token can only be successfully consumed once and that authentication behavior remains safe under failure conditions.
0
31
Message
0
Guillaume Strohecker
AI Agent Security Audit — Click Click
0
36
Explore projects