The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

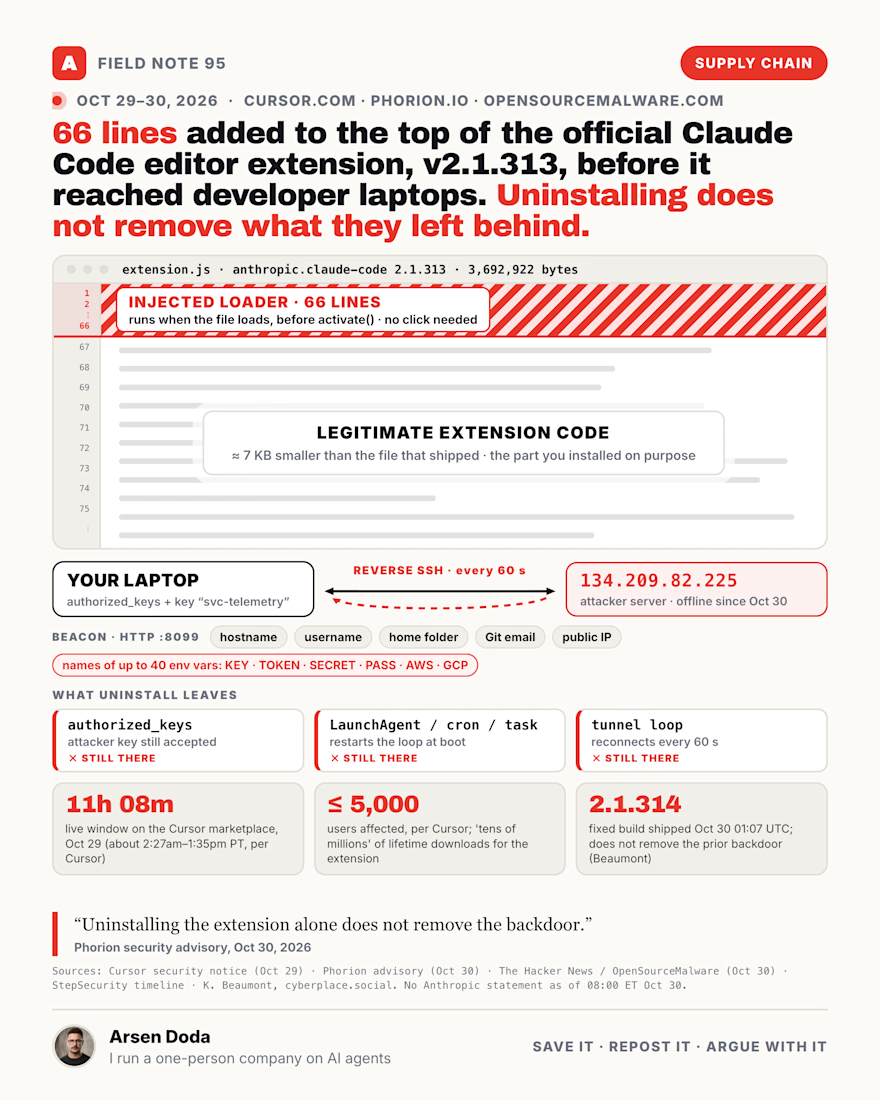
66 lines of code.
That is what an attacker added to the top of the official Claude Code editor extension, version 2.1.313, before it went out to developer laptops yesterday.
Uninstalling the extension does not remove what those 66 lines left behind.
Cursor's security notice, verbatim: the trojanized build was live "between about 2:27am PT and 1:35pm PT" on October 29. "At most 5,000 users were affected, and we will reach out directly." Cursor says the build "was not developed by Anthropic" and rebuilt its marketplace.
Phorion, the endpoint-security firm that published the teardown, on what the loader does:
→ Runs when the editor loads the file, before the extension even activates. No click needed.
→ Appends an attacker's SSH key, labelled "svc-telemetry", to your authorized_keys.
→ Opens a reverse SSH tunnel to 134.209.82.225, retrying every 60 seconds.
→ Installs itself as a LaunchAgent on Mac, a reboot cron job on Linux, a scheduled task on Windows.
→ Phones home with hostname, username, home folder, Git email, and the NAMES of up to 40 environment variables matching KEY, TOKEN, SECRET, PASS, AWS or GCP.
Not the values. The names. A shopping list for the next visit.
The fix, 2.1.314, shipped overnight. Security researcher Kevin Beaumont says he confirmed the replacement versions "do not remove the prior backdoors and recon activity". Clean version in, back door still open.
Anthropic had not published a statement when I wrote this. Cursor had. Phorion had. OpenSourceMalware, which counted the 66 lines, had.
I run a one-person company on AI agents. Tools like this one sit between me and everything I ship. This morning, before writing a word, I checked my own machine against the published indicators: the key, the LaunchAgent, the tunnel. Clean. A few minutes.
That is the whole lesson. The extension auto-updates. You did not choose version 2.1.313. Your editor chose it for you, at 2:27am.
Rule 1: Check, do not assume. Search authorized_keys for "svc-telemetry". If it is there, uninstalling changes nothing: run the vendor's remediation script and rotate every credential that machine could reach.
Rule 2: Auto-update is a trust decision, not a convenience setting. For anything that runs code on the machine that holds your keys, pin the version and update on a schedule you read.
Rule 3: The names of your secrets are secrets. The loader skipped the values and took the variable names. An inventory of what you have is the first stage of losing it.
Supply-chain attacks are not new. This one matters because the compromised thing is the AI tool itself.
The update was automatic.
The cleanup is not.
Did you check your machine today? Yes or no. 👇
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

Casemate: making malware analysis feel calm instead of scary
Cybersecurity websites usually look the same: black background, green code, a hooded guy. I wanted to try the opposite for Casemate, a concept for a malware analysis tool.
The idea is simple: the product keeps a suspicious file in a sealed chamber and watches what it does. So I put a bug frozen in amber in the middle of a canyon. It’s dangerous and under control at the same time, and you get it without reading a word.
Then I made sure the page still works for a security lead who wants facts. The stats sit right next to the headline: threats isolated, latency, endpoints covered.
The hardest part was keeping it warm without losing trust. I stayed with one terracotta colour, wide capitals and mono labels, so it reads like a serious tool and not a poster.
I’m taking on new projects for SaaS and tech teams. If you have a product that’s hard to explain in one glance, send me a message.
What do you think, would you trust a security product with a canyon on the homepage?


I love it! It feels so calm, and I would definitely try it! This is amazing, Kris. I never thought cybersecurity could be this cool ❤️🔥

Friday Question: When Did You Last Check Your Website on Your Phone? 📱
Not on your laptop.
Not in the editor preview.
On your actual phone. The way your customers see it.
This week I did exactly that with my own website. And I didn’t love what I saw.
The menu button was plain. The dropdown felt like an afterthought. And the most important button, “Let’s Talk,” was just another line of text in a list.
So I rebuilt it.
✔ A clearer menu button
✔ A proper slide-out menu
✔ A call-to-action you can’t miss
Nothing was “broken.” It just wasn’t helping anyone take the next step.
Here’s a 60-second test you can do right now:
→ Open your website on your phone
→ Tap the menu
→ Try to contact yourself
How many taps did it take? Did anything feel awkward?
Friday question: when did you last check your website on your phone? And what did you notice? 👇