The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

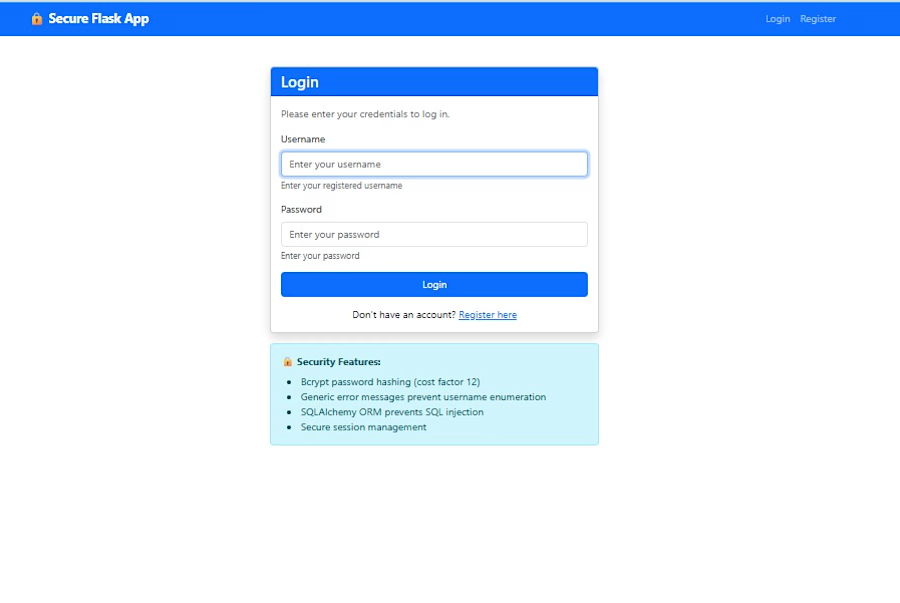
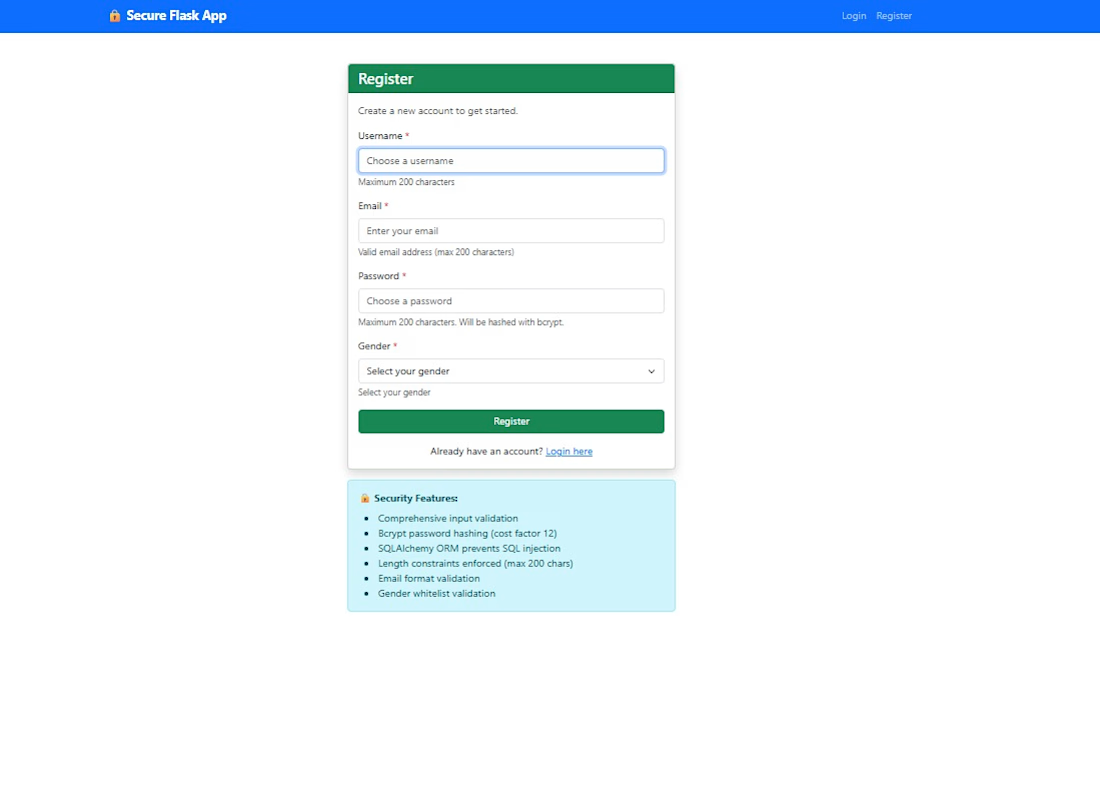
Secure Authentication System — SQL Injection Prevention🚀🧑🏻💻
I built a secure user authentication system from the ground up to demonstrate how to properly defend a web application against SQL injection — one of the most common and dangerous web vulnerabilities (OWASP Top 10).
The project includes two versions of the same app: an initial PHP implementation and a production-grade rebuild in Python/Flask, so the before-and-after security improvements are easy to see and explain.
What I delivered:
Eliminated SQL injection risk by replacing raw queries with parameterized queries and an ORM (SQLAlchemy)
Implemented secure password storage with bcrypt, including automatic migration of legacy plaintext passwords on login
Added thorough input validation and sanitization across every form
Wrote 230+ automated tests (unit, integration, and property-based tests with Hypothesis) to formally verify the app can't be exploited through its inputs
Set up database migrations (Alembic) and a Dockerized test environment
Why it matters:
This isn't just a demo — it's a working reference for how real applications should handle authentication and user input safely. I can apply the same approach to secure an existing app, audit code for injection risks, or build new features with security built in from day one.
Tech: Python, Flask, SQLAlchemy, Bcrypt, PHP, MySQL, pytest, Hypothesis, Docker


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

$10K earned on Contra. 🎉💸
Grateful for every client who took a chance on me. This is just the beginning. More great products, more real partnerships, more milestones to hit. 🙌
Thank you to everyone who's been part of it. Onward. 🚀
#10k #contraearnings #Freelance #Webflow #Framer #Webdesign


Congratulations nice job 🎉🎉


Sharing a few recent projects 👋
It has been an exciting few months! A good mix of industries in this one, from an arcade and a mini golf hire company to car inspections and hospitality.
Excited to see what the rest of the year brings!


I should try adding blur also when slide goes back or a 0.1 delay in upcoming one,
the mid transition phase is bothering me


Hero exploration for an AI Startup - Orbio.
- Editorial serif caps
- Marble statue as the hero
- A live 01 grid reacting to mouse
- Different highlight color for each division


a different highlight colour per division is such a clean system move. the live 01 grid reacting to the mouse is a nice touch too
