The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

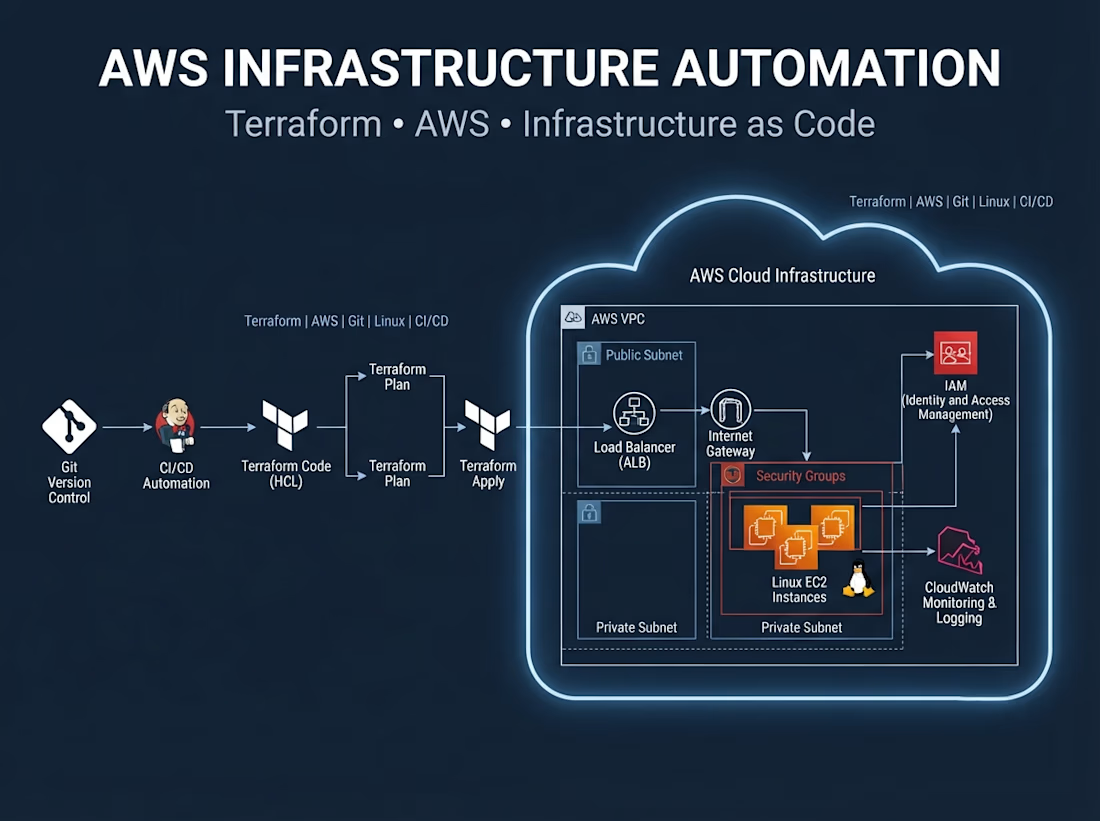
Automated AWS infrastructure provisioning and configuration using Terraform, with an emphasis on repeatable infrastructure, resource configuration, environment consistency, and reliable cloud deployment practices.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts

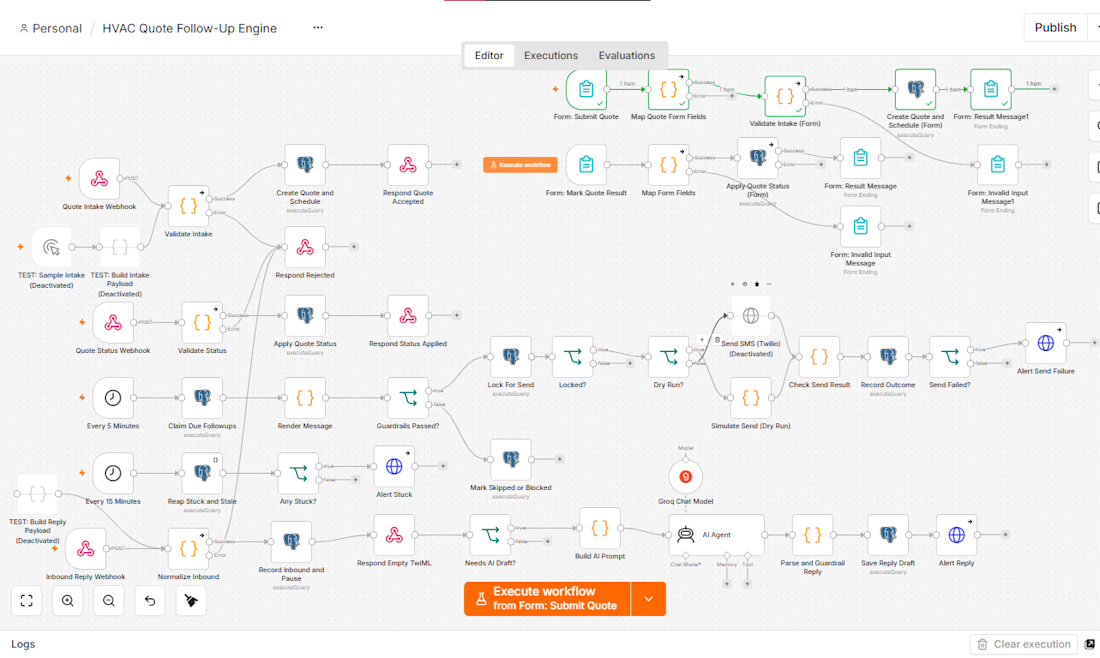
Quote Follow-Up Automation for HVAC & Plumbing
Most home-service quotes don’t get rejected, they just go quiet. I built a system that follows up on them automatically.
What it does
Takes each quote through a simple form
Schedules up to 8 timed texts over 30 days
Stops instantly on a reply, a STOP, or a booked/lost update
Uses AI to draft replies to objections, with a human approving every one
Built with safety first
No duplicate texts, even when processes overlap
Only contractor-approved wording is sent
Texts go out only during local business hours
Opt-outs are honored immediately
Stack: n8n, Postgres, Groq, Docker, Twilio
Status: built and tested end to end, ready to pilot.
I build automation systems like this for service businesses. Message me if you’d like one for yours😊 .



Would you run a command without knowing what it could do?
A copied installation script. An automated workflow. A shell command suggested by AI.
Convenient? Yes. Worth checking before execution? Absolutely.
That’s why I built SafeShell, an open-source tool for inspecting commands, applying security policies, and running permitted commands with sandboxing on Linux.
The goal: help developers and engineering teams work faster with more control over what they execute.
Explore the code, try it, and share your feedback:
https://github.com/HamzaGhebriche/SafeShell
Building automation or CI/CD workflows that need stronger security controls? I’m available for freelance projects in DevSecOps, secure automation, and cloud security. Let’s talk through Contra.




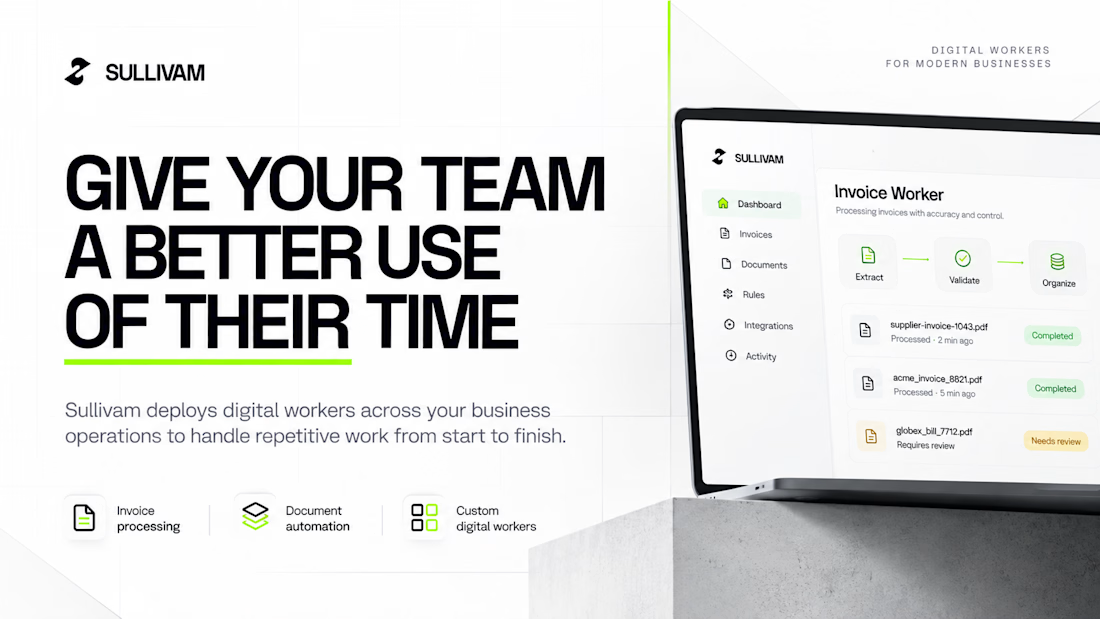
Sullivam is a SaaS platform that helps businesses automate repetitive tasks and simplify their daily operations.
As CTO, I lead the technical development, from software architecture and backend systems to integrations and intelligent automation.
The goal is simple: build reliable technology that helps businesses spend less time on manual work and more time growing