The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

A cleanup on my Mac turned into a CI optimization across several projects.
It started with 30 GB of npm cache and another 20 GB in old node_modules folders. After recovering roughly 50 GB, I moved several projects to pnpm.
Updating CI for the migration led me to review the pipelines themselves. I found duplicate stages and Docker images carrying build-time dependencies and unnecessary files into production.
I removed the duplicate work and switched to multi-stage Docker builds, keeping only what each app needed at runtime.
On some projects, average CI runs dropped from 6–7 minutes to about 2. A few longer pipelines went from 15–16 minutes to around 6.
The pnpm migration also sped up dependency installs and gave me more control over dependency install scripts.
What’s had the biggest impact on build times in your projects?
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started






Related posts

Building a Startup? Don't waste $2000 on a backend.I will build your Secure Backend in FastAPI for $250.
✅ Login + JWT Auth + Role Access
✅ PostgreSQL Database with ACID Safety
✅ Payment-safe APIs + Docker Setup
✅ Swagger Docs + TestingDelivery in 1 week.
I have 2 slots open this week. DM me your idea, I will tell you the exact plan.


The danger of SaaS Git dependency: When a vendor outage, account suspension, or price hike halts your entire engineering lifecycle.
Most modern technology companies anchor their entire software supply chain—source code, CI/CD pipelines, secret management, package registries, and issue tracking—to a single external SaaS provider (GitHub or GitLab).
While convenient, this model creates massive single-point-of-failure vulnerabilities and compliance liabilities:
1. Cascading Outage Disruption: When the SaaS provider suffers an incident, your developers cannot push code, CI pipelines cannot run security scans, and production emergency hotfixes are completely paralyzed.
2. IP Sovereignty & Data Exfiltration: Hosting sensitive proprietary algorithms, enterprise encryption keys, or regulated financial/healthcare intellectual property on multi-tenant commercial clouds carries inherent data exposure and regulatory audit friction.
3. Unpredictable Tier Pricing: Public SaaS platforms continually monetize developer seats, build minutes, and artifact storage, driving unexpected 40%+ operational cost increases.
The modern solution for resilient engineering organizations is deploying a self-hosted, sovereign Git forge (such as Forgejo or Gitea) integrated with dedicated, air-gapped CI/CD runners:
• Mathematical Resource Efficiency: Forgejo is a lightweight Go binary with a PostgreSQL backend. It delivers full Git hosting, PR reviews, issue management, and container registries consuming under 250MB of RAM—compared to 16GB+ for heavy alternatives.
• Native Actions Compatibility: Run standard, modern CI/CD workflows utilizing your existing YAML configurations with dedicated, bare-metal ephemeral execution runners.
• True Data Sovereignty: Store all git repositories, artifacts, and build logs on your own encrypted storage volumes (NVMe/Ceph) behind your zero-trust network perimeter.
• Hybrid Synchronization: Mirror external open-source dependencies locally for air-gapped security, while maintaining automated bidirectional replication to public repos when desired.
Take back control of your source code, your intellectual property, and your developer workflow.
Deploy a production-hardened sovereign Git forge with our 1–2 week Sprint on Contra:
#DevOps #Infrastructure #Security #CyberSecurity #Automation #Linux #SRE #Architecture

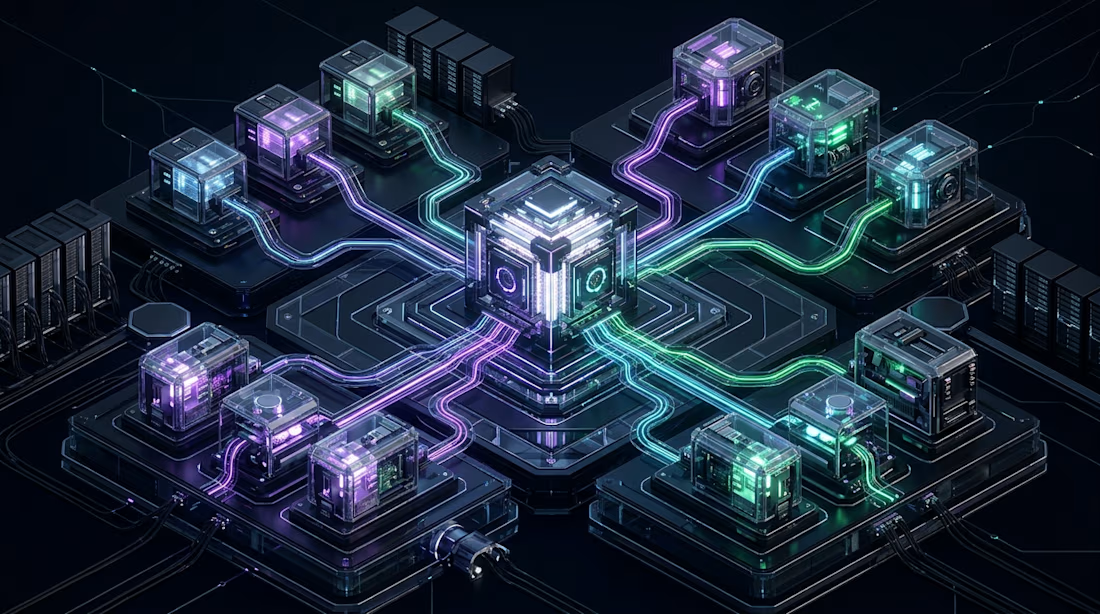

i'm loving designing and building architecture studio sites, and specially the experience with
@framer is insane