The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Mobile Application Pentest - Android Banking App
Conducted a full black-box mobile penetration test on an Android banking application following OWASP MASTG methodology. Identified 17 vulnerabilities including 5 critical findings: hardcoded AES encryption keys in SharedPreferences, SSL pinning bypass via Frida instrumentation, root detection bypass via LIEF binary patching, exported Activities without permission checks, and sensitive data exposed in Logcat.
Delivered MASTG-aligned report with CVSS scoring and PoC code for all critical findings.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started







Related posts

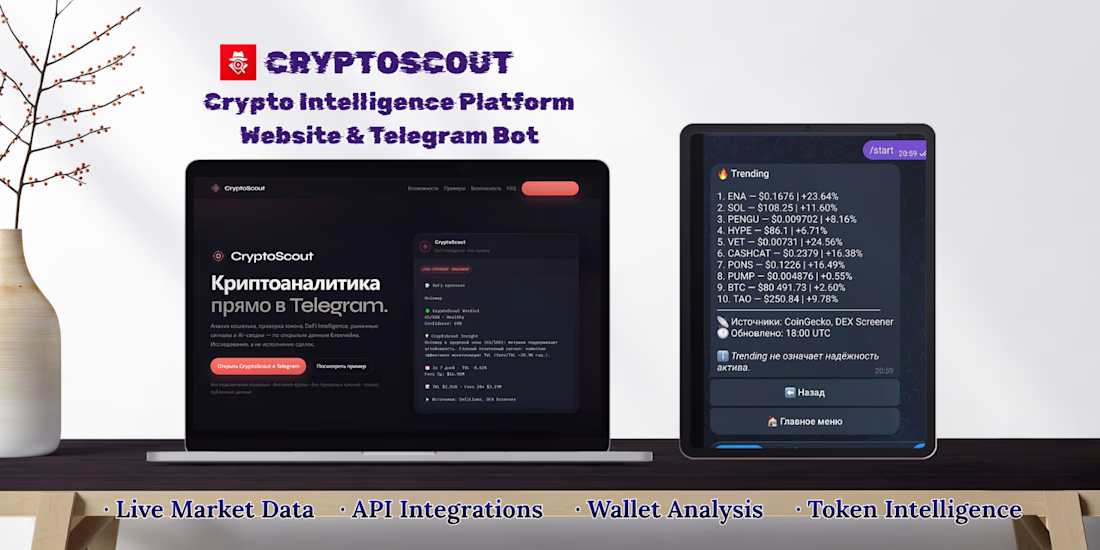
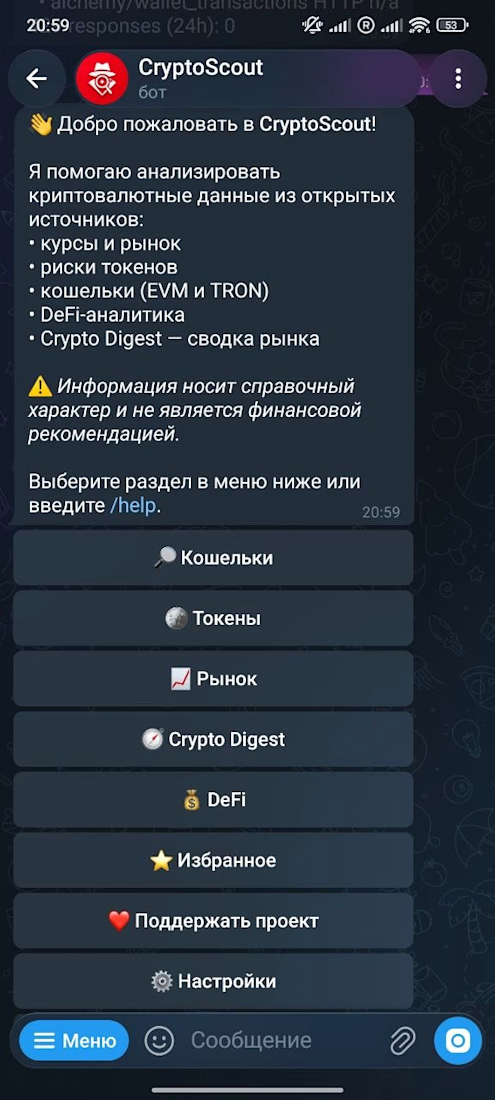
CryptoScout is a Telegram crypto assistant that provides users with tools for checking wallets and tokens, monitoring portfolios, and accessing useful crypto information directly through Telegram.

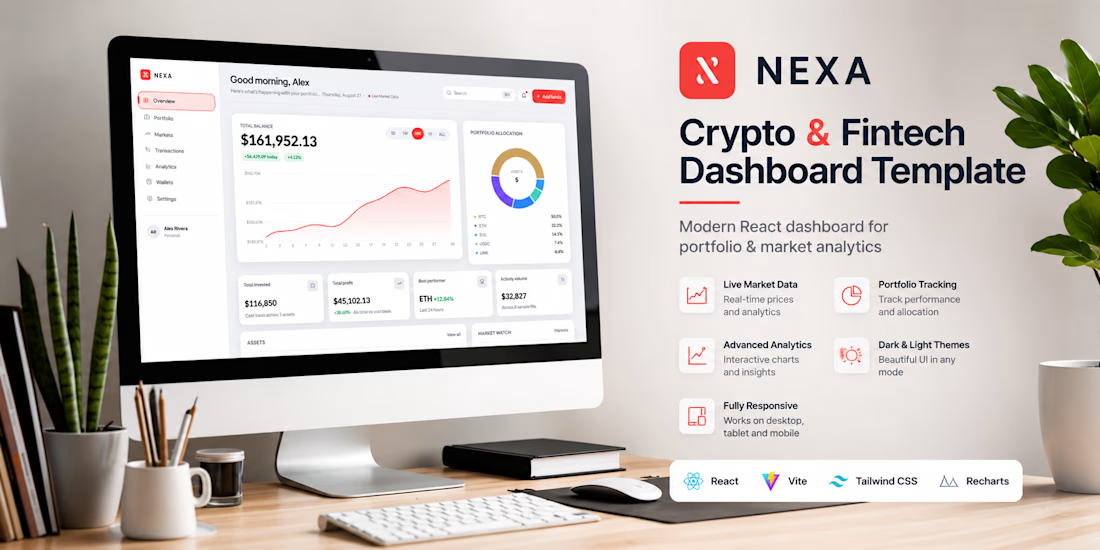
NEXA is a modern crypto portfolio dashboard designed to provide a clear overview of digital assets, portfolio performance, market data, and key statistics in one interface.

OSINTGuard — AI-Powered OSINT Exposure Detection
A pre-publication security tool that detects sensitive information in text and screenshots, explains potential exposure and helps users create safer content before publishing.

