The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

The future is not just AI that can answer you.
It is software that can act, transact, verify, coordinate, and work with other software.
That future needs infrastructure built for machines from the start.
That is what I’ve been building.
CrossingKey
intelligence is the standard.
#MCP #ModelContextProtocol #AIAgents #AgenticAI #x402 #MachineCommerce #Base #CrossingKey

Agents that can transact and coordinate with other software is where it gets interesting, and also where identity and permissions get messy fast. How are you handling scoped access when one agent acts on a user's behalf inside another service? Short-lived tokens, per-action approval, something else?
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started







Related posts


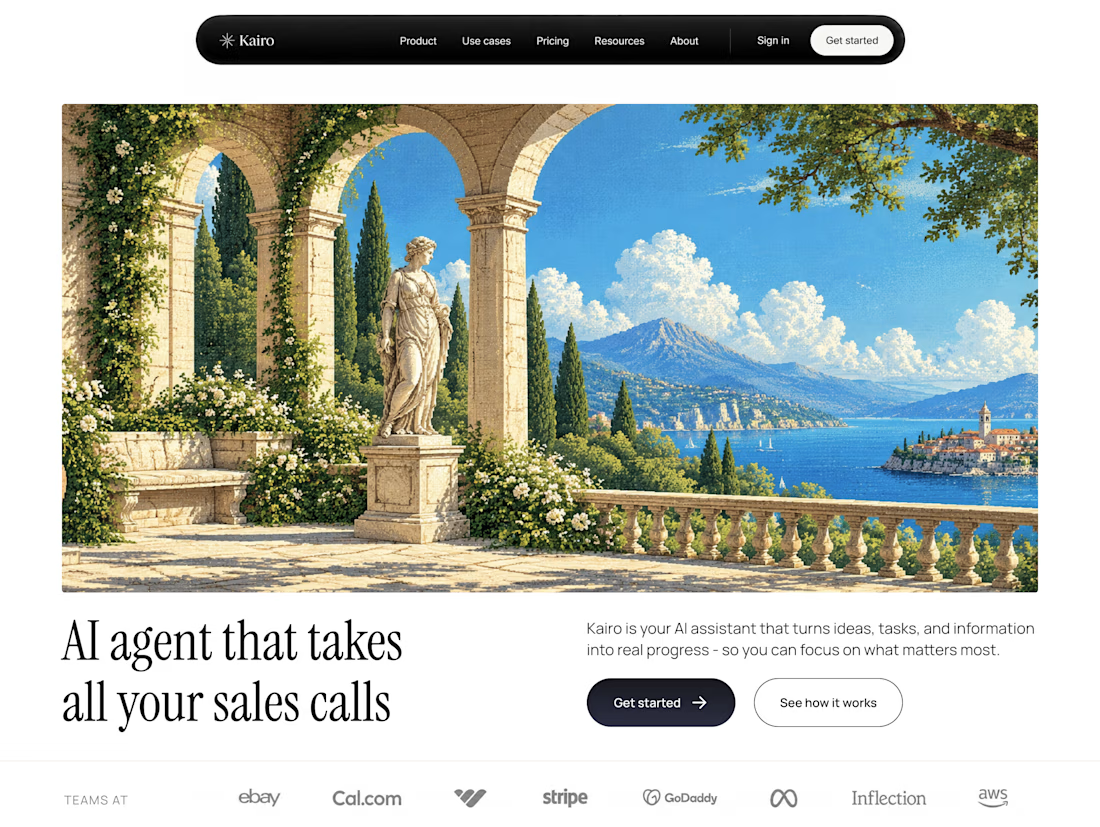

The visual storytelling is good.

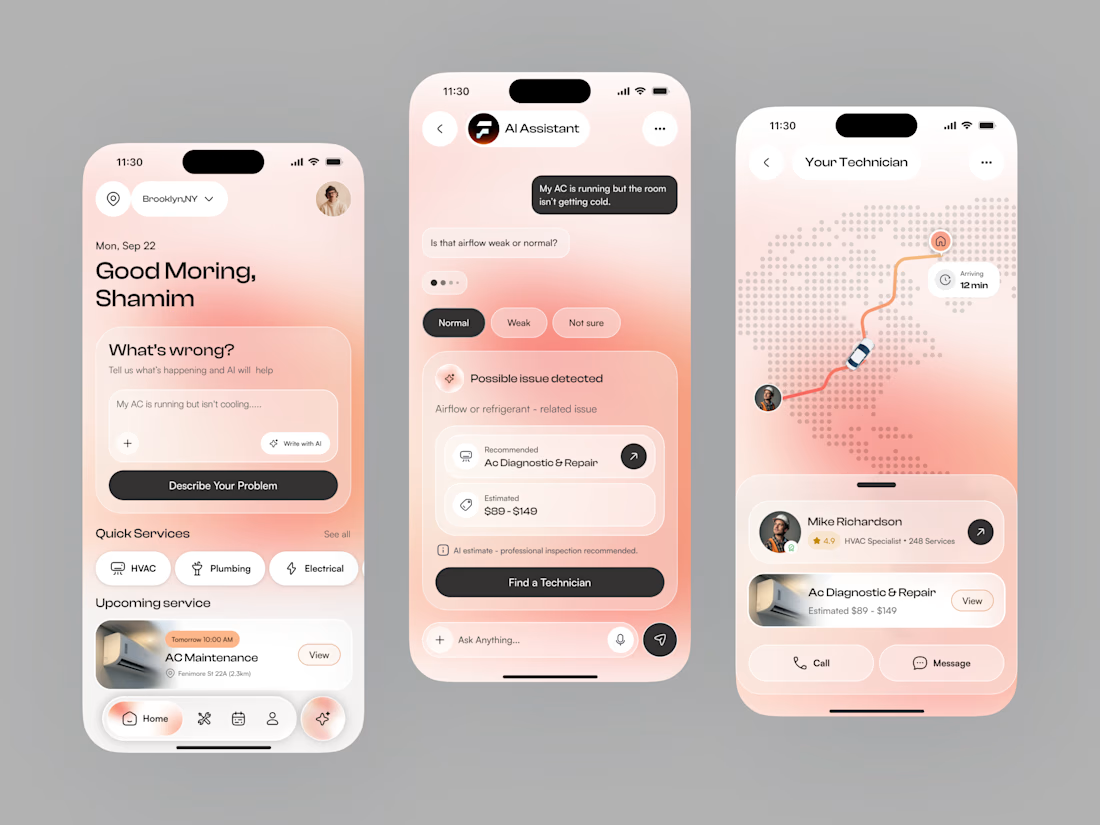
AI Home Services App — Smart Technician Booking & Repair
A premium AI-powered home services app designed to simplify how people diagnose home problems, find the right service, and book qualified technicians.
The product uses AI to turn a simple problem description into a clear service recommendation — helping users move from “What’s wrong?” → “What do I need?” → “Who can fix it?”
Key Experience
→ AI-powered problem diagnosis
→ Text, voice & photo input
→ Smart service recommendations
→ Technician discovery & booking
→ Transparent service information
→ Real-time technician tracking
→ Premium, intuitive mobile experience
The concept is designed for founders building AI home-service platforms, technician marketplaces, repair apps, and SaaS products where reducing friction and improving the booking experience can create a stronger customer journey.
Role: Product Designer
Focus: AI Product Design · UX/UI · Mobile App Design · Service Marketplace



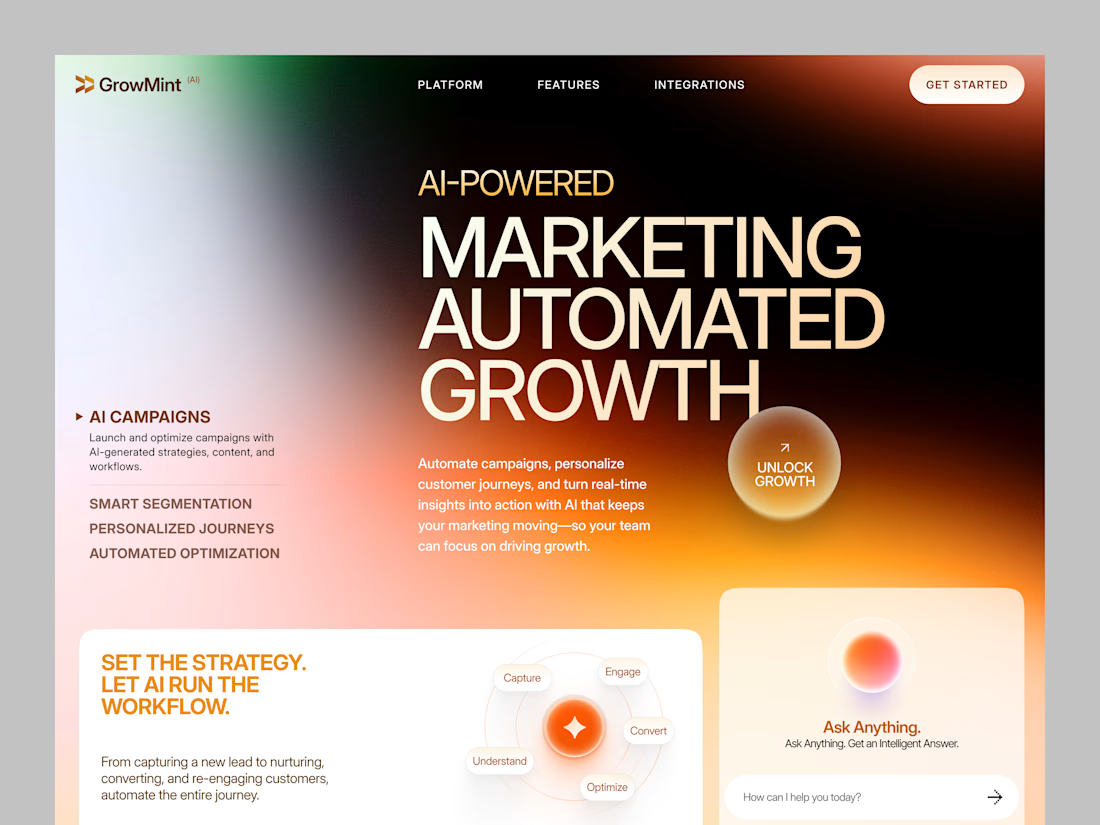
GrowMint AI - AI Marketing Automation Website
An AI marketing automation experience designed around the needs of marketing teams, growth marketers, and digital businesses.
The interface brings campaign management, customer journeys, analytics, and AI-driven optimization into a focused SaaS product experience, making complex automation easier to understand and navigate.

Nice design