The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

4 EU AI Act readiness checks most companies are skipping right now:
1. "Our vendor handles compliance."
Under Article 28, deployers carry their own obligations separate from the provider. Your vendor's CE mark doesn't cover your use case. You're a deployer, not a bystander.
2. No documented human override process.
Article 14 requires more than logging. There has to be a process for humans to monitor and override AI outputs, and someone has to own it. "We can see the output" doesn't count.
3. Risk classification treated as a checkbox.
If you retrain the model, change its inputs, or deploy it in a new context, the risk level needs to be reassessed. Most teams do it once and forget it. Auditors won't.
4. No data provenance trail.
Article 10 requires training and validation data to meet quality criteria, including where it came from and how it was cleaned. If you can't answer that question in 5 minutes, that's the gap an audit will find first.
None of these are complicated to fix once you spot them.
What's the one your team assumed was already covered?
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

As a freelancer, keeping everything that runs your business organized gets harder as the business grows. Money coming in and going out, client details, project files, new leads, job applications. It adds up fast, and it gets overwhelming.
So I built Rendr, a personal AI-powered macOS app that keeps my whole business in one place, so I spend less time managing and more time designing.
What it does:
• Command Center: a daily briefing of what needs my attention, and why
• Pipeline: tracks leads from first contact to signed work, with AI-drafted proposals and follow-ups
• Clients: every client's history, files and notes in one hub
• Money: payments, open invoices and payouts, synced from Contra
• Job search: Contra jobs plus open job boards, matched to my skills and rate
• Applications: tailored resumes, cover letters and pitches, written only from my real experience
• Site audits: reviews a prospect's website and turns the findings into a pitch email in one click
• Work library: tagged portfolio files, with the best samples suggested for each pitch
• Backups: automatic, every day, to Dropbox
It runs on my Mac, and it never sends an email, invoice or message on its own. I review everything first.
Still building, with more to come.


Looks amazing..is it a native app ?


When I worked as a guide, booking was one of my biggest pain points: constant back-and-forth, checking availability, handling changes, payments, confirmations, and trying not to lose track of who was coming when.
So I built HERODOT - History of Mystery around exactly that problem.
A visitor can simply describe what they want, and HERODOT interprets the request, recommends the best-fit historical tour, checks availability, handles the booking and payment, and confirms everything. On the guide side, the Guide Desk brings together guests, routes, payment state, mobility notes, local conditions, briefings, and only the exceptions that genuinely need human attention.
It is basically the booking workflow I wish I had when I was guiding.
And who knows — maybe tomorrow I’ll wander off into the unknown again. If I do, at least the bookings will be sorted.


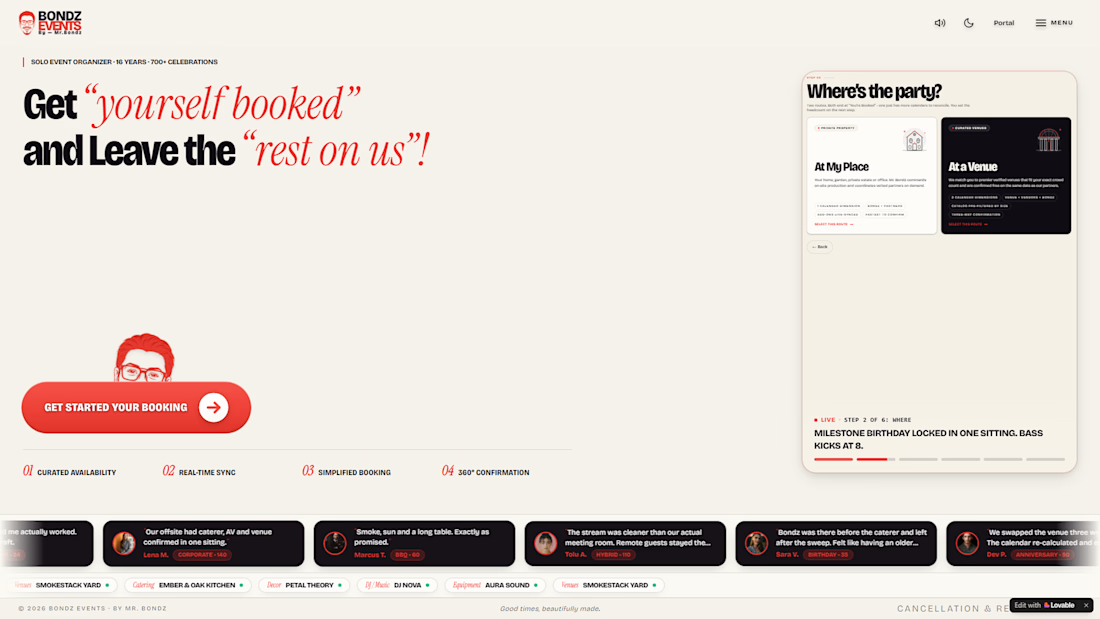
Planning a milestone event shouldn’t feel like running an air traffic control tower from your inbox.
You know the drill: you want to celebrate a wedding, corporate events, milestone birthday, or anniversary. You find a venue you love, but their open Saturday doesn't work for the caterer. You scramble to find another date, but now the caterer is booked. Three weeks, nine different vendor quotes, and 30 back-and-forth emails later, you’re exhausted before the party even starts. The worst.
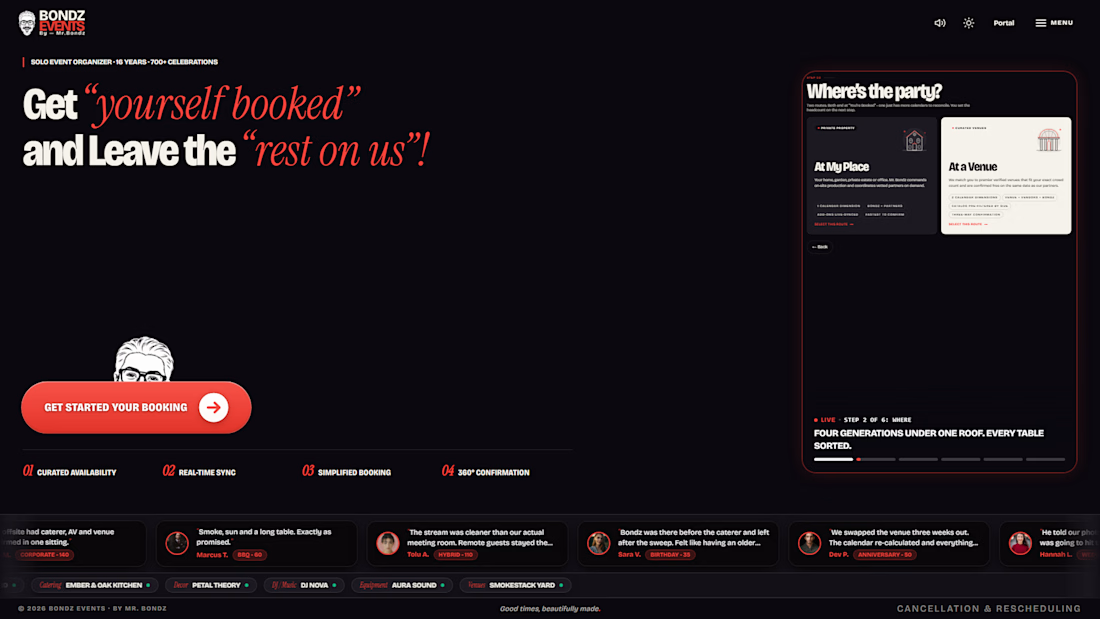
So I built Bondz Events. The problem I wanted to solve: eliminate multi-vendor booking chaos and turn high-touch event planning into a synchronized, single-sitting digital experience.
See it in action here: https://bondzevents.lovable.app
The booking canvas lets clients pick their vibe, select a venue or home setup, and assemble their curated vendor dream team, from live grill catering and craft lighting to DJs and cinematics. Behind the scenes, an intelligent 75-day multi-calendar availability engine checks everyone's schedules simultaneously. A date turns green only if the venue, Mr. Bondz, and every single selected partner are 100% available, zero double-booking, zero post-deposit cancellations. Everything wraps up with a high-contrast digital signature pad and with 360° confirmation feedback the moment you tap to lock in your deposit.
Behind the curtain, the dual-sided Owner's Portal keeps the entire ecosystem in sync. Mr. Bondz has a master command center to monitor live revenue, confirmed dispatches, and incoming requests. Meanwhile, partners have their own dedicated view to inspect work orders and toggle blackout dates that update front-end client availability in real time.
Built and deployed natively with Lovable and engineered with Web Audio synthesis and editorial visual.
Less phone tag for the client, zero scheduling conflicts for the vendors.
The celebration is bespoke. Locking it in shouldn’t be a headache. 🥂
See Social posts:
X: https://x.com/mdrafat007/status/2105906188852539804?s=20
LinkedIn: https://lnkd.in/p/gqiMf_he
See the demo walk through and the build process below.

Loved the design and thought behind this. The tactile interaction with sounds really a cherry on top. The amount of details goes into the entire booking process really enhances the booking procedure to another level. Keep up the good work brother ❤️