The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

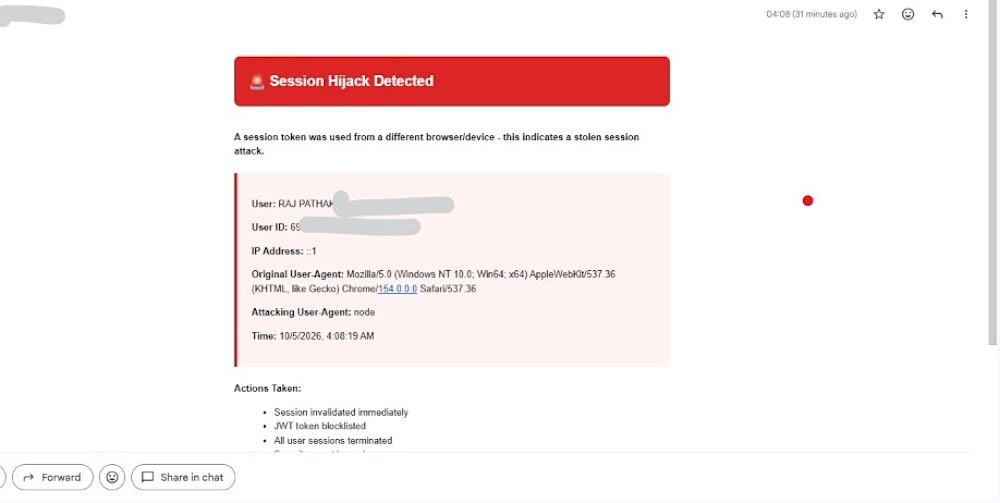
I got a "CRITICAL: session hijack detected" email at 4am. it was my own test, but the system didn't know that. it killed the session and blocklisted the token on its own
On every project i set up a stack of security checks before launch: session fingerprinting, rate limits, server-side payment verification and more. i'm no security guru, it's just a habit i never skip
AI tools are great for speed. but i've seen what happens when nobody checks what's under the hood
What's one security check you never skip before handing a project to a client? I am curious what's on your list
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

Then: 1 month, 1 template.
Now: 1 week, 15 templates.
Same designer, different workflow.
I wrote up how I built no-code.supply: fifteen website templates, each with its own brand, in HTML and React, and some in Framer too. Claude Code did most of the typing. I did the directing.

no-code.supply
How I built 15 website templates with an AI coding agent in a week
How I built 15 AI-ready website templates with Claude Code in a week: the workflow, the quality bar, and why a template is only the starting point.

Going from one template a month to fifteen a week is wild. How much of the design direction did you still do by hand?

Rosso Archive — Gallery Website
Rosso Archive is a website for a contemporary art gallery — a calm, editorial space built around a single idea: twenty-four works.
We kept the interface quiet so the images can speak. Monospaced captions, a soft grey palette and generous white space give the archive the feel of a printed catalogue, while small interactions make it feel alive online.
What's inside:
— Index list view with a live preview of the hovered work
— Grid view with a colour-on-hover state for the active piece
— Work detail page with specs, description and related works
— Seamless zoom-in transitions between artworks and screens
Have a project in mind? Let's talk.


Great work, Dmytro!

Building hero sections that don't just look cool, but actually convert. 🚀
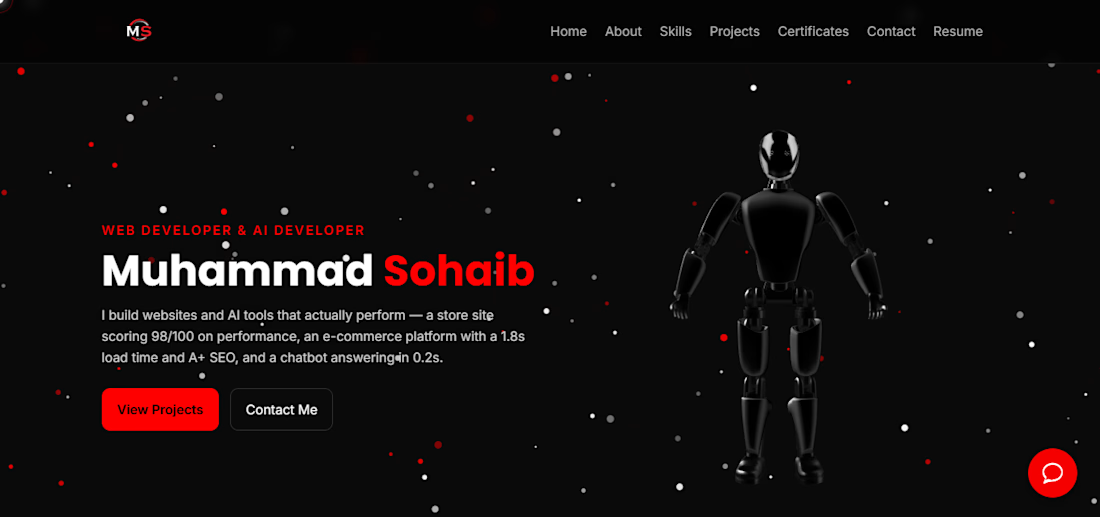
Just finalized the new hero layout for my portfolio. Blending dark aesthetics, interactive 3D elements, and real performance metrics:
⚡ 98/100 Performance Score
⚡ 1.8s Page Load Time
⚡ 0.2s AI Chatbot Latency
High-performance Web & AI engineering is all about combining immersive visuals with zero-compromise speed.
What do you think of this layout?
The robot on the right balances the dark hero nicely. Is the 3D model lazy loaded?