The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Wound up on this app development project!🚀


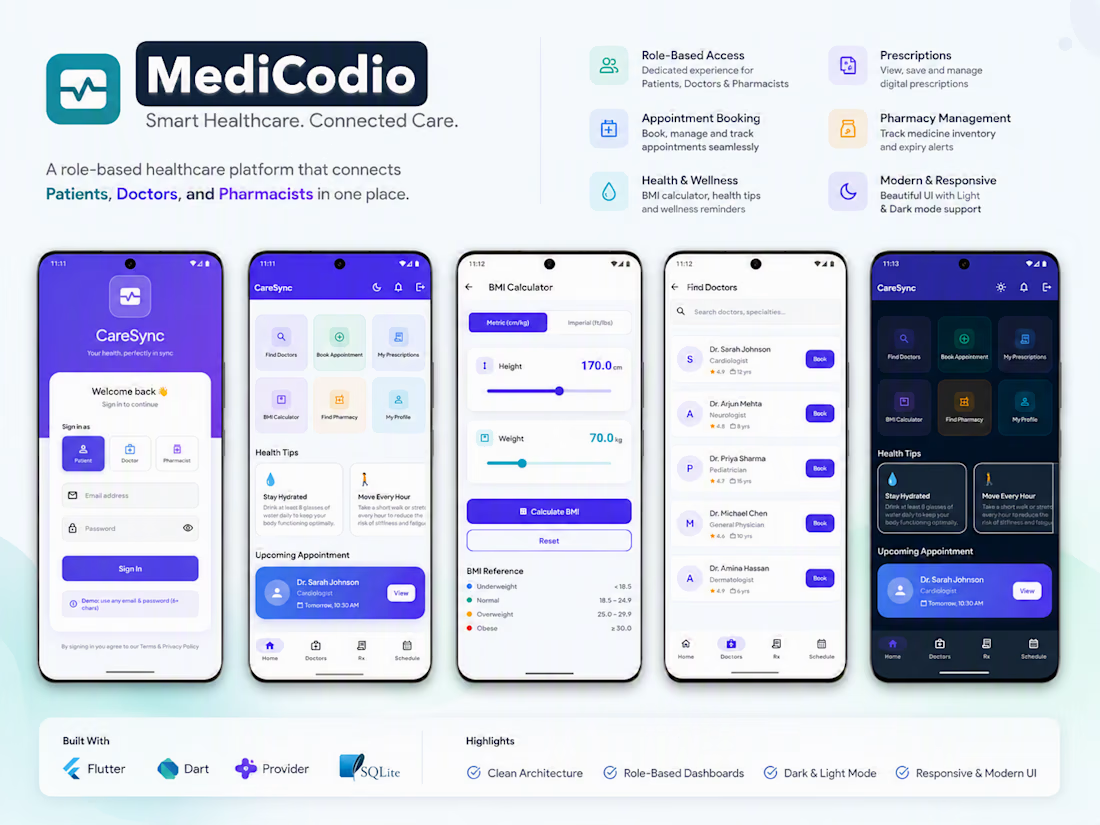

Role-based access across patients, doctors, and pharmacists in one app is the hard part here — curious how you scoped permissions between the appointment booking and prescription views, since a pharmacist and a doctor need pretty different slices of the same booking data.

Filtering at the API layer instead of the client is the right call, it means a compromised client can't just widen its own query. One thing worth adding on top: audit the write side per role too, a pharmacist's dispense update and a doctor's prescription amendment should hit...
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started










Related posts



Aryna, that golden symbol pops so nicely against the plum background ✨


Website for an app that posts to 17 apps at once. Open source now, one HTML file. Live link and code in the reply 👇

That's really great idea to save time and growing your business it will be so helpful ❤️❤️
Great job Kazi🔥🔥

Overview
Halo App is a premium Framer template I designed and built for app founders. They need a launch page that converts and feels as polished as their product.
The challenge
Most app landing pages show a static screenshot and a list of features. Visitors scroll past without feeling the product.
My approach
I made the page itself feel like an app. The hero phone tilts in 3D as you move your mouse, and the balance, chart and transactions animate in. Every feature card shows a small live preview of the feature instead of only describing it.
Design decisions
• Liquid-glass system: frosted surfaces with background blur, light edges and soft colored light that drifts behind them
• Bento layout: cards sized by importance, so the most valuable features get the most space
• Motion with a purpose: each animation explains something (sorting, saving, reminders), and all of it respects reduced-motion settings
• Built to convert: store buttons with a QR code card for desktop visitors, social proof near every call to action, and pricing with an annual-savings badge
• Two themes: a full light and dark system built on design tokens
Built with: Framer, Framer Motion, CMS and responsive breakpoints
🔗 Template: https://framer.link/ZMXd0Ev
Live Preview: https://pretty-layout-205790.framer.app/#
Launching an app? I design and build high-converting landing pages and Framer websites for startups. Message me here on Contra or email asadhussainsyedi@gmail.com.




does the 3d phone tilt just sit still on mobile or swap to something else