The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Why clock drift in production servers cascades into split-brains, expired tokens, and silent database corruption.
In modern infrastructure, time synchronization is often treated as an invisible background detail: "We have systemd-timesyncd or default NTP running; time is fine."
In virtualized and multi-cloud environments, virtual machine clocks drift constantly due to hypervisor CPU overcommit, live migrations, and hardware timer interrupt variations.
When system clocks drift by just a few hundred milliseconds, catastrophic distributed failures begin: 1. Distributed Consensus Split-Brains: Raft clusters (etcd, Consul, Patroni) rely on precise election timeouts. Clock skew can cause healthy nodes to believe the leader has timed out, triggering non-stop leader elections and cluster paralysis. 2. Kerberos & Auth Ticket Rejections: Kerberos protocols strictly enforce a 5-minute clock skew window. A drifted node suddenly rejects valid authentication tokens, locking engineers and services out of production. 3. Cryptographic Invalidation: TLS certificates evaluated against a skewed system clock appear expired or "not yet valid," breaking API handshakes without warning. 4. Transaction Sequencing Corruption: Database engines relying on timestamps for conflict resolution or multi-version concurrency control (MVCC) silently overwrite newer data with older records.
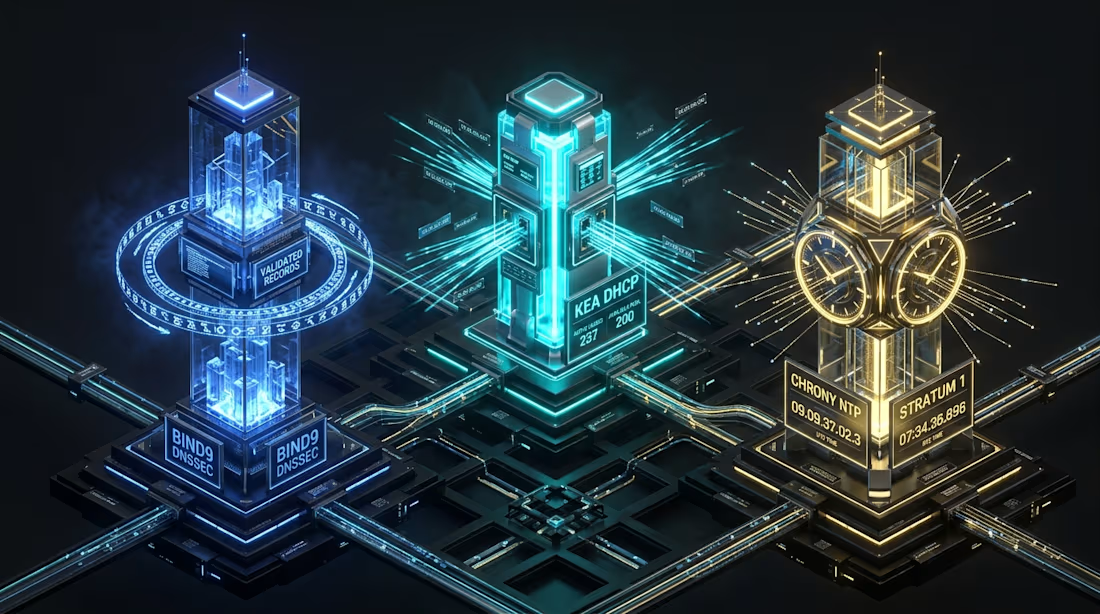
Modern infrastructure solves this with hardened **Chrony NTP**: • Sub-millisecond tracking against curated Stratum-1 hardware or atomic time sources. • Kernel-level PPS (Pulse Per Second) discipline and hardware timestamping. • Frequency drift slew calibration: smoothly adjusting clock speed rather than introducing jarring time jumps that corrupt transactional databases. • Restrictive firewalld and systemd sandboxing protecting time daemons from spoofing attacks.
Don't let silent clock drift corrupt your state.
Deploy hardened core network services with our 1-week Core Sovereign Network Services Sprint on Contra: https://contra.com/s/mrP3E36W-core-sovereign-network-services-bind9-dnssec-kea-dhcp-and-chrony-ntp
#Networking #Database #Infrastructure #Architecture #Performance #Linux #DevOps #SRE

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

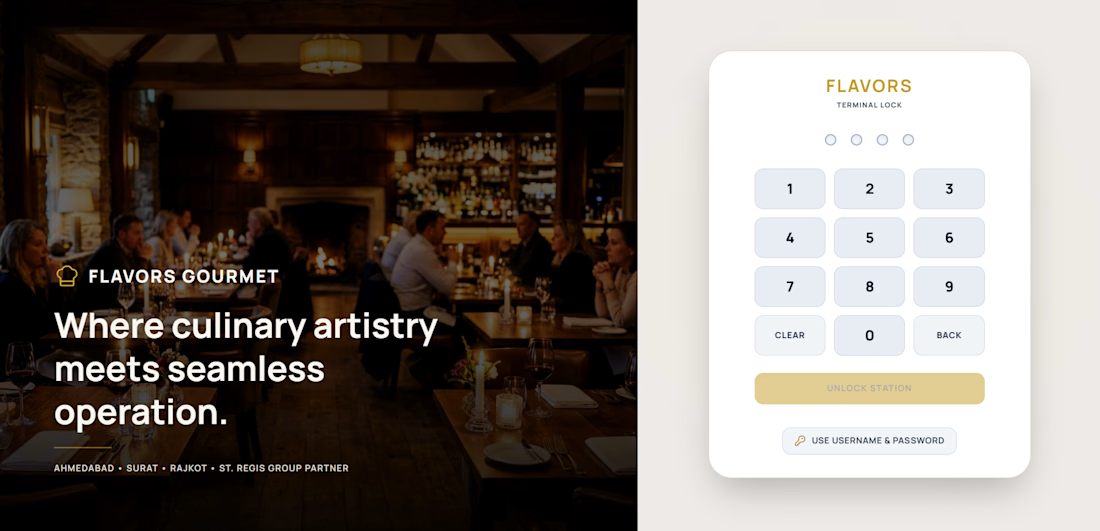
Real-time restaurant operations hub featuring bidirectional WebSocket KDS order dispatching, live table-session lifecycle management, and automated thermal receipt printing pipelines.


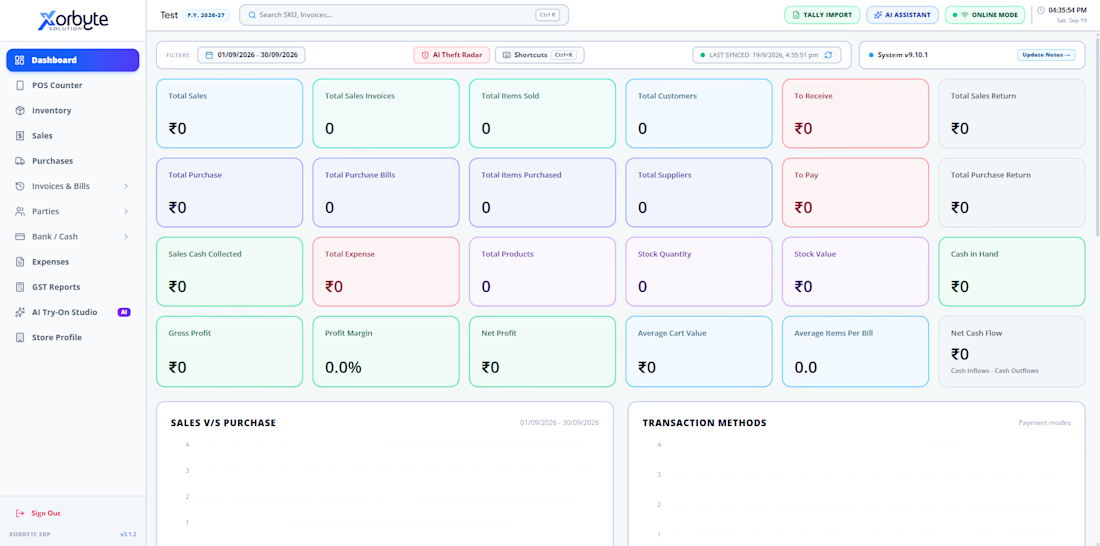
Multi-tenant retail ERP & offline-first POS platform built with React 19 and Node.js. Features 0ms real-time counter sync via Server-Sent Events, Google Gemini AI receipt OCR, and an IndexedDB offline checkout queue.

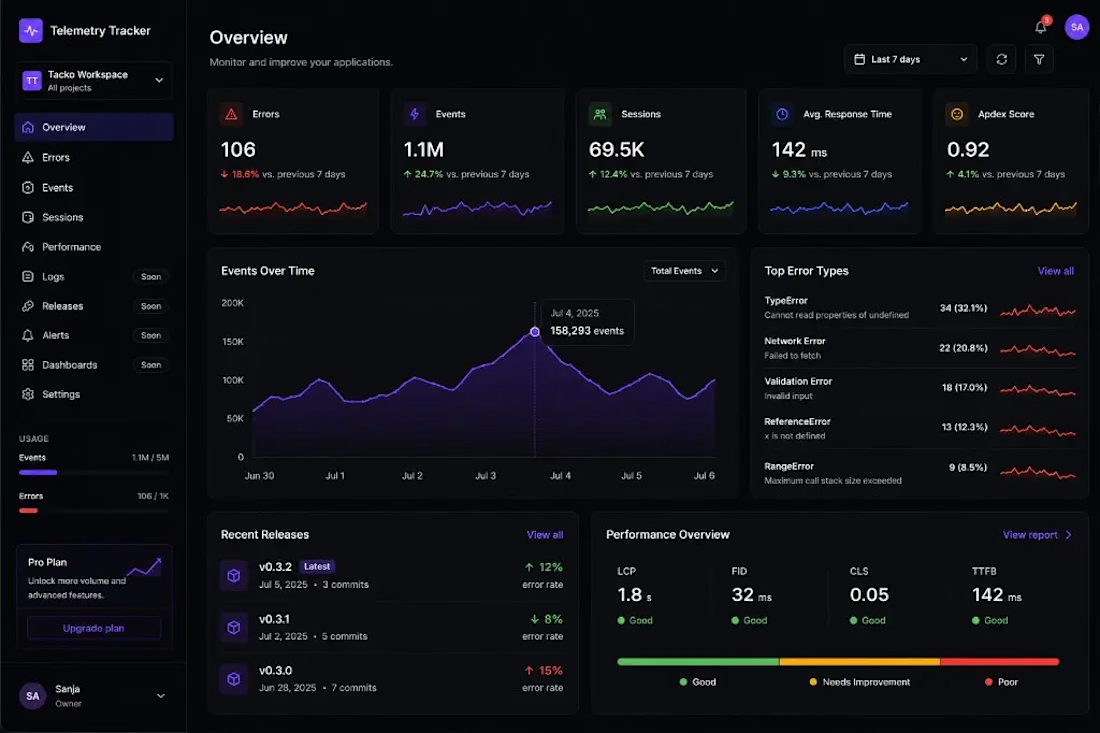
I’ve been building Telemetry Tracker — a self-hosted observability platform for error tracking, performance, sessions, releases and alerts.
Built with Next.js, TypeScript, Node.js and PostgreSQL.
One of my favorite parts of building it has been working across the entire product — from frontend and APIs to database performance, infrastructure and production reliability.