The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

A profile screen that only shows display name and bio looks like it keeps the role field safe. Firestore rules never see that screen; they evaluate the document a request proposes. Anyone signed in can send role: "admin" to their own profile document, and an ownership-only rule allows it.
The fix is a field allowlist, split in two. On update, allow the write only when diff(resource.data).affectedKeys() stays inside the editable fields. On create there is nothing to compare against, so that path validates the whole payload with keys().hasOnly().
The tempting shortcut is one allow write carrying that diff check. Role edits are blocked and existing users can still rename themselves, so an update-only test suite stays green, while every new account's first profile write fails: resource is null and the condition errors out.
Role itself belongs to server code, with rules reading a custom claim instead of a field the client can write. Full rule set, the emulator cases that catch both failures, and what field rules cannot do:
https://www.duskolicanin.com/blog/flutter-firestore-rules-field-allowlist


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started



Related posts

Behind the scenes of shipping a client web app: the launch-day cut list is where the real product gets decided. This week we shipped with three features deliberately left out, not because they were hard, but because nobody on the client's team could explain who would use them or when. Every feature you ship is a promise to maintain it, support it and explain it to the next new hire. The apps clients keep paying for are not the ones with the longest feature list, they are the ones where every single thing on screen earns its place. Ship less, on purpose, then add only what real users ask for twice.

Ship less on purpose, love that. Half the features I've built got clicked once, by me, while testing 😅


Before I touch anyone else’s code, I check these 5 things first 👇
Payments and webhooks. What happens when Stripe sends the same event twice?
Auth. Can a normal user open an admin page just by changing the URL?
Indexes. One missing index can turn a 4 ms query into a 3-second one.
Swallowed errors. An empty catch block hides bugs your users are already hitting.
Dependencies. Being 3 major versions behind means missing security fixes, and every upgrade gets harder.
Most apps don’t need a rewrite. They need the right things fixed, in the right order.
Which of these have you run into?

400 renders. Zero manual errors. 🚀
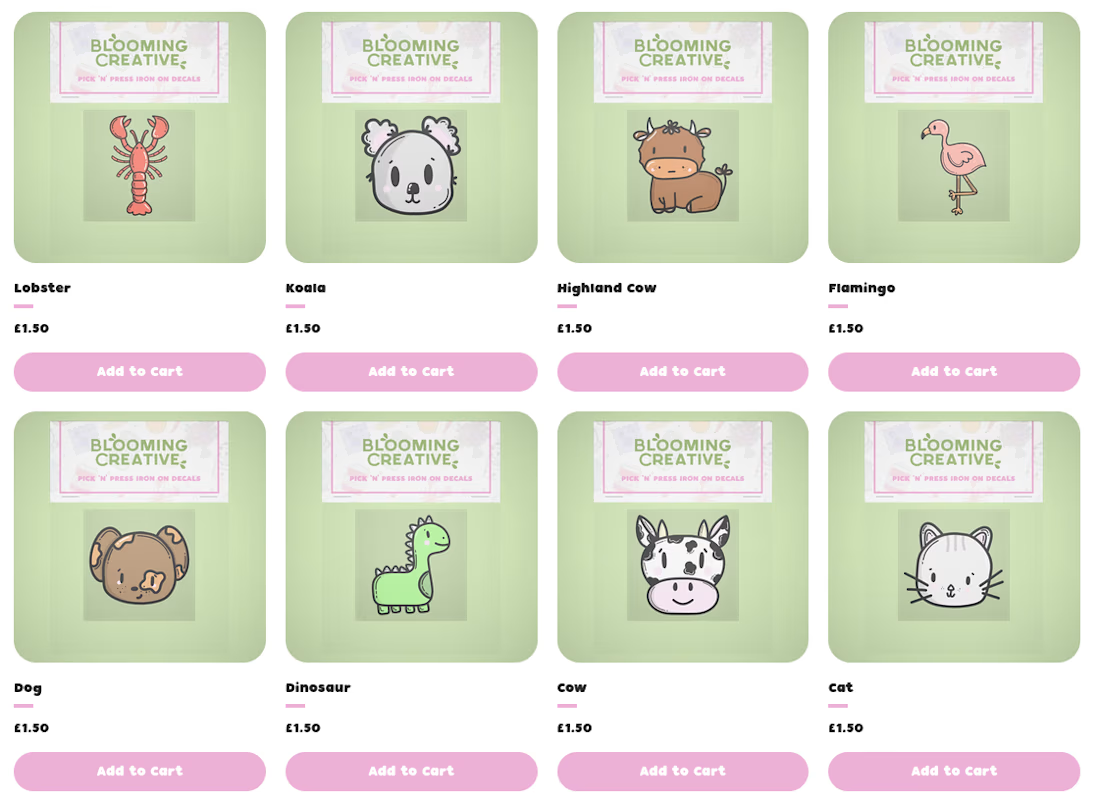
A recent client needed 400 product variants for their Wix store. The problem? Wix randomizes filenames on upload, making bulk organization a nightmare.
I solved this by building a procedural pipeline in Blender to handle the volume and using a strict SKU-based naming system for the files. To bypass the Wix glitch, I hosted the images on a temporary static site to serve them by their original names.
The result: a perfectly synced store and a process that turned days of manual data entry into a seamless technical win.


Hi Zak, let's connect. Useful approach, thanks. Where did you host them? Cloudflare or Cloudinary? Or maybe something else?