The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

A recruitment portal with Applicant signups, password resets, login, admin dashboard and applicant dashboard, form fills, prefilled area data, forms... for low cost shared hosting.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

New website for CavioAi
Architectural imagery, blue dither textures, and custom motion showing how enquiries, bookings, and CRM workflows connect.
Designed and built from the first concept to the final experience.
A quick walkthrough ↓


The blue dither on the architecture photo gives it a printed feel. Works well for an AI brand.

🚨 WordPress Security Alert: This One Deserves Attention
WordPress 7.1.2 was released as a critical security update.
But here's the part developers should pay attention to:
Security researchers have reported active exploitation attempts targeting the vulnerability after the patch was released.
The vulnerability can allow an unauthenticated attacker to include local PHP files under certain conditions, potentially leading to remote code execution.
Patchstack has reported attackers moving beyond basic scanning and attempting to write PHP files to the server.
If you manage WordPress websites, don't just assume your sites are safe because automatic updates are enabled.
✅ Check your WordPress version
✅ Verify the update actually completed
✅ Review recently modified files
✅ Check admin users
✅ Review security logs
✅ Verify your backups
✅ Remove unused plugins/themes
A security patch is only useful if it's actually applied.
For WordPress developers, regular security monitoring should be part of website maintenance — not an afterthought.
#WordPress #WordPressSecurity #WebDevelopment #PHP #CyberSecurity #WordPressDeveloper


🚨 CODES, SHADERS & SPOOKY UI: WHY BUILDERS CAN’T MATCH HAND-CODED PRECISION
Most creators blend static assets in Figma or Canva. As a Full-Stack Engineer, I treat code itself as an art form.
For the Rive Halloween Challenge, I brought together raw code, terminal-driven workflows, and GPU shaders into one ultimate dev collage:
• Rive CLI & RML: Writing responsive interactive scenes directly inside VS Code—zero bloat.
• GPU Canvas (WGSL Shaders): Custom fog, flickering lights, and real-time spooky effects powered directly by the GPU.
• Cybersecurity & Clean Architecture: High-performance, pixel-perfect web apps built to convert in 0.05 seconds.
Forget laggy plugins and heavy template builders. True digital experiences are engineered from the ground up.
💬 Quick Question for Creatives & Devs:
Are you team Drag-and-Drop Builders or team 100% Hand-Coded Architecture?
👇 Drop your thoughts below, let's connect and push the boundaries of modern web tech!


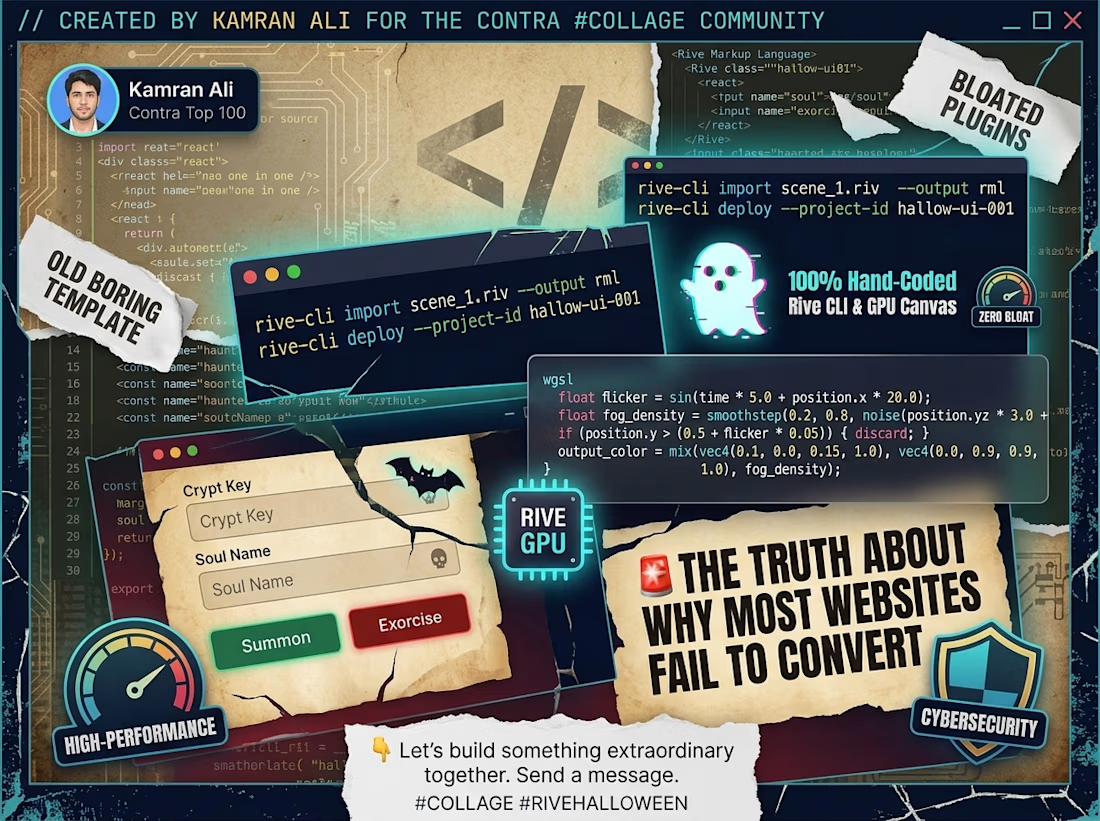

The part where you drive fog and flickering lights with WGSL shaders on the GPU feels like the kind of low level control that really cuts latency.