The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

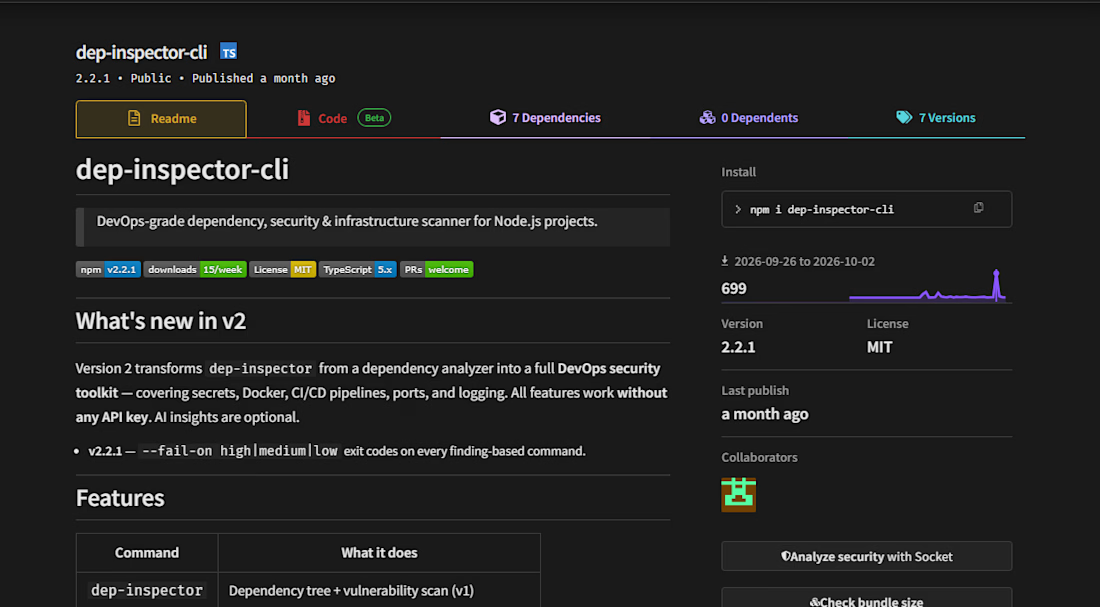
I published dep-inspector-cli — an open-source npm package that traces the exact dependency chain that pulled a vulnerable package into your project.
It explains the risk with Groq AI insights and outputs JSON for CI/CD pipelines, so builds can fail automatically on risky dependencies. 700+ weekly downloads on npm.
GitHub: https://github.com/Nevin100/Dep-inspector-cli
Built with: TypeScript, Node.js, Groq API


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started










Related posts

Building a Modern Restaurant Management Dashboard with Lovable (Light ☀️ vs. Dark 🌙)
I’ve been working on the dashboard interface for ReserveTable (Eat Pro Japan), focusing on giving restaurant managers and users a clean, modern, and intuitive interface to manage bookings, tables, and analytics.
Using Lovable, I was able to rapidly prototype and construct a modern UI system complete with smooth component transitions and native theme switching.
✨ Key Design & Tech Highlights:
⚡ Built with Lovable: Leveraged AI-powered design-to-code workflows to assemble clean component hierarchies, responsive search/filter bars, and sleek cards rapidly.
🌗 Seamless Light & Dark Mode: Designed a flexible color system using modern CSS variables / Tailwind tokens so the entire interface gracefully shifts between an elegant light aesthetic and a moody, dark dining ambience.
🎯 Contextual UI Elements: Styled input controls, select menus, and primary CTA buttons to maintain legibility and contrast across both light and dark themes.


For reservation and table states, the same semantic color tokens need to stay clear in light and dark mode. Did you define status tokens once and map both themes to them, or tune those colors per component?


I like the design

This is for all of us building with Ai…
Stop asking AI to "make it look pretty" and expecting a miracle. You’re just going to get the same boring layout as 500 other companies.
Watch this before you build another piece of AI slop
Don’t say i didn’t do anything for you 🌝🤲🏽… And yesss, I was shouting because the Ai design slop is too much😂
