The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost


Cyber Insurance in 2026
Have you wondered what Cyber Insurance carriers are actually requiring in 2026? Most of my clients fail at least 2 of these when I audit their environment.
Here's the checklist insurers are using:
→ MFA enforced on ALL accounts — not just "enabled." Carriers want enforcement logs.
→ Conditional Access policies active — blocking legacy auth, requiring MFA from new devices.
→ Endpoint Detection & Response — antivirus alone doesn't qualify anymore.
→ Tested backups with restore verification — documented in the last 90 days.
→ Written incident response plan — reviewed annually.
The enforcement is real. I've seen claims denied because the org had MFA "available" but not enforced. That's a denial.
Here's what gets me: most orgs running Microsoft 365 Business Premium already have the tools to check every box. Conditional Access, Intune, Defender — it's all included in the license. They just haven't configured it.
A security configuration engagement takes about a week for a 25-50 person company. That's the difference between a covered claim and a denied one.
If your organization needs help getting compliant before your next renewal, I do this work every week. DM me or check my services below.
#CyberInsurance #Microsoft365 #MFA #Cybersecurity #SMBSecurity

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started







Related posts

Shielda is a mobile cybersecurity app that helps small businesses detect and respond to digital threats in real time.
The experience makes security easier to manage for non-technical users. Clear threat statuses, high-contrast visuals, and actionable alerts help business owners understand what needs attention and decide what to do next.
See the design: https://dribbble.com/shots/27792730-Mobile-App-Cybersecurity


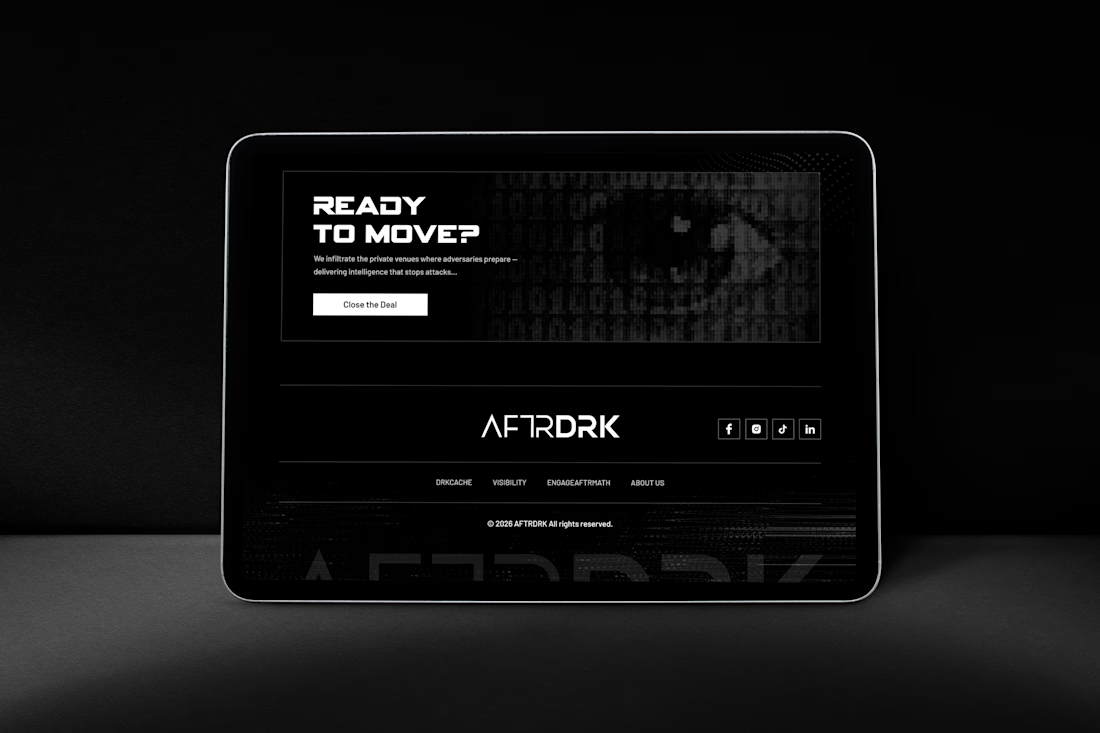
Almost every cybersecurity website looks the same. Blue gradients, padlock icons, and a stock photo of a hacker in a hoodie.
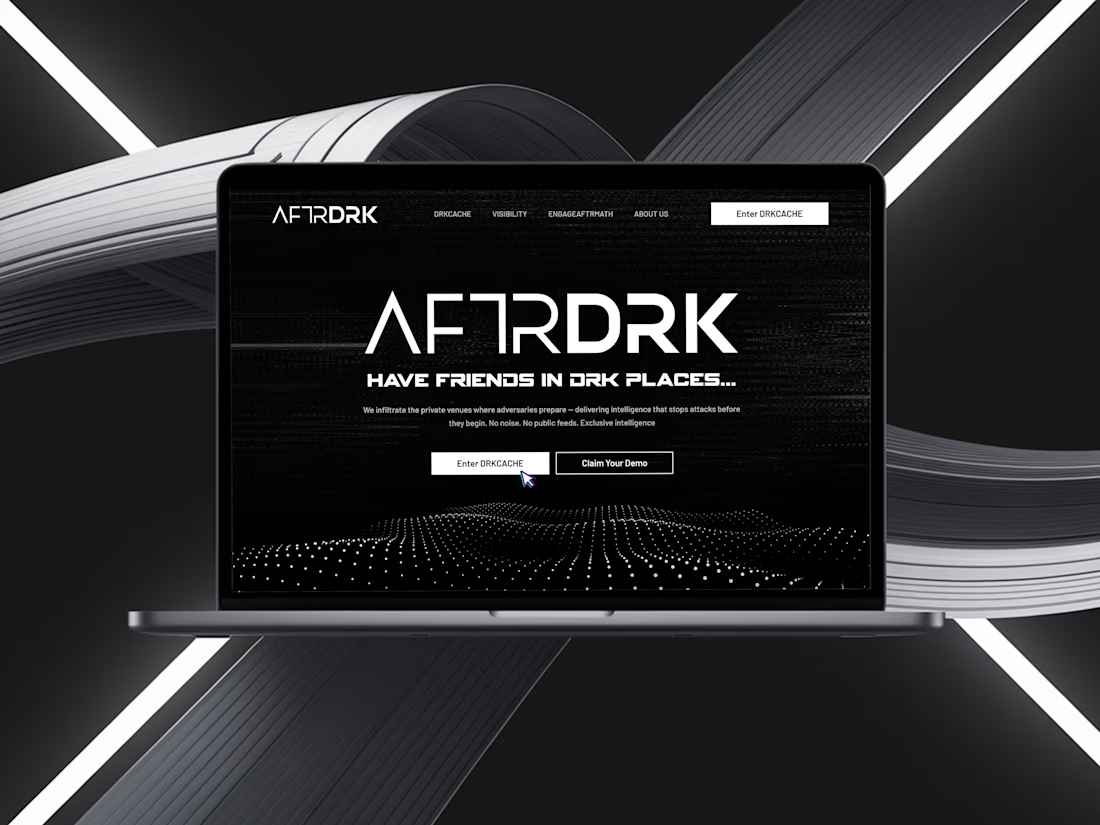
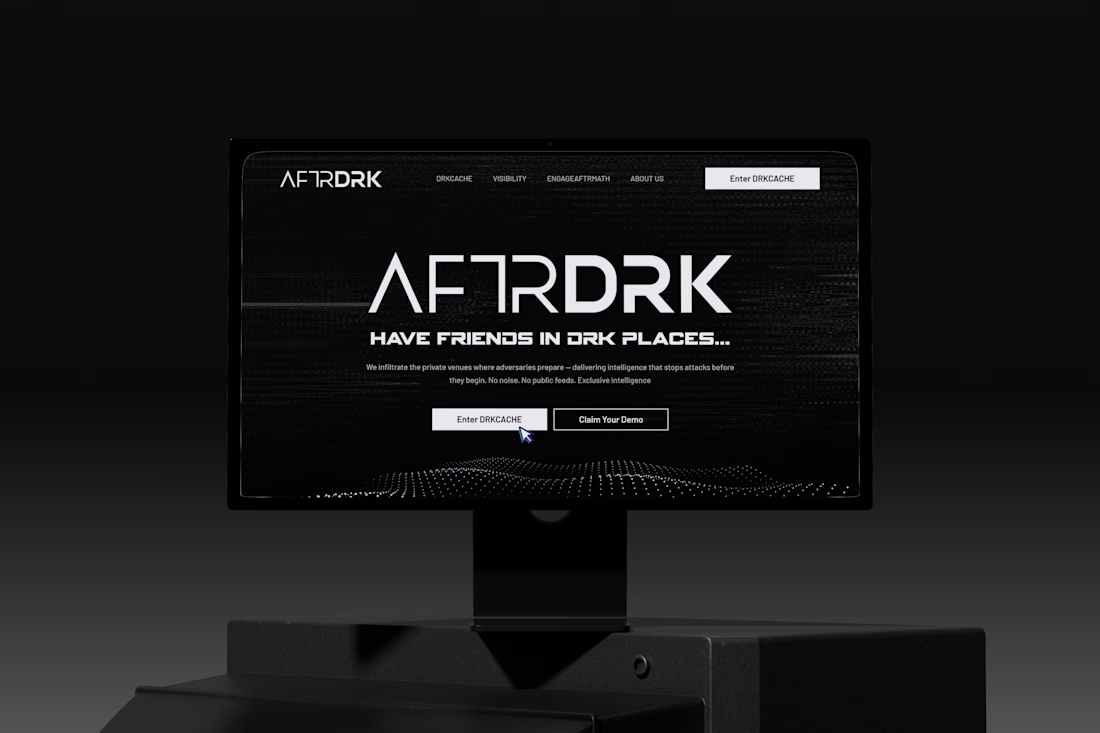
For my AFTRDRK concept, a threat intelligence company that operates in the hidden corners of the internet, I went the other way.
Their whole value is access to places others can’t reach. So instead of looking “safe,” the site leans into the dark:
1) Pure black and white, no accent colour. The restraint makes it feel serious and exclusive
2) Glitch textures, scan lines and a particle wave, so the page feels like it’s picking up signals from somewhere hidden
3) A headline with attitude: “Have friends in DRK places...” It tells you exactly what they do in five words
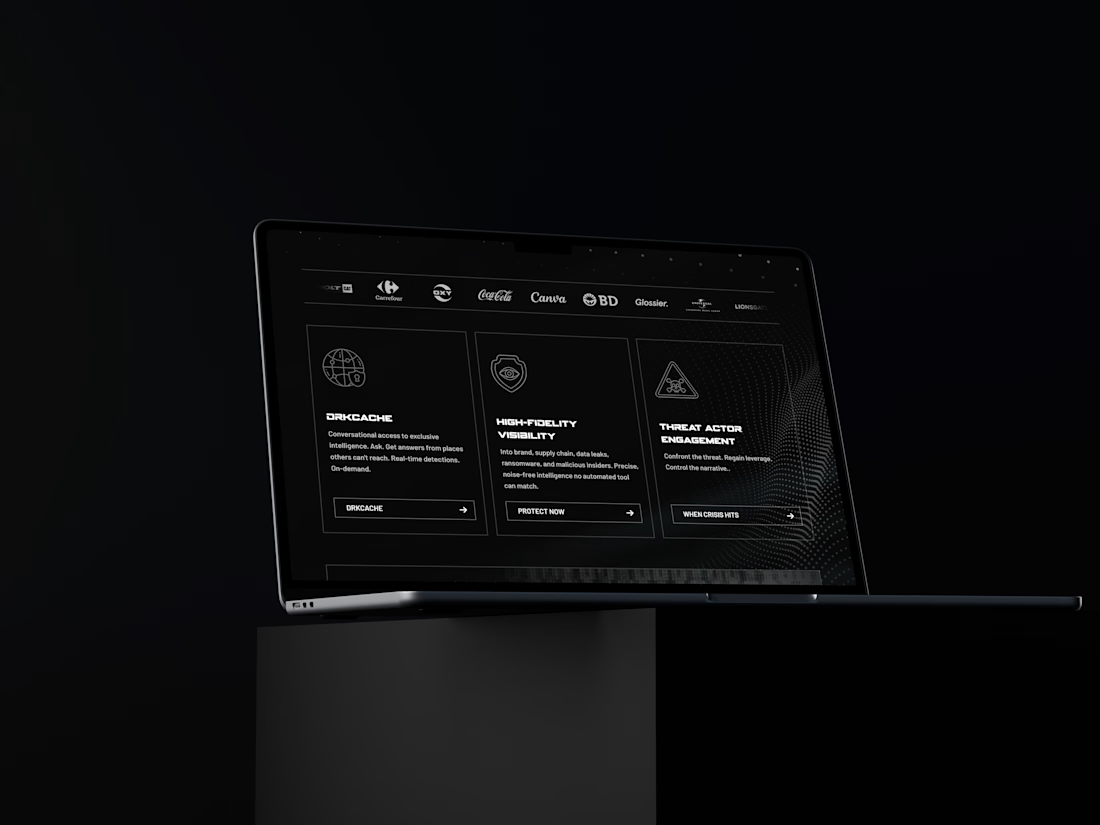
4) Three services, each with its own action: DRKCACHE, Protect Now, When Crisis Hits. The button tells you which situation you’re in
Dark, but never messy. Every section stays clean enough for a security team to trust.
Designers, honest question:
Should a cybersecurity brand look safe and reassuring, or a little dangerous?


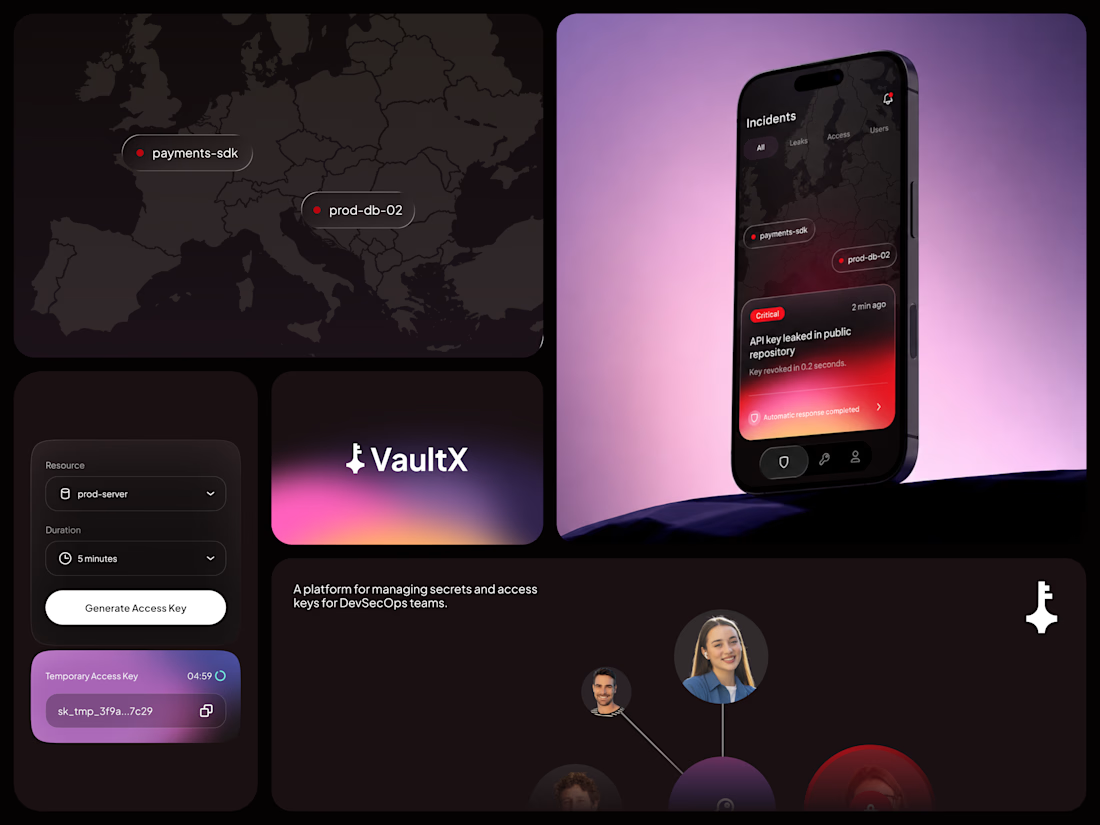
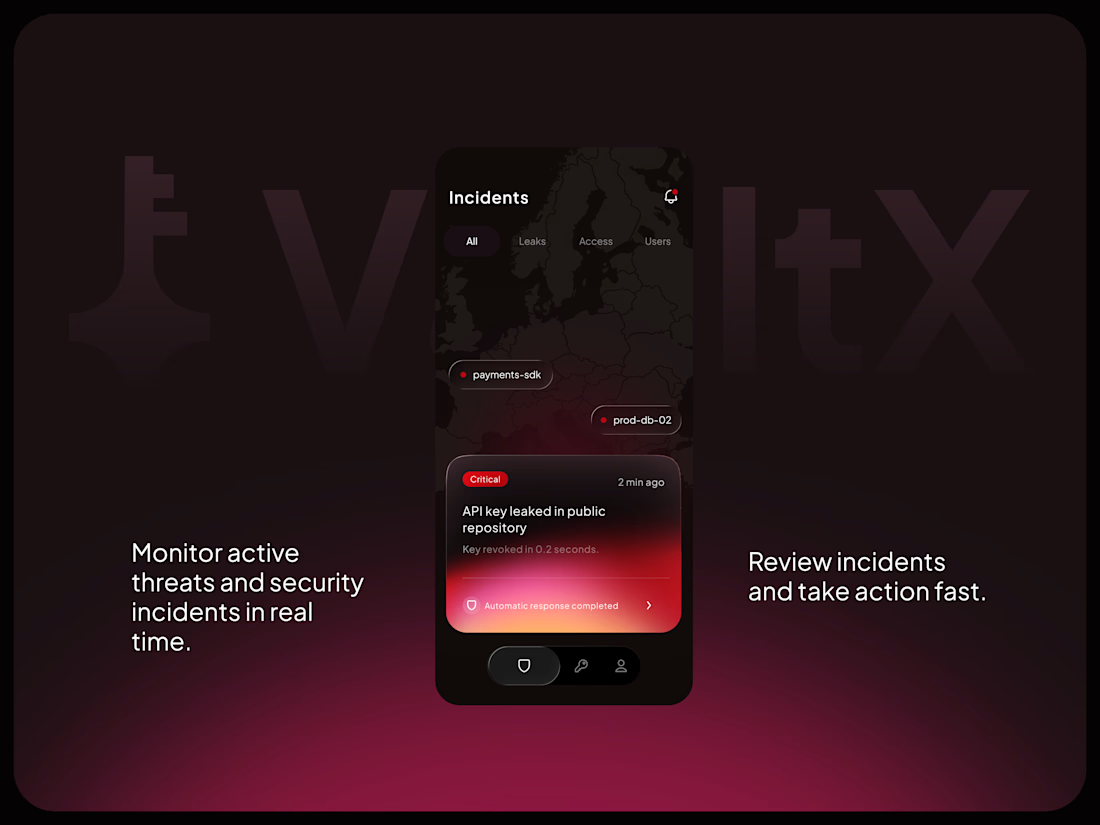
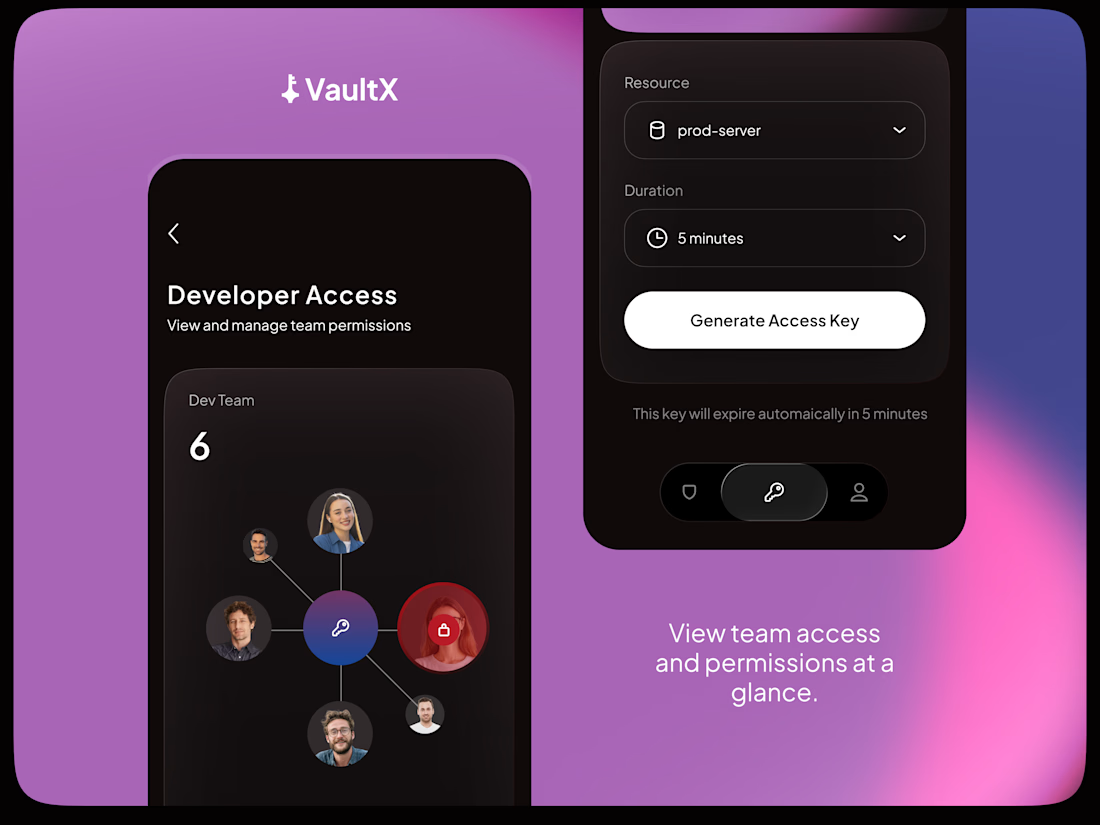
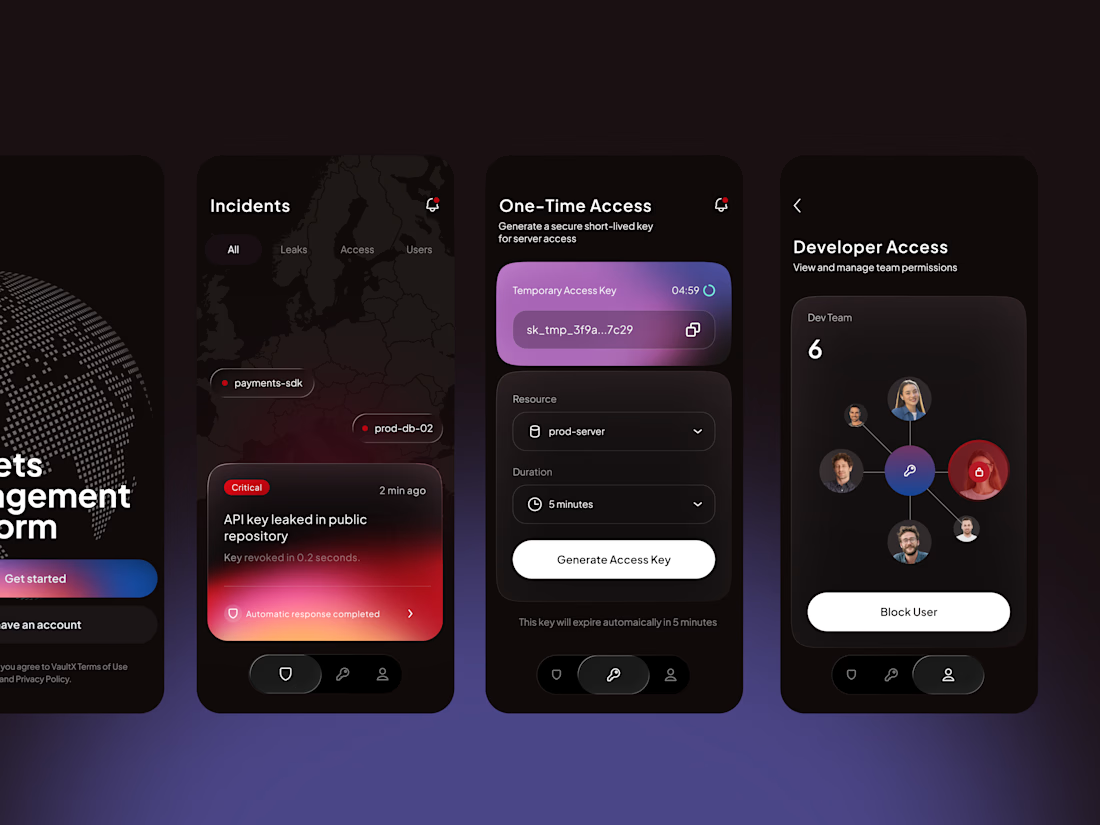
VaultX is a mobile security app for DevSecOps teams. We designed a focused experience for monitoring security incidents, generating temporary access keys, and managing sensitive resources and team permissions.
See the project on Dribbble:
https://dribbble.com/shots/27782415-Mobile-App-DevSecOps-Security