The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

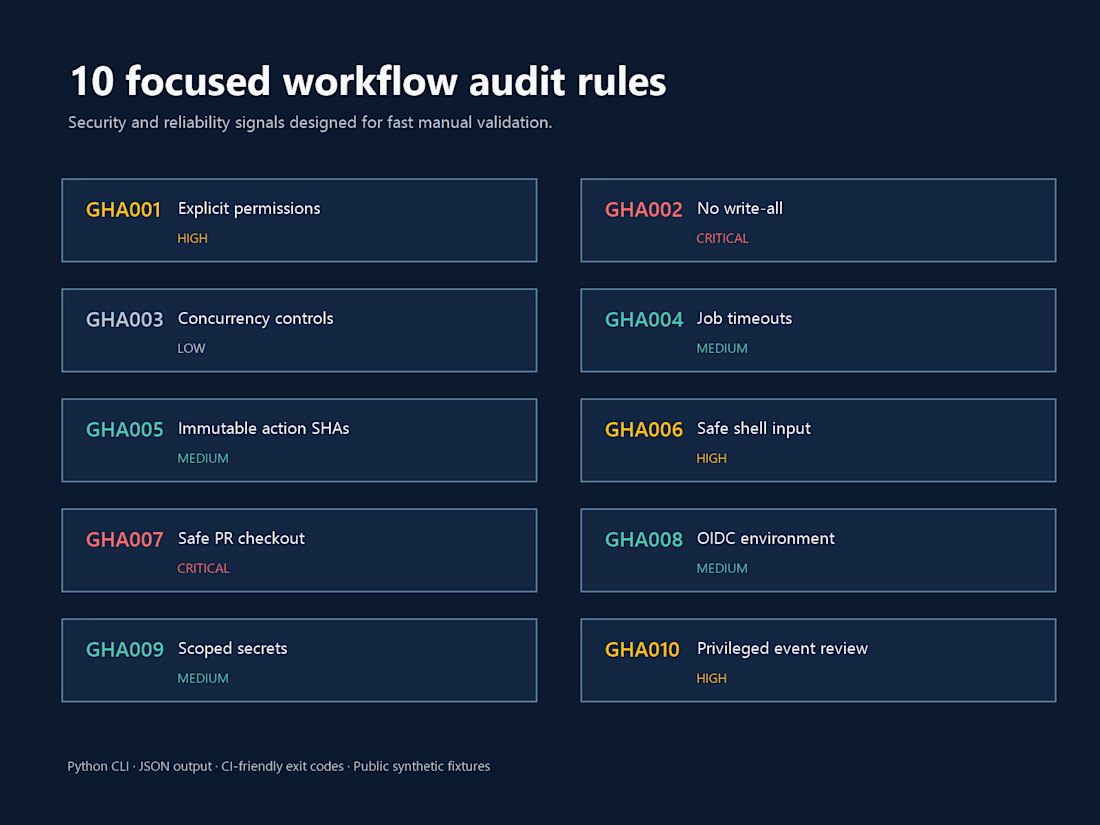
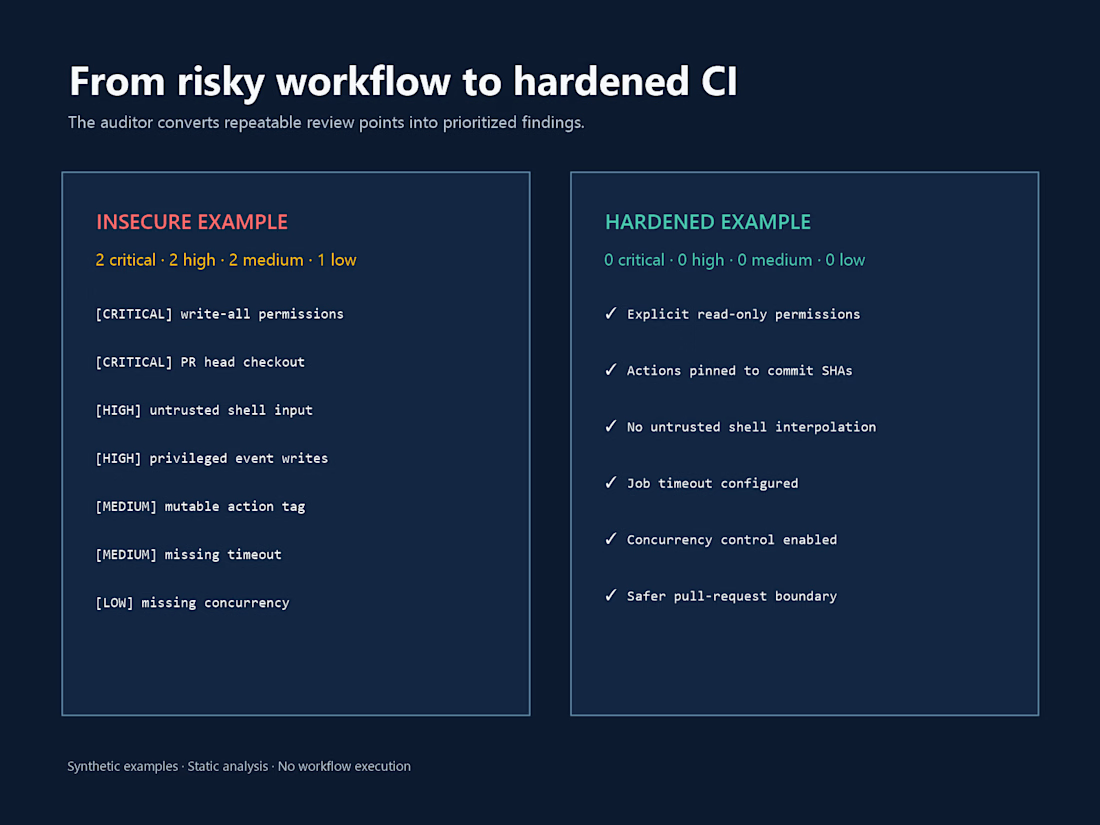
I built a Python CLI that statically reviews GitHub Actions workflows for security and reliability risks. It detects excessive permissions, mutable action references, unsafe shell interpolation, privileged pull-request patterns, missing timeouts and concurrency controls, OIDC boundary concerns, and broad secret inheritance.
The project includes 10 focused audit rules, human-readable and JSON output, CI-friendly exit codes, synthetic before-and-after workflows, 11 unit tests, and its own hardened GitHub Actions pipeline. The auditor does not execute workflow code, and all examples are public and synthetic.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

Building AI for healthcare leaves zero room for error.
I’m currently collaborating with an incredible team on Raphald AI, a medical detection application. Building the systems for a project with stakes this high is a massive reminder that the underlying backend architecture matters just as much as the machine learning model itself.
When integrating diagnostic AI, your API endpoints cannot drop requests, and your database workflows demand absolute integrity. You aren't just passing JSON payloads; you are handling critical, real-time workflows where stability is non-negotiable.
Engineering these systems continues to shape my approach to building robust Python backends. If you are developing a product that requires reliable AI integration or rock-solid FastAPI infrastructure, check out the newly updated services on my profile. Let's build something that works when it counts.


𝐑𝐀𝐆 𝐀𝐈 𝐊𝐧𝐨𝐰𝐥𝐞𝐝𝐠𝐞 𝐏𝐥𝐚𝐭𝐟𝐨𝐫𝐦 | 𝐈𝐧𝐭𝐞𝐥𝐥𝐢𝐠𝐞𝐧𝐭 𝐒𝐞𝐚𝐫𝐜𝐡, 𝐀𝐈 𝐀𝐧𝐬𝐰𝐞𝐫𝐬 & 𝐕𝐞𝐜𝐭𝐨𝐫 𝐃𝐚𝐭𝐚𝐛𝐚𝐬𝐞
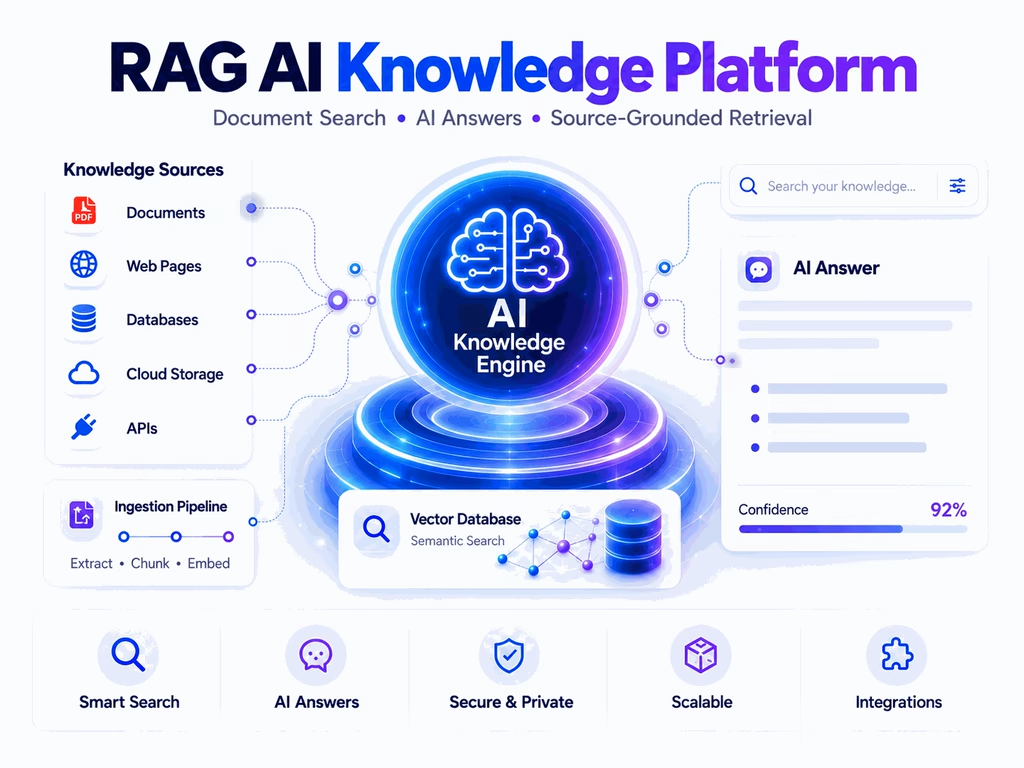
I designed and built a RAG-powered AI knowledge platform that lets businesses search documents, websites, databases, and internal knowledge using natural language.
The system processes content, creates embeddings, stores them in a vector database, retrieves the most relevant information, and uses AI to generate accurate, source-grounded answers.
My services include: RAG development, document ingestion, semantic search, vector database setup, OpenAI/LLM integration, internal knowledge assistants, API integrations, and analytics.
The solution helps teams find information faster, reduce repetitive research, improve answer consistency, and build scalable AI-powered knowledge systems.
𝐓𝐞𝐜𝐡 𝐒𝐭𝐚𝐜𝐤:
OpenAI, LangChain, RAG, Pinecone, Qdrant, Weaviate, FAISS, Chroma, Python, FastAPI, PostgreSQL, APIs.


Hi everyone! if you want to develop your own websites. You are in right place. Feel free to contect me.I am always available for you. Thank you