The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Recently something interesting happened.
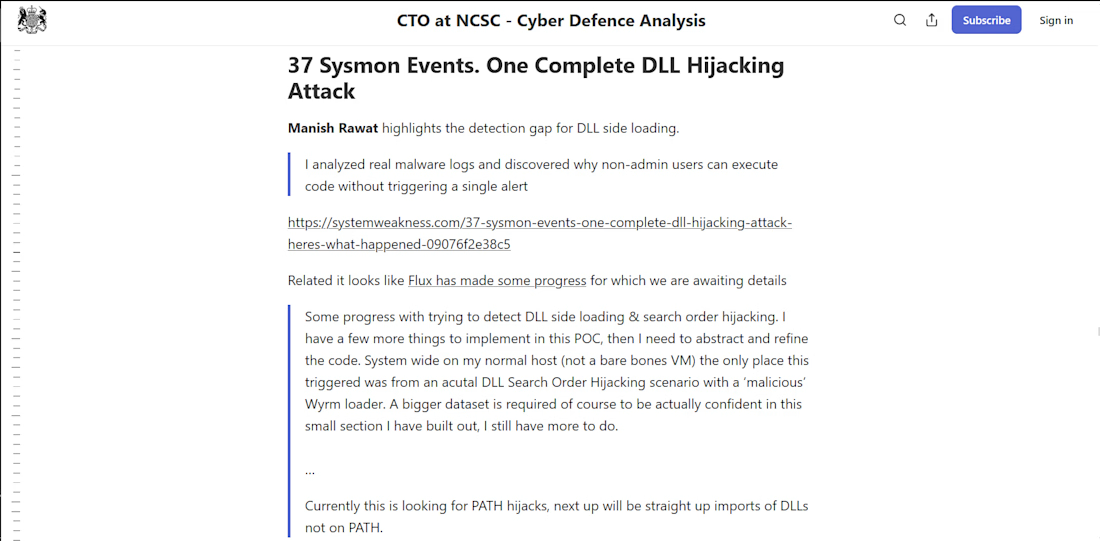
My research on DLL hijacking detection was referenced in work from the National Cyber Security Centre (Cyber Defence Analysis).
The section “37 Sysmon Events. One Complete DLL Hijacking Attack” came from my analysis of malware telemetry showing how code execution occurred without triggering alerts.
To clarify: the detection PoC mentioned later isn’t mine — my contribution focused on identifying the detection gap.
Right now I’m continuing to explore:
• Sysmon event correlation
• Detection blind spots in Windows telemetry
• Why some attacks still bypass common logging assumptions
If you're working on detection engineering, threat hunting, or malware analysis, I’d be happy to exchange ideas.
#threathunting #Malwareanalysis #Medium #Infosec #detectionengineering


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Related posts


Casemate: making malware analysis feel calm instead of scary
Cybersecurity websites usually look the same: black background, green code, a hooded guy. I wanted to try the opposite for Casemate, a concept for a malware analysis tool.
The idea is simple: the product keeps a suspicious file in a sealed chamber and watches what it does. So I put a bug frozen in amber in the middle of a canyon. It’s dangerous and under control at the same time, and you get it without reading a word.
Then I made sure the page still works for a security lead who wants facts. The stats sit right next to the headline: threats isolated, latency, endpoints covered.
The hardest part was keeping it warm without losing trust. I stayed with one terracotta colour, wide capitals and mono labels, so it reads like a serious tool and not a poster.
I’m taking on new projects for SaaS and tech teams. If you have a product that’s hard to explain in one glance, send me a message.
What do you think, would you trust a security product with a canyon on the homepage?


I love it! It feels so calm, and I would definitely try it! This is amazing, Kris. I never thought cybersecurity could be this cool ❤️🔥

DriftWatch
DriftWatch is an API concept for identifying customers who may be becoming inactive.
Rather than introducing machine learning immediately, I designed the first version around an explainable rules-based scoring system.
The score considers signals such as:
Recent activity
Changes in engagement
Event severity
The approach is intentional.
Without sufficient real-world data, an ML model would add complexity without necessarily adding value.
The initial goal is to establish measurable signals, collect real usage data and use that information to determine whether machine learning is justified later.