The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

🔍 Splunk Investigation: Tracing a Ransomware Attack Chain
During my SOC internship, I analyzed a simulated ransomware attack using Splunk to reconstruct the attack timeline and identify key indicators of compromise.
This investigation involved:
• Log analysis and event correlation
• IOC identification
• Tracking attacker activity
• MITRE ATT&CK mapping
• Incident documentation
One of the most valuable lessons was learning how individual security events can be connected to reveal the bigger picture of an attack.
I've shared the full project in my portfolio for anyone interested in the investigation process and findings.
#CyberSecurity #SOCAnalyst #Splunk #BlueTeam #ThreatDetection
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Splunk Log Analysis and Investigation: Ransomware Chain
Splunk

Security Engineering
Systems Engineering


Related posts



Really nice use of color and texture in this! Great job!



The green accents work so well.

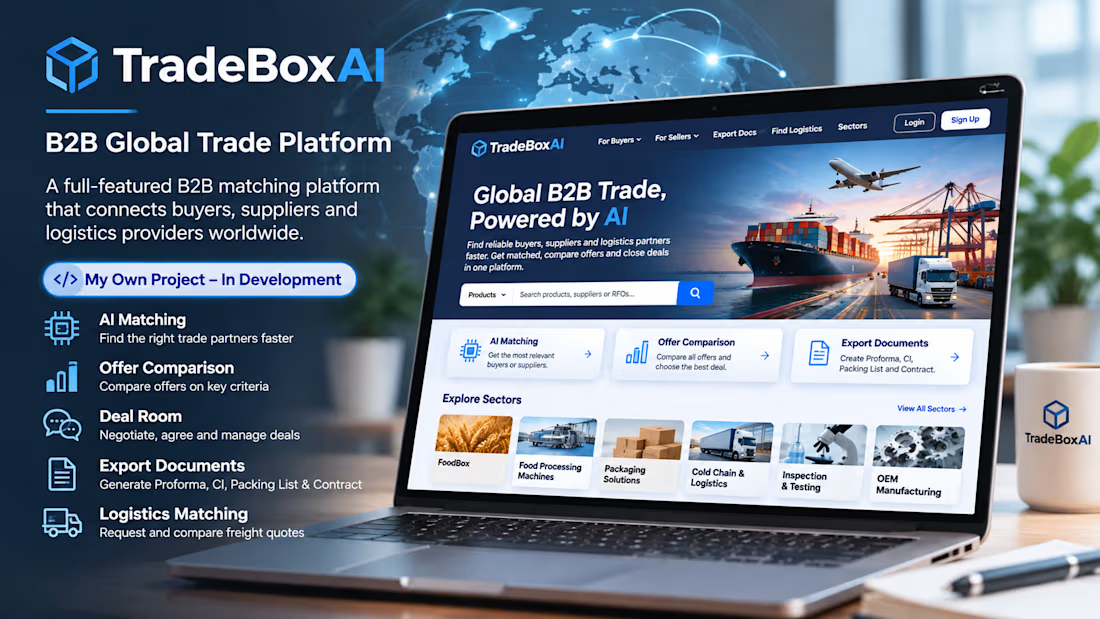
Project Title: TradeBoxAI – AI-Powered B2B Global Trade Platform
Project Description:
TradeBoxAI is my personal software development project, currently in active development.
I'm building an AI-powered B2B trade platform designed to connect international buyers, suppliers, and logistics providers.
The platform includes AI-powered matching, offer comparison, buyer–seller communication, export document generation, and logistics management.
I'm personally involved in the platform's concept, interface design, development, and business workflows, drawing on my 15 years of international trade experience.
Project Status: In Development
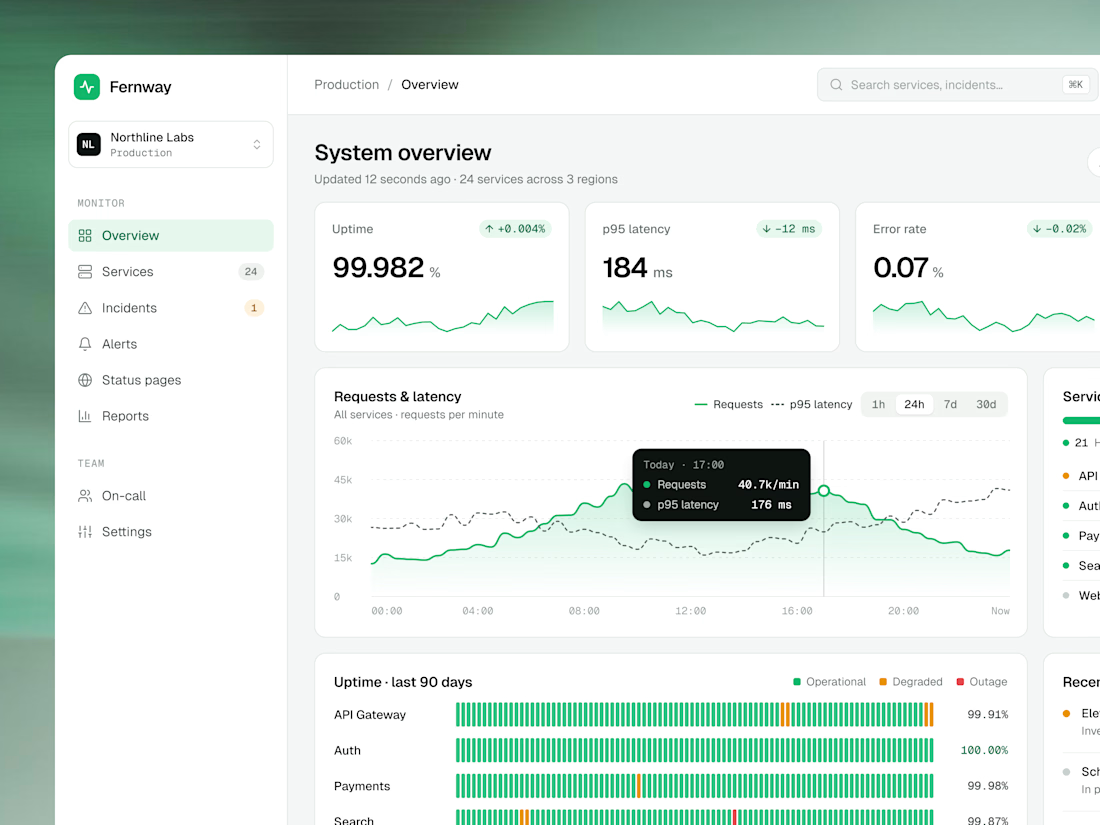
The cover image is a conceptual visualization of the platform, not an actual screenshot of the finished product.