The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Most AI products fail the same three security tests.
The system prompt can be extracted in under 10 minutes.
The guardrails block obvious jailbreaks but miss indirect prompt injection through documents, RAG sources and tool outputs.
There are no runtime evidence logs, so when a regulator or enterprise client asks "prove your model behaved", there is nothing to show.
I work on exactly this. That's my product AI Prompt Shield in the screenshot below, a guardrail API with runtime evidence logging mapped to OWASP's agentic security guidance and the EU AI Act. I have also published a book on LLM security and write about AI governance and compliance.
What I offer here on Contra, all fixed scope, no hourly meters:
LLM security and prompt injection audits
System prompt hardening and prompt engineering
AI governance documentation packs aligned to the EU AI Act
Technical writing on AI security and compliance
If you are shipping anything with an LLM inside it, get it tested before a user or a competitor does it for free. DM me.
#aisecurity #llm #promptengineering #aigovernance #euaiact #compliance #promptinjection #technicalwriting

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

I built ProofFace a visual provenance & content verification engine in Rust
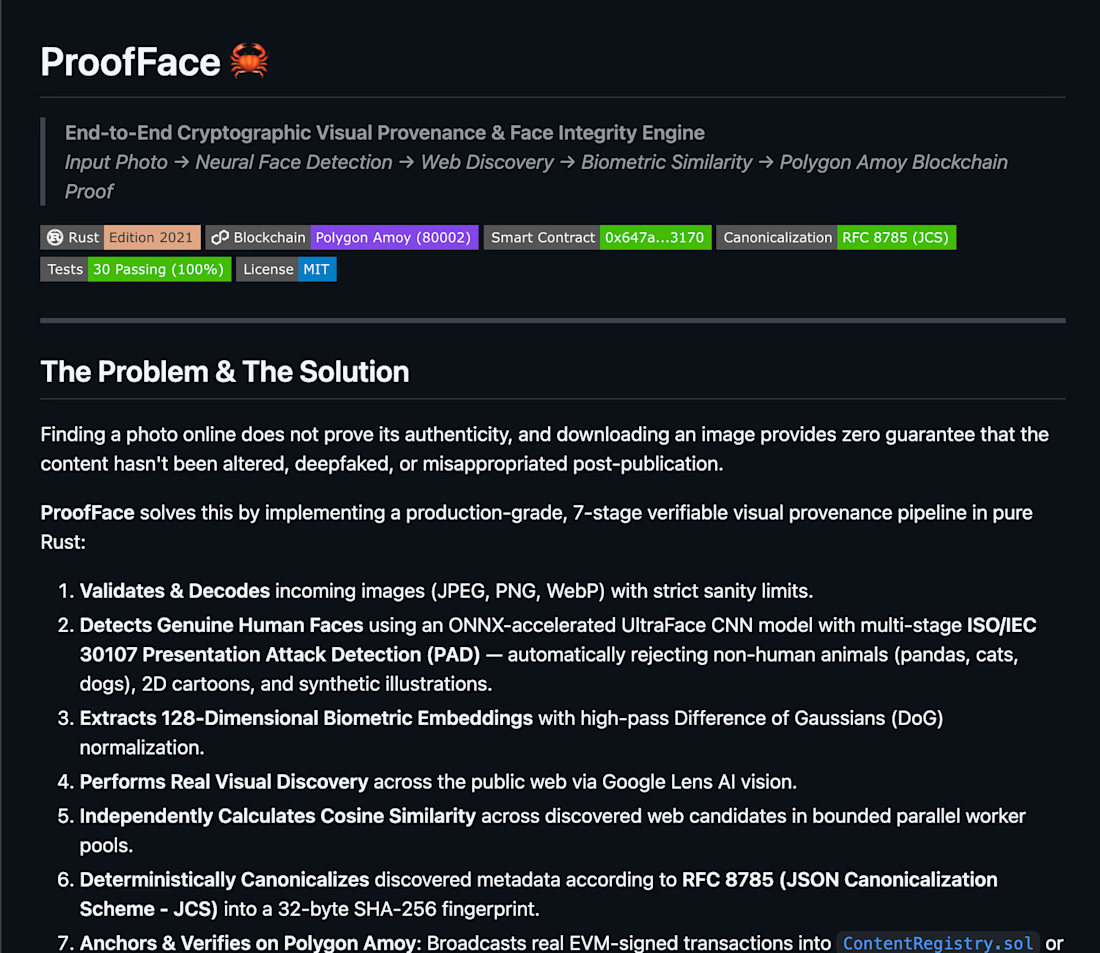
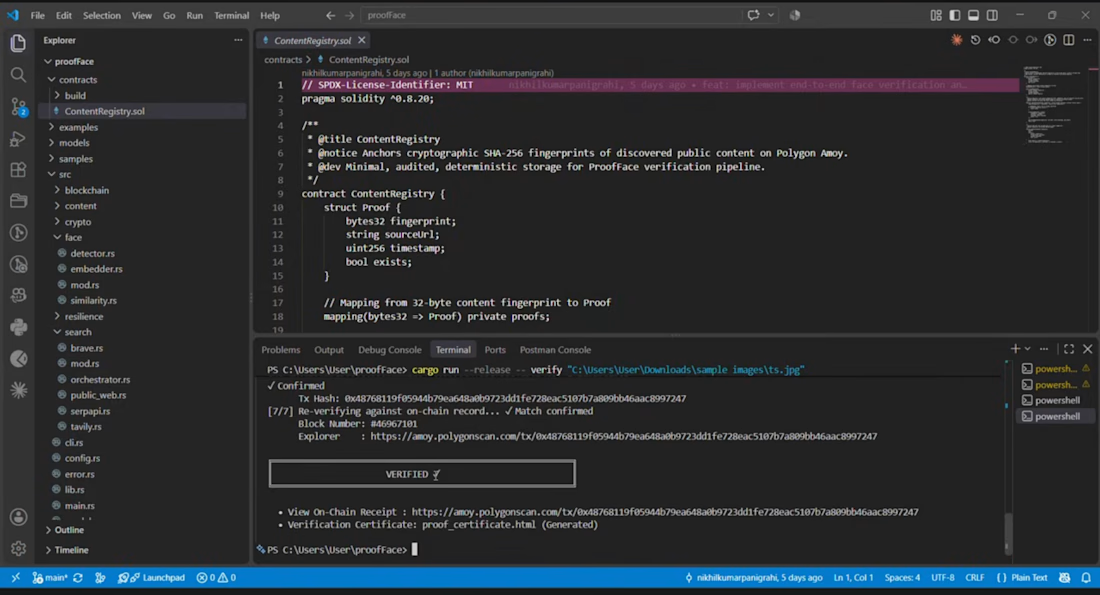
I have been building ProofFace an end-to-end visual provenance and content verification engine built in Rust.
The idea is simple:
Finding an image online doesn’t prove that it’s authentic, original, or unchanged.
So I built a verification pipeline that goes from:
📸 Image input
→ 🧠 Neural face detection
→ 🔎 Web visual discovery
→ 🧬 Biometric similarity
→ 🔐 Deterministic SHA-256 fingerprinting
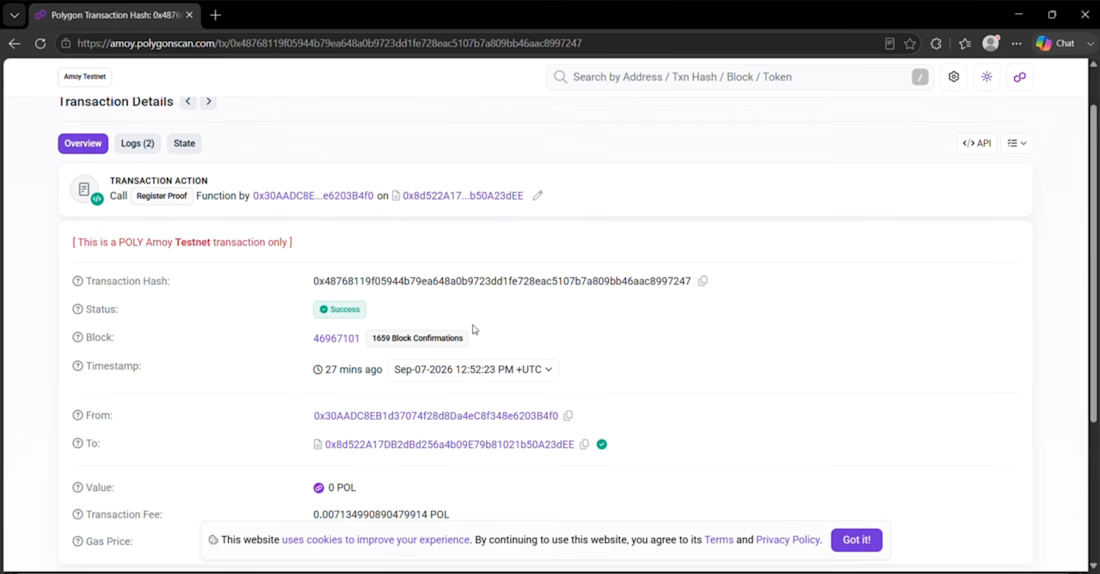
→ ⛓️ Polygon Amoy blockchain proof
→ ✅ Verification result
Some of the things I worked on:
• ONNX-based face detection
• 128-dimensional biometric embeddings
• Presentation attack detection
• Parallel visual candidate evaluation
• Cosine similarity matching
• RFC 8785 JSON canonicalization
• SHA-256 content fingerprinting
• Polygon smart-contract integration
• Automated unit & integration testing
The project currently has 30 passing tests.
What I enjoyed most was bringing several different areas together computer vision, Rust systems programming, cryptography, and blockchain into one reproducible verification workflow.
Would love to hear what you’d improve or add to a system like this.


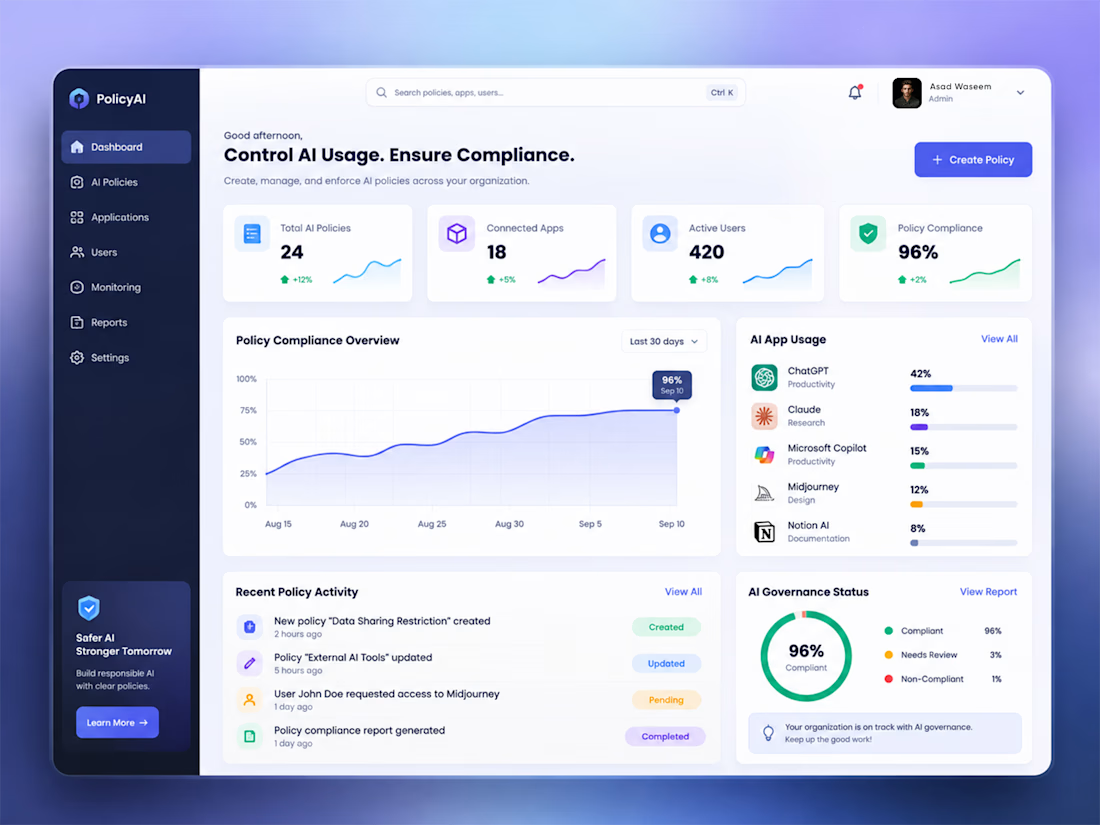
AI Governance Dashboard | Control AI Usage. Ensure Compliance.
AI is becoming part of every organization, but managing how teams use AI tools is becoming a serious challenge.
I designed this AI Governance Dashboard to bring policy management, compliance monitoring, AI application usage, user activity, and governance analytics into one centralized platform.
The goal was to keep a complex enterprise product simple, clear, and actionable through:
• AI Policy Management
• Compliance Monitoring
• AI App Usage Analytics
• User & Access Management
• Governance Status
• Policy Activity
• Compliance Reporting
The interface uses a clean SaaS design system with clear hierarchy, data visualization, subtle gradients, and focused interactions.
Designed in Figma.
If you're building an AI SaaS, enterprise dashboard, or web application, feel free to connect or message me.


I created this short AI film using detailed prompting 😍