Advanced Enterprise Red Teaming & Adversary EmulationSohaib Jamil
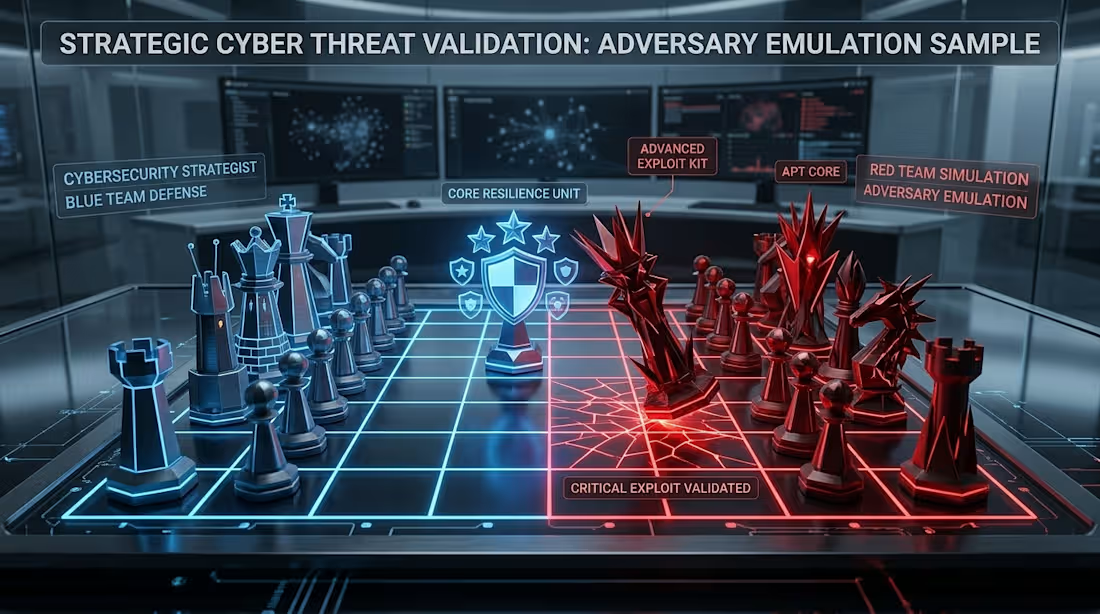
Validate your organization's true security posture through a full-scale, objective-driven adversary emulation. Unlike standard vulnerability scanning, this service simulates real-world Advanced Persistent Threats (APTs) to test your network's perimeter resilience, your internal detection capabilities, and your incident response effectiveness. By chaining together complex attack vectors—from initial phishing footholds to complete Active Directory compromise—this assessment demonstrates exactly how sophisticated threat actors can access your critical infrastructure and data.
What You Get
Executive Debrief Dashboard: A high-level, impact-focused summary detailing the attack timeline, time-to-compromise metrics, and SOC detection rates.
Verified Attack Kill Chain: A comprehensive breakdown mapped to the MITRE ATT&CK framework, documenting every executed technique from initial access to domain dominance.
Operator Evidence & Log Correlation: Raw terminal logs, cryptographic proofs, and verified attack paths to help your Security Operations Center (SOC) tune their SIEM alerts and close visibility gaps.
Strategic Remediation Roadmap: Actionable, prioritized engineering steps to patch misconfigurations, harden Active Directory security groups, and eliminate critical internal attack paths.
Core Testing Methodologies
Spearphishing & Initial Foothold Generation
Adversary-in-the-Middle (AiTM) MFA Bypasses
Active Directory Enumeration & BloodHound Mapping
Identity & Privilege Escalation (Kerberoasting, Misconfigured ACLs)
Network Pivot, Data Exfiltration & Domain Dominance
Starting at$250
Duration1 week
Tags
Penetration Testing
Red Teaming
Service provided by
Sohaib Jamil Abbottabad, Pakistan
Advanced Enterprise Red Teaming & Adversary EmulationSohaib Jamil
Starting at$250
Duration1 week
Tags
Penetration Testing
Red Teaming
Validate your organization's true security posture through a full-scale, objective-driven adversary emulation. Unlike standard vulnerability scanning, this service simulates real-world Advanced Persistent Threats (APTs) to test your network's perimeter resilience, your internal detection capabilities, and your incident response effectiveness. By chaining together complex attack vectors—from initial phishing footholds to complete Active Directory compromise—this assessment demonstrates exactly how sophisticated threat actors can access your critical infrastructure and data.
What You Get
Executive Debrief Dashboard: A high-level, impact-focused summary detailing the attack timeline, time-to-compromise metrics, and SOC detection rates.
Verified Attack Kill Chain: A comprehensive breakdown mapped to the MITRE ATT&CK framework, documenting every executed technique from initial access to domain dominance.
Operator Evidence & Log Correlation: Raw terminal logs, cryptographic proofs, and verified attack paths to help your Security Operations Center (SOC) tune their SIEM alerts and close visibility gaps.
Strategic Remediation Roadmap: Actionable, prioritized engineering steps to patch misconfigurations, harden Active Directory security groups, and eliminate critical internal attack paths.
Core Testing Methodologies
Spearphishing & Initial Foothold Generation
Adversary-in-the-Middle (AiTM) MFA Bypasses
Active Directory Enumeration & BloodHound Mapping
Identity & Privilege Escalation (Kerberoasting, Misconfigured ACLs)
Network Pivot, Data Exfiltration & Domain Dominance
$250