Supabase security check for Lovable, Bolt and v0 appsTrung Thanh Tran
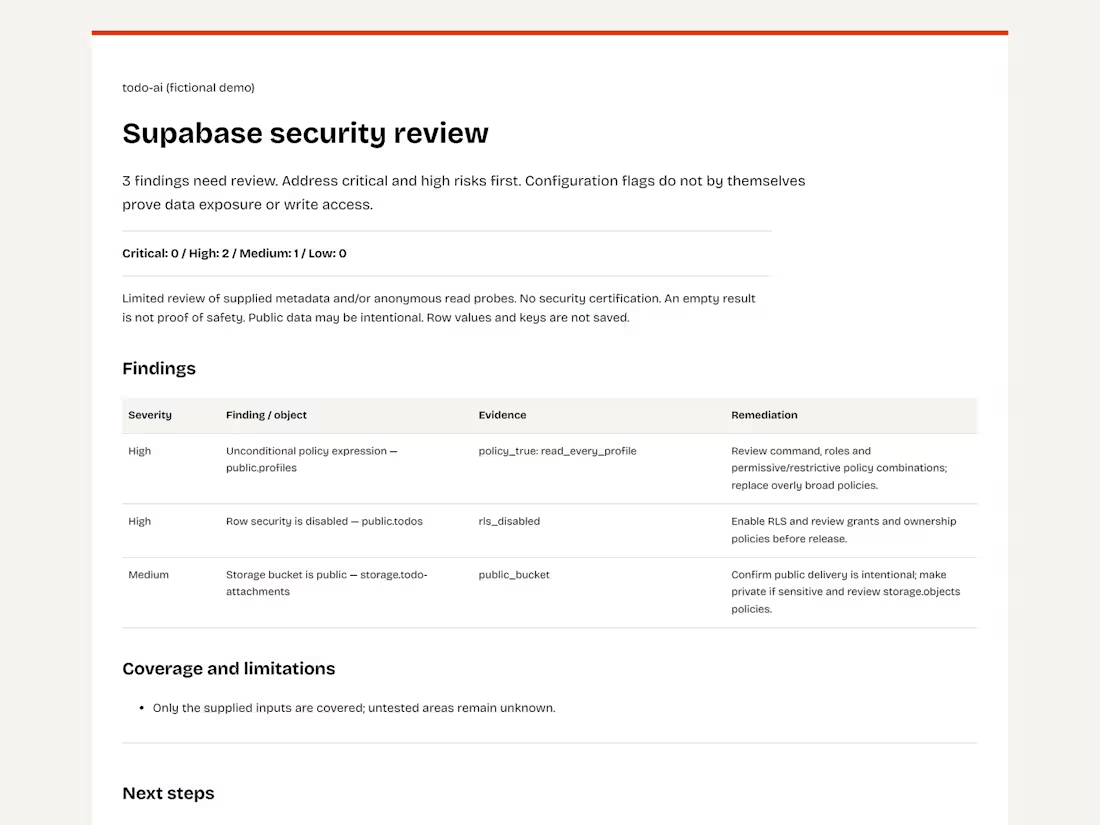
Apps built with Lovable, Bolt or v0 often ship with tables that anyone holding the public anon key can read. That key sits in your site's JavaScript, so this is easy to find for anyone who looks.
I check your project the safe way. You run one read-only SQL query in your Supabase SQL Editor and send me the result. It returns table and policy metadata only, never your users' rows. From that I write a short report and a fix script you review before running.
What I look for
tables in the public schema with Row Level Security turned off
policies that are just true, or that let signed-out users read sensitive tables
SECURITY DEFINER functions the anon key can call through the REST rpc endpoint
definer functions without a fixed search_path, and views that bypass RLS
public Storage buckets
a service_role key left in your frontend code (Standard)
What you get
a report (PDF and HTML) with each finding, its severity, the evidence and how to fix it, written so a non-developer can follow it
fix.sql that enables RLS with owner-only policy templates, wrapped in a transaction that rolls back until you review it
Standard adds a read-only test of your live API with the anon key (one row per table, values never stored), a scan of your frontend for leaked keys, and one re-check after you apply fixes
You never send me a password or your service_role key. I don't change your database; you run the fix script yourself after reading it.
This is a focused configuration review, not a penetration test or a certification. I need your written OK as the project owner before any live check.
Price: $69 for the SQL review (2 days). Standard with the live checks and one re-check is $139 (3 days). Message me and I will send a custom offer.
Starting at$69
Duration2 days
Tags
Supabase
Service provided by
Trung Thanh Tran Ho Chi Minh City, Vietnam
Supabase security check for Lovable, Bolt and v0 appsTrung Thanh Tran
Starting at$69
Duration2 days
Tags
Supabase
Apps built with Lovable, Bolt or v0 often ship with tables that anyone holding the public anon key can read. That key sits in your site's JavaScript, so this is easy to find for anyone who looks.
I check your project the safe way. You run one read-only SQL query in your Supabase SQL Editor and send me the result. It returns table and policy metadata only, never your users' rows. From that I write a short report and a fix script you review before running.
What I look for
tables in the public schema with Row Level Security turned off
policies that are just true, or that let signed-out users read sensitive tables
SECURITY DEFINER functions the anon key can call through the REST rpc endpoint
definer functions without a fixed search_path, and views that bypass RLS
public Storage buckets
a service_role key left in your frontend code (Standard)
What you get
a report (PDF and HTML) with each finding, its severity, the evidence and how to fix it, written so a non-developer can follow it
fix.sql that enables RLS with owner-only policy templates, wrapped in a transaction that rolls back until you review it
Standard adds a read-only test of your live API with the anon key (one row per table, values never stored), a scan of your frontend for leaked keys, and one re-check after you apply fixes
You never send me a password or your service_role key. I don't change your database; you run the fix script yourself after reading it.
This is a focused configuration review, not a penetration test or a certification. I need your written OK as the project owner before any live check.
Price: $69 for the SQL review (2 days). Standard with the live checks and one re-check is $139 (3 days). Message me and I will send a custom offer.
$69