API & Web Application TesterAbdullah
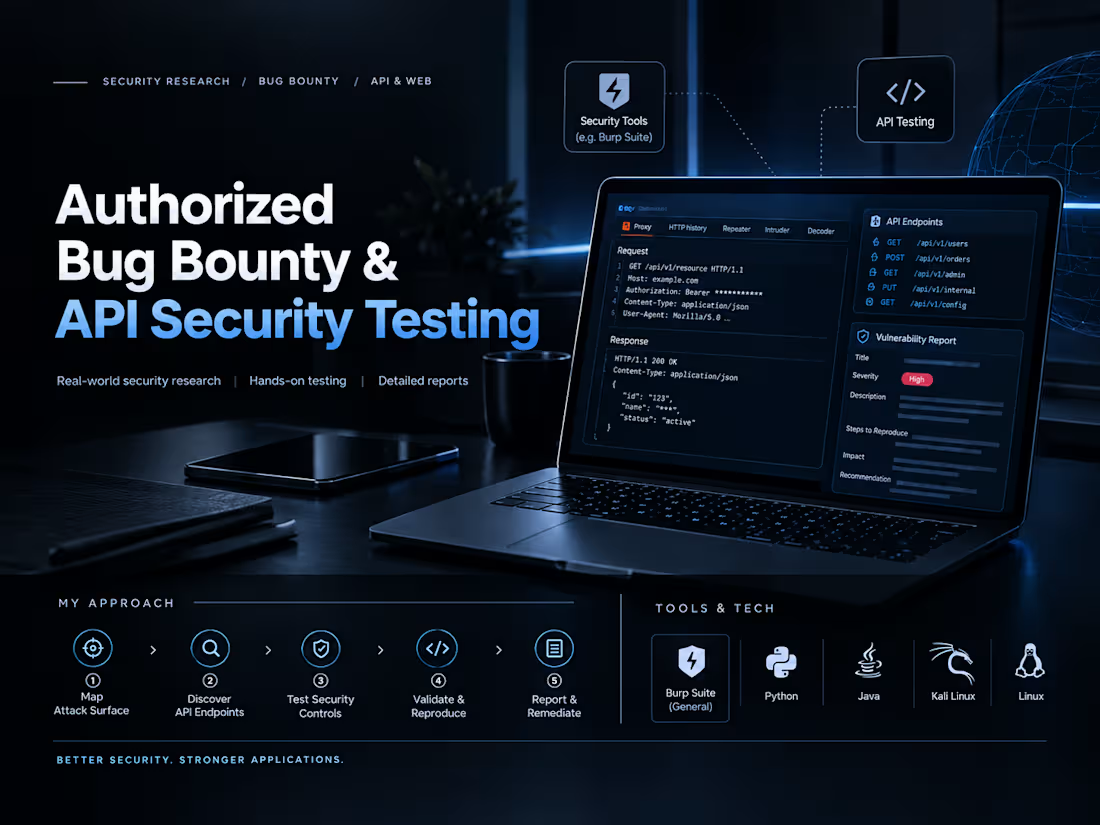
I provide manual security testing for APIs and web applications to identify vulnerabilities before they can be exploited.
What I Test
API Security
Authentication & session management
Authorization and access control
BOLA/IDOR and privilege escalation
Input validation and injection
Rate limiting and abuse cases
API endpoint and parameter testing
Business logic vulnerabilities
Sensitive data exposure
Web Application Security
Authentication and authorization
Access control vulnerabilities
XSS and injection vulnerabilities
Session and security configuration issues
File upload and input handling
Business logic flaws
Sensitive information exposure
Common OWASP application security issues
My Approach
I start with reconnaissance and attack-surface mapping, then manually test application functionality and security controls. For each confirmed vulnerability, I provide clear reproduction steps, evidence, impact, and remediation guidance.
Deliverables
Security findings with severity
Reproducible proof-of-concept steps
Screenshots/evidence where appropriate
Impact assessment
Recommended remediation
Professional security report
I focus on practical, reproducible findings rather than automated scanner output alone.
FAQs
Abdullah's other services
Contact for pricing
Duration1 week
Tags
AI Agents
Reporting
Application Security Tester
BurpSuite
Recon Tools
Security Tester
Top Vulns
Service provided by
Abdullah Peshawar, Pakistan
API & Web Application TesterAbdullah
Contact for pricing
Duration1 week
Tags
AI Agents
Reporting
Application Security Tester
BurpSuite
Recon Tools
Security Tester
Top Vulns
I provide manual security testing for APIs and web applications to identify vulnerabilities before they can be exploited.
What I Test
API Security
Authentication & session management
Authorization and access control
BOLA/IDOR and privilege escalation
Input validation and injection
Rate limiting and abuse cases
API endpoint and parameter testing
Business logic vulnerabilities
Sensitive data exposure
Web Application Security
Authentication and authorization
Access control vulnerabilities
XSS and injection vulnerabilities
Session and security configuration issues
File upload and input handling
Business logic flaws
Sensitive information exposure
Common OWASP application security issues
My Approach
I start with reconnaissance and attack-surface mapping, then manually test application functionality and security controls. For each confirmed vulnerability, I provide clear reproduction steps, evidence, impact, and remediation guidance.
Deliverables
Security findings with severity
Reproducible proof-of-concept steps
Screenshots/evidence where appropriate
Impact assessment
Recommended remediation
Professional security report
I focus on practical, reproducible findings rather than automated scanner output alone.
FAQs
Abdullah's other services
Contact for pricing