AWS Infrastructure Setup with Terraform (VPC, Staging Env, IAM)Dishant Arora
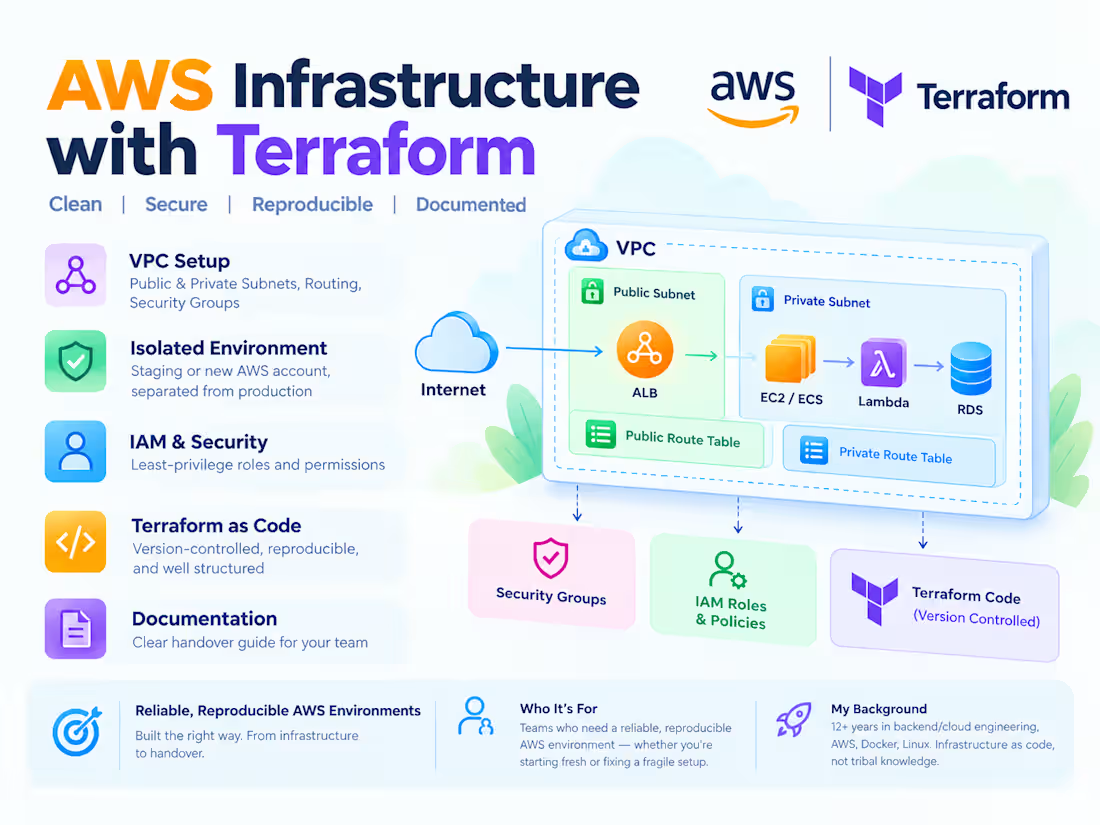
I'll set up a clean, isolated AWS environment for your application using Terraform - infrastructure as code, not manual console clicks that no one can reproduce later.
What you get:
A properly structured VPC (public/private subnets, routing, security groups)
An isolated environment (staging or new account), separated from production
IAM roles and permissions following least-privilege principles
Everything defined in Terraform, version-controlled, and documented
A short handover doc explaining the setup
Who this is for:
Teams who need a reliable, reproducible AWS environment set up correctly the first time - whether you're starting fresh or fixing a manually-built setup that's become fragile.
My background: 12+ years in backend/cloud engineering, including hands-on AWS (Lambda, API Gateway, EC2), Docker, and Linux server administration. I write infrastructure as code so your setup is documented and repeatable, not tribal knowledge.
Message me with your current stack and what you're trying to achieve, and I'll confirm scope before we start.
FAQs
Contact for pricing
Duration1 week
Tags
AWS Lambda
Docker
GitHub
GitHub Actions
Terraform

Amazon Web Services
CI/CD
DevOps Engineer
AWS EC2
Service provided by
Dishant Arora Delhi, India
AWS Infrastructure Setup with Terraform (VPC, Staging Env, IAM)Dishant Arora
Contact for pricing
Duration1 week
Tags
AWS Lambda
Docker
GitHub
GitHub Actions
Terraform
Amazon Web Services
CI/CD
DevOps Engineer
AWS EC2
I'll set up a clean, isolated AWS environment for your application using Terraform - infrastructure as code, not manual console clicks that no one can reproduce later.
What you get:
A properly structured VPC (public/private subnets, routing, security groups)
An isolated environment (staging or new account), separated from production
IAM roles and permissions following least-privilege principles
Everything defined in Terraform, version-controlled, and documented
A short handover doc explaining the setup
Who this is for:
Teams who need a reliable, reproducible AWS environment set up correctly the first time - whether you're starting fresh or fixing a manually-built setup that's become fragile.
My background: 12+ years in backend/cloud engineering, including hands-on AWS (Lambda, API Gateway, EC2), Docker, and Linux server administration. I write infrastructure as code so your setup is documented and repeatable, not tribal knowledge.
Message me with your current stack and what you're trying to achieve, and I'll confirm scope before we start.
FAQs
Contact for pricing