Software Compliance & Regulatory ReviewNathan Combs
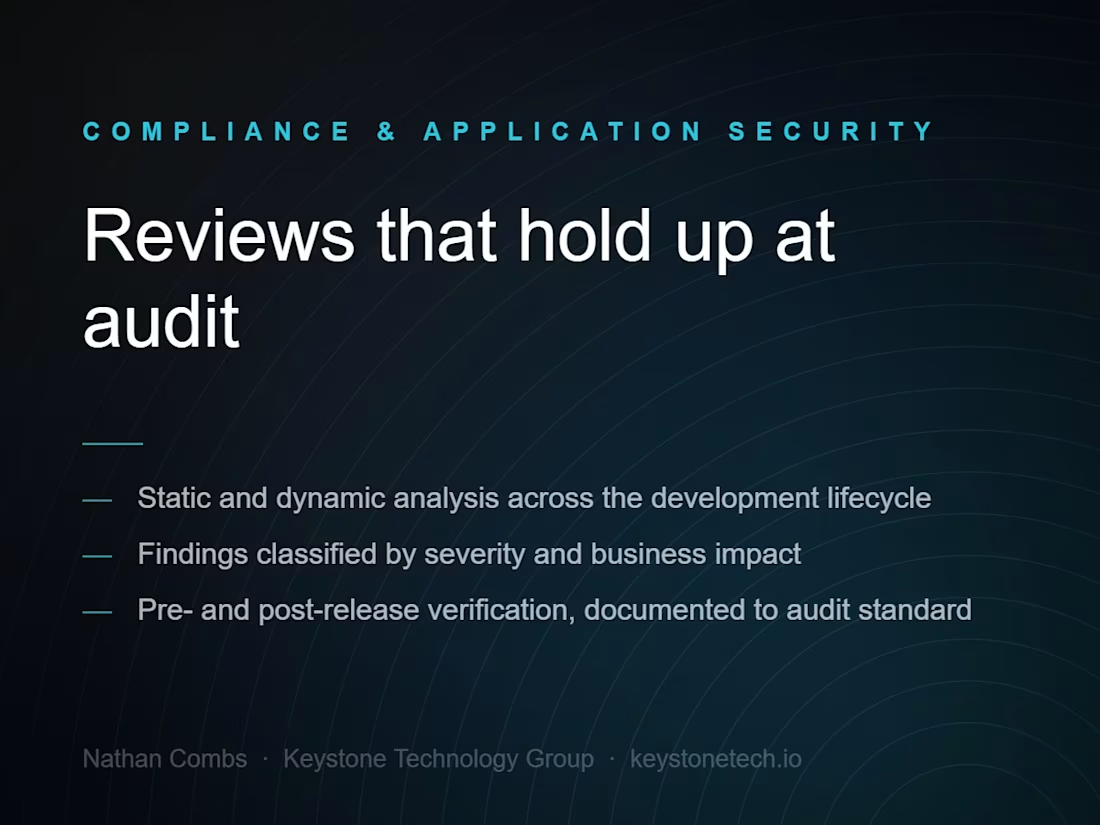
I spent six years as a Software Compliance Analyst at a national mortgage lender - one of the most heavily regulated software environments in the United States. I was the person who decided whether a release met the bar. What that looked like: static and dynamic analysis of applications across the full development lifecycle, validated against both external regulatory requirements and internal controls. Findings classified by severity with business impact and required corrections. Remediation worked through directly with the engineering teams, not handed off as a ticket. Pre- and post-release verification to confirm the fix actually landed. Everything documented to internal audit, regulatory and industry standards, because in that environment a finding you cannot evidence did not happen. What you get: a defensible audit trail, not just a list of issues. I write findings the way an auditor needs to read them, and I can tell you which shortcuts are cheap now and expensive at review. I am also a working engineer, which means I can propose fixes that are actually buildable rather than throwing findings over a wall. If your product touches financial services, healthcare, or anything with a regulator attached, I have spent years on the other side of that review.
Contact for pricing
Duration1 week
Tags
Cybersecurity Specialist
Service provided by
Nathan Combs Detroit, USA
Software Compliance & Regulatory ReviewNathan Combs
Contact for pricing
Duration1 week
Tags
Cybersecurity Specialist
I spent six years as a Software Compliance Analyst at a national mortgage lender - one of the most heavily regulated software environments in the United States. I was the person who decided whether a release met the bar. What that looked like: static and dynamic analysis of applications across the full development lifecycle, validated against both external regulatory requirements and internal controls. Findings classified by severity with business impact and required corrections. Remediation worked through directly with the engineering teams, not handed off as a ticket. Pre- and post-release verification to confirm the fix actually landed. Everything documented to internal audit, regulatory and industry standards, because in that environment a finding you cannot evidence did not happen. What you get: a defensible audit trail, not just a list of issues. I write findings the way an auditor needs to read them, and I can tell you which shortcuts are cheap now and expensive at review. I am also a working engineer, which means I can propose fixes that are actually buildable rather than throwing findings over a wall. If your product touches financial services, healthcare, or anything with a regulator attached, I have spent years on the other side of that review.
Contact for pricing