Supabase Security Review: Row-Level Security, Auth & FunctionsRimon Debnath
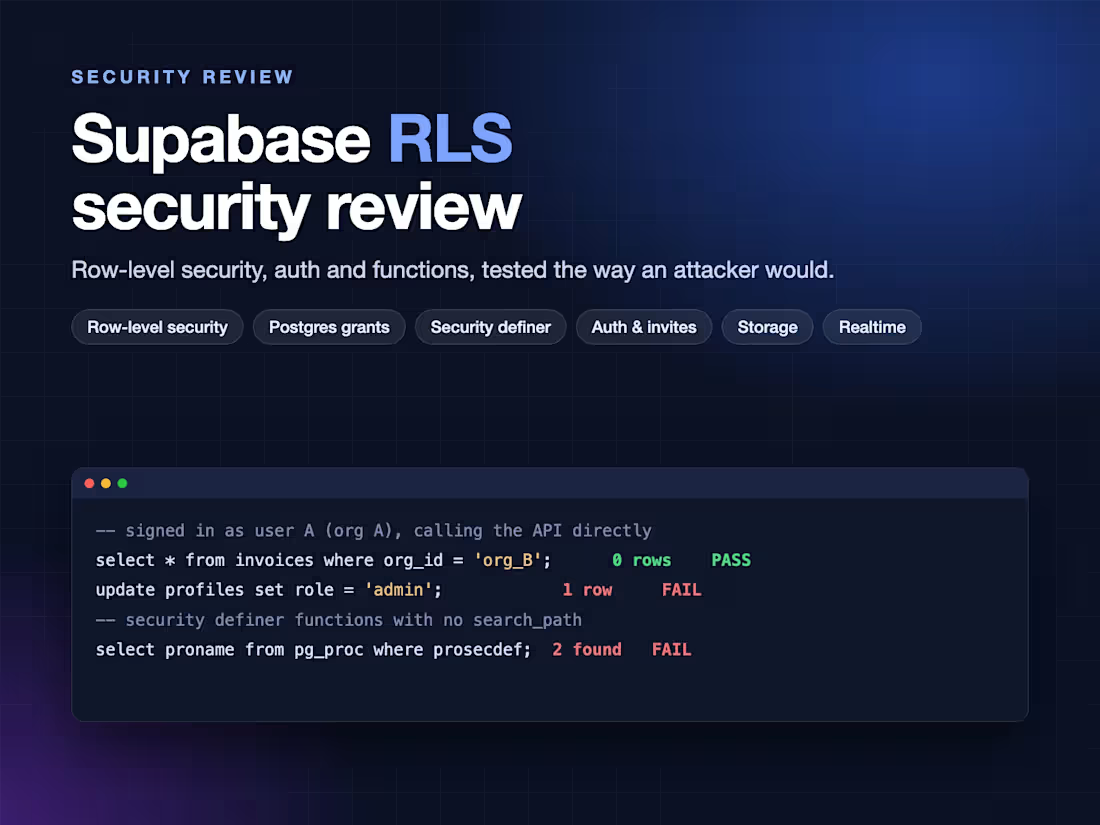
Built on Supabase, or on Lovable or Bolt with a Supabase backend? Your public anon key ships in every visitor's browser, so row-level security is the only thing between one user and everyone else's data. I'll test it the way an attacker would.
What I check
Tables with RLS off or no policies, UPDATE policies missing WITH CHECK, and grants to anon and authenticated
SECURITY DEFINER functions without a fixed search_path, or still callable by anon
Role tests as anon and as each demo user, straight against the REST/RPC API, storage and realtime: can user A read or change org B's rows, or change their own role?
Sign-in codes and invitations (expiry, reuse, rate limits), server routes and service-role key use
What you get
A report ranked by severity, with proof and a fix for each finding
A re-runnable SQL test script, so you can re-check after fixing
A call to walk through the results
Pricing: $150 for the RLS, grants and functions pass (about 2 days). The full review, adding auth flows, invitations, server routes and the call, is $400 (about 5 days).
To be upfront: I'm not a certified auditor. My proof is Locus, my open-source Next.js + Supabase app with RLS on every table and a 174-assertion test suite for tenant isolation: github.com/Rimonok12/Locus
To start I need a schema dump without data (or read-only access), one demo account per role and the app URL. Write tests only ever run on demo accounts or a staging/branch database.
Example work
Rimon's other services
Starting at$150
Duration1 week
Tags
Lovable
Next.js
PostgreSQL
SQL
Supabase
Backend Engineer
Database Engineer
Service provided by
Rimon Debnath Brahmanbaria, Bangladesh
- 2
- Followers
Supabase Security Review: Row-Level Security, Auth & FunctionsRimon Debnath
Starting at$150
Duration1 week
Tags
Lovable
Next.js
PostgreSQL
SQL
Supabase
Backend Engineer
Database Engineer
Built on Supabase, or on Lovable or Bolt with a Supabase backend? Your public anon key ships in every visitor's browser, so row-level security is the only thing between one user and everyone else's data. I'll test it the way an attacker would.
What I check
Tables with RLS off or no policies, UPDATE policies missing WITH CHECK, and grants to anon and authenticated
SECURITY DEFINER functions without a fixed search_path, or still callable by anon
Role tests as anon and as each demo user, straight against the REST/RPC API, storage and realtime: can user A read or change org B's rows, or change their own role?
Sign-in codes and invitations (expiry, reuse, rate limits), server routes and service-role key use
What you get
A report ranked by severity, with proof and a fix for each finding
A re-runnable SQL test script, so you can re-check after fixing
A call to walk through the results
Pricing: $150 for the RLS, grants and functions pass (about 2 days). The full review, adding auth flows, invitations, server routes and the call, is $400 (about 5 days).
To be upfront: I'm not a certified auditor. My proof is Locus, my open-source Next.js + Supabase app with RLS on every table and a 174-assertion test suite for tenant isolation: github.com/Rimonok12/Locus
To start I need a schema dump without data (or read-only access), one demo account per role and the app URL. Write tests only ever run on demo accounts or a staging/branch database.
Example work
Rimon's other services
$150