HIPAA-Compliant Healthcare SaaS MVP DevelopmentKamal Berriga
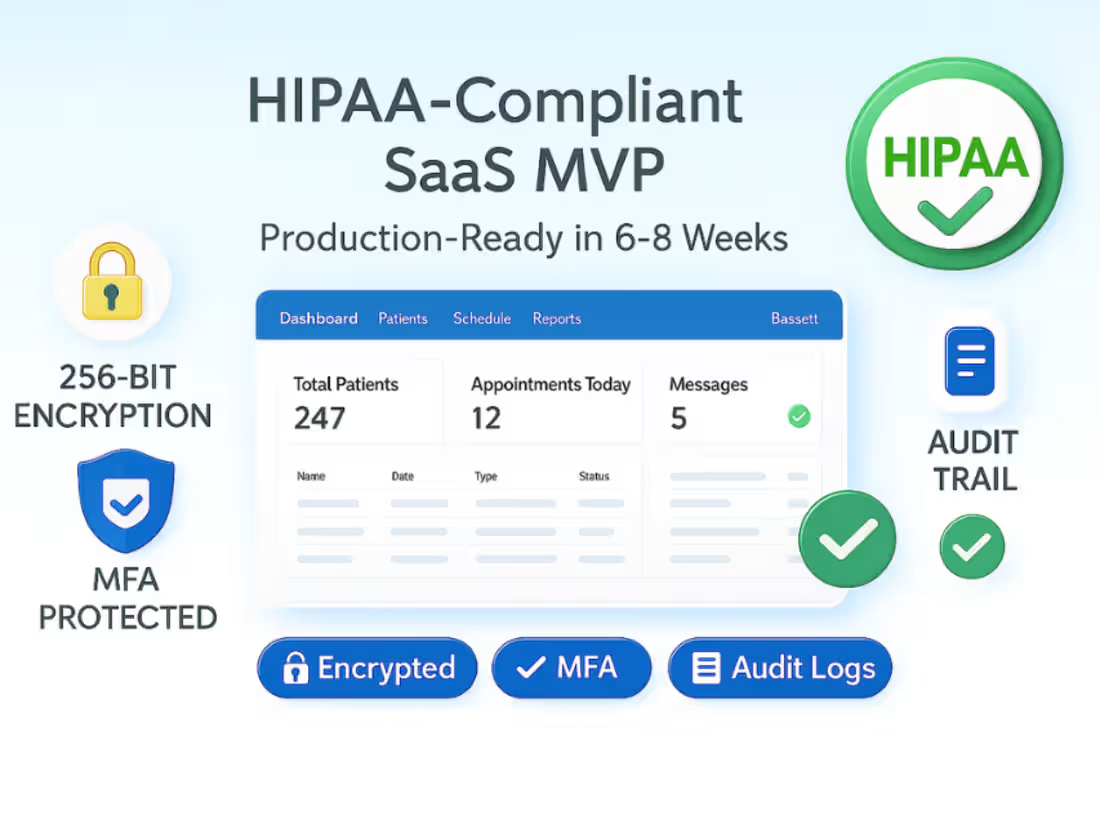
Launch your healthcare SaaS with built-in HIPAA compliance. I deliver secure patient portals, telemedicine platforms, or EHR systems with encryption, MFA, audit logs, and HIPAA-ready AWS hosting. No legal/compliance consulting—just production-ready technical infrastructure that passes security audits. 6-8 weeks from start to launch.
What's included
Technical Specification & Architecture Document
Comprehensive technical blueprint covering system architecture, database schema with PHI data mapping, API endpoints documentation, and security implementation details. Includes architecture diagrams showing data flow, encryption layers, and access control structure to demonstrate HIPAA compliance to auditors, investors, or future developers.
Secure Authentication with Multi-Factor Authentication (MFA)
Production-ready user authentication system with email/password login, mandatory multi-factor authentication (SMS or authenticator app), role-based access control for different user types (Admin, Provider, Patient), automatic session timeout after 15 minutes of inactivity, and password complexity requirements meeting HIPAA security standards.
End-to-End Encryption Implementation
AES-256 encryption for all Protected Health Information stored in the database, TLS 1.3 for data transmission between client and server, encrypted automated database backups, and AWS KMS for encryption key management. All PHI is encrypted at rest and in transit, meeting HIPAA encryption requirements.
Comprehensive Audit Logging System
Automated audit trail capturing all user actions including login/logout, PHI access, data modifications, and deletions with timestamp, user ID, IP address, and action type. Searchable audit log viewer in admin dashboard with filtering by date, user, or action type, plus export capability for compliance documentation during audits.
Full-Stack Web Application (Backend + Frontend)
Complete healthcare application built with Node.js/NestJS backend and React/Next.js frontend, including patient portal for viewing records and appointments, provider dashboard for managing patient data, admin panel for user management and system monitoring, and your core healthcare features (patient records, scheduling, secure messaging, document uploads, etc.).
HIPAA-Eligible AWS Cloud Infrastructure
Secure cloud infrastructure on AWS including encrypted RDS PostgreSQL database, private VPC with proper security groups, encrypted S3 buckets for file storage, CloudWatch logging and monitoring, automated encrypted backups with 30-day retention, and production-grade hosting that meets HIPAA technical safeguards. Deployed in your AWS account for full ownership.
Admin Dashboard with User Management
Comprehensive admin panel for managing users, viewing audit logs, monitoring system activity, and managing permissions. Includes user creation/deletion, role assignment, activity reports, and system health monitoring.
Role-Based Access Control (RBAC) System
Permission system with predefined user roles (Admin, Provider, Patient) where each role has specific access rights to different data and features. Users only see information they're authorized to access.
Secure File Upload & Storage
Encrypted document upload system for medical records, lab results, and other files. Files automatically encrypted before storage in AWS S3, with access controls ensuring only authorized users can download. Includes file type validation and size limits.
Payment Integration (Stripe - if needed)
Stripe payment processing for patient billing, subscription management, or co-pays. Payment data handled by Stripe (not stored in your database), meeting both HIPAA and PCI-DSS requirements.
Automated Encrypted Backup System
Daily automated backups of database and files to encrypted AWS S3 storage with 30-day retention. Includes documented backup restoration procedure to recover data if needed.
Security Monitoring & Alert System
Automated monitoring for failed login attempts (5+ failures = account lockout), unusual access patterns, and system errors. Email alerts sent to admin for security events requiring attention.
Mobile-Responsive Interface
Fully responsive design working on mobile phones, tablets, and desktop computers. Tested on Chrome, Safari, Firefox, and Edge browsers with mobile-first approach for healthcare providers on the go.
Email Notification System
Transactional email system using AWS SES or SendGrid for password resets, account security alerts, and appointment reminders. Emails designed to never include PHI in content, only secure portal links.
Database Schema with PHI Protection
PostgreSQL database with proper indexing, relationships, and PHI fields clearly identified and encrypted. Includes database migration scripts and seed data for testing.
Production Deployment with SSL Certificate
Live deployment to AWS with custom domain, SSL/TLS certificate for HTTPS, and basic CDN setup. Includes staging environment for testing updates before production deployment.
Security Best Practices Implementation
Production-ready application following OWASP security guidelines including SQL injection prevention, XSS attack protection, CSRF token implementation, rate limiting on API endpoints, secure session management, and input validation on all forms. Code reviewed for common security vulnerabilities before deployment.
Source Code & Technical Documentation
Full source code ownership via private GitHub repository with README, setup instructions, environment configuration guide, deployment documentation, and inline code comments explaining HIPAA-related security implementations.
HIPAA Security Implementation Guide
Technical documentation explaining how your application implements HIPAA security safeguards including encryption methods, access controls, audit logging, authentication, and data backup procedures. Useful for demonstrating compliance to auditors, investors, or healthcare partners who need to understand your security architecture.
2 Weeks Post-Launch Support
Two weeks of email support after launch for bug fixes, minor adjustments, technical questions, and guidance on maintaining security. Includes help with AWS account setup if needed.
FAQs
Kamal's other services
Starting at$26,000
Duration8 weeks
Tags
AWS
Intelligence

Next.js
Node.js
PostgreSQL
Fullstack Engineer
Web Developer
Service provided by
Kamal Berriga proAgadir 80000, Morocco
HIPAA-Compliant Healthcare SaaS MVP DevelopmentKamal Berriga
Starting at$26,000
Duration8 weeks
Tags
AWS
Intelligence
Next.js
Node.js
PostgreSQL
Fullstack Engineer
Web Developer
Launch your healthcare SaaS with built-in HIPAA compliance. I deliver secure patient portals, telemedicine platforms, or EHR systems with encryption, MFA, audit logs, and HIPAA-ready AWS hosting. No legal/compliance consulting—just production-ready technical infrastructure that passes security audits. 6-8 weeks from start to launch.
What's included
Technical Specification & Architecture Document
Comprehensive technical blueprint covering system architecture, database schema with PHI data mapping, API endpoints documentation, and security implementation details. Includes architecture diagrams showing data flow, encryption layers, and access control structure to demonstrate HIPAA compliance to auditors, investors, or future developers.
Secure Authentication with Multi-Factor Authentication (MFA)
Production-ready user authentication system with email/password login, mandatory multi-factor authentication (SMS or authenticator app), role-based access control for different user types (Admin, Provider, Patient), automatic session timeout after 15 minutes of inactivity, and password complexity requirements meeting HIPAA security standards.
End-to-End Encryption Implementation
AES-256 encryption for all Protected Health Information stored in the database, TLS 1.3 for data transmission between client and server, encrypted automated database backups, and AWS KMS for encryption key management. All PHI is encrypted at rest and in transit, meeting HIPAA encryption requirements.
Comprehensive Audit Logging System
Automated audit trail capturing all user actions including login/logout, PHI access, data modifications, and deletions with timestamp, user ID, IP address, and action type. Searchable audit log viewer in admin dashboard with filtering by date, user, or action type, plus export capability for compliance documentation during audits.
Full-Stack Web Application (Backend + Frontend)
Complete healthcare application built with Node.js/NestJS backend and React/Next.js frontend, including patient portal for viewing records and appointments, provider dashboard for managing patient data, admin panel for user management and system monitoring, and your core healthcare features (patient records, scheduling, secure messaging, document uploads, etc.).
HIPAA-Eligible AWS Cloud Infrastructure
Secure cloud infrastructure on AWS including encrypted RDS PostgreSQL database, private VPC with proper security groups, encrypted S3 buckets for file storage, CloudWatch logging and monitoring, automated encrypted backups with 30-day retention, and production-grade hosting that meets HIPAA technical safeguards. Deployed in your AWS account for full ownership.
Admin Dashboard with User Management
Comprehensive admin panel for managing users, viewing audit logs, monitoring system activity, and managing permissions. Includes user creation/deletion, role assignment, activity reports, and system health monitoring.
Role-Based Access Control (RBAC) System
Permission system with predefined user roles (Admin, Provider, Patient) where each role has specific access rights to different data and features. Users only see information they're authorized to access.
Secure File Upload & Storage
Encrypted document upload system for medical records, lab results, and other files. Files automatically encrypted before storage in AWS S3, with access controls ensuring only authorized users can download. Includes file type validation and size limits.
Payment Integration (Stripe - if needed)
Stripe payment processing for patient billing, subscription management, or co-pays. Payment data handled by Stripe (not stored in your database), meeting both HIPAA and PCI-DSS requirements.
Automated Encrypted Backup System
Daily automated backups of database and files to encrypted AWS S3 storage with 30-day retention. Includes documented backup restoration procedure to recover data if needed.
Security Monitoring & Alert System
Automated monitoring for failed login attempts (5+ failures = account lockout), unusual access patterns, and system errors. Email alerts sent to admin for security events requiring attention.
Mobile-Responsive Interface
Fully responsive design working on mobile phones, tablets, and desktop computers. Tested on Chrome, Safari, Firefox, and Edge browsers with mobile-first approach for healthcare providers on the go.
Email Notification System
Transactional email system using AWS SES or SendGrid for password resets, account security alerts, and appointment reminders. Emails designed to never include PHI in content, only secure portal links.
Database Schema with PHI Protection
PostgreSQL database with proper indexing, relationships, and PHI fields clearly identified and encrypted. Includes database migration scripts and seed data for testing.
Production Deployment with SSL Certificate
Live deployment to AWS with custom domain, SSL/TLS certificate for HTTPS, and basic CDN setup. Includes staging environment for testing updates before production deployment.
Security Best Practices Implementation
Production-ready application following OWASP security guidelines including SQL injection prevention, XSS attack protection, CSRF token implementation, rate limiting on API endpoints, secure session management, and input validation on all forms. Code reviewed for common security vulnerabilities before deployment.
Source Code & Technical Documentation
Full source code ownership via private GitHub repository with README, setup instructions, environment configuration guide, deployment documentation, and inline code comments explaining HIPAA-related security implementations.
HIPAA Security Implementation Guide
Technical documentation explaining how your application implements HIPAA security safeguards including encryption methods, access controls, audit logging, authentication, and data backup procedures. Useful for demonstrating compliance to auditors, investors, or healthcare partners who need to understand your security architecture.
2 Weeks Post-Launch Support
Two weeks of email support after launch for bug fixes, minor adjustments, technical questions, and guidance on maintaining security. Includes help with AWS account setup if needed.
FAQs
Kamal's other services
$26,000