
AI Production Readiness AuditEhtasham Ali
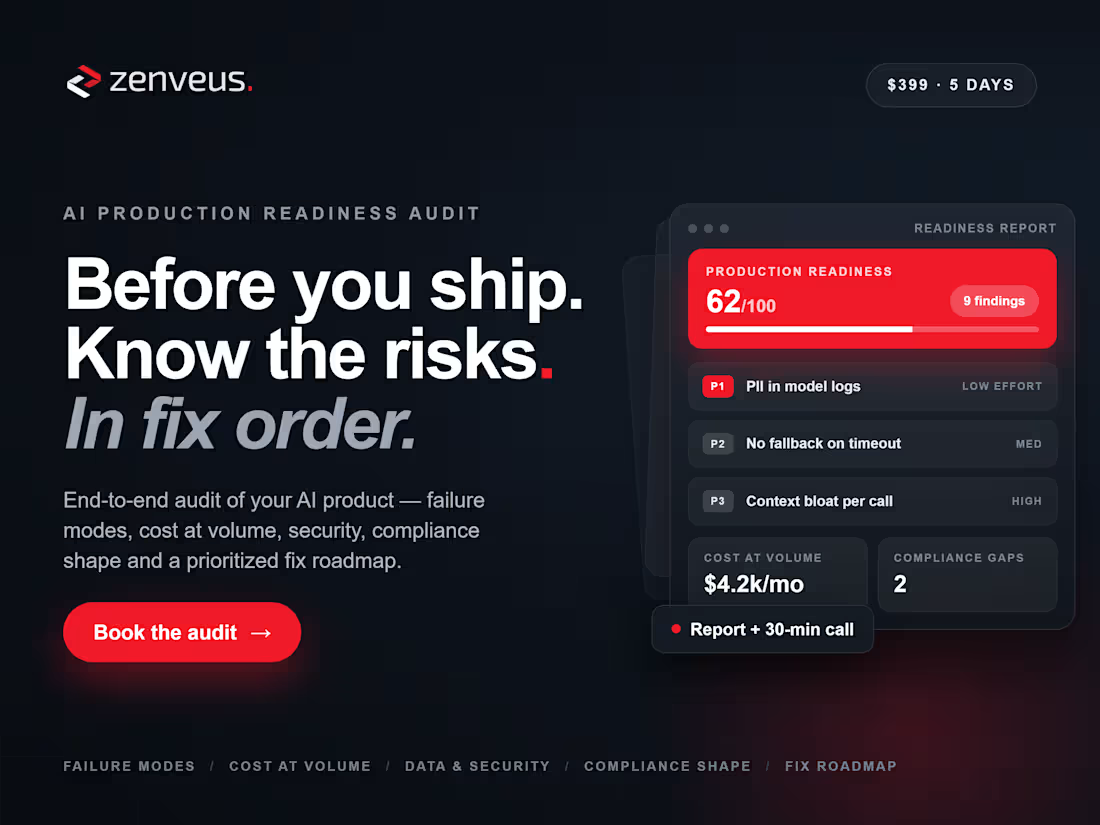
This is the audit for when more than one feature is on the line, a product with AI running through it, an MVP about to take on real customers, or a feature someone else built that you've inherited and don't fully trust.
I go through the system end to end and come back with a written report plus a call to walk through it together. The report covers:
Failure modes — the specific ways this breaks under real traffic, bad input, or edge cases the demo never hit
Cost — a per-call and monthly estimate at your expected volume, and where the spend is going
Data and security — what's exposed, what isn't logged that should be, what a security review would flag
Compliance shape — if you're in health, finance, insurance or another regulated space, whether the architecture is even compatible with HIPAA/SOC 2/KYC-type requirements, and what's missing
A prioritized roadmap — every issue ranked by risk and effort, so you know what to fix first and what can wait
You get the written report first, then a 30-minute call to go through it, ask questions, and leave with a clear next step, whether that's you fixing it, your team fixing it, or bringing me in to do it.
This is still a diagnosis, not a build. I'm not implementing fixes as part of this audit, I'm telling you exactly what's wrong, why it matters, and in what order to handle it.
What I need from you: an architecture overview or walkthrough, read-only access to the relevant code, and a rough sense of your expected user volume and data sensitivity (e.g. "handles health records" or "handles payments").
FAQs
Ehtasham's other services
Starting at$399
Duration1 day
Tags
AI Consulting
Cybersecurity Specialist
Generative AI
LLM
AI Architecture
AI Audit
AI Security
SaaS
Technical Consulting
Service provided by
Ehtasham Ali proKarachi, Pakistan
- $25k+
- Earned
- 2
- Paid projects
- 46
- Followers
AI Production Readiness AuditEhtasham Ali
Starting at$399
Duration1 day
Tags
AI Consulting
Cybersecurity Specialist
Generative AI
LLM
AI Architecture
AI Audit
AI Security
SaaS
Technical Consulting
This is the audit for when more than one feature is on the line, a product with AI running through it, an MVP about to take on real customers, or a feature someone else built that you've inherited and don't fully trust.
I go through the system end to end and come back with a written report plus a call to walk through it together. The report covers:
Failure modes — the specific ways this breaks under real traffic, bad input, or edge cases the demo never hit
Cost — a per-call and monthly estimate at your expected volume, and where the spend is going
Data and security — what's exposed, what isn't logged that should be, what a security review would flag
Compliance shape — if you're in health, finance, insurance or another regulated space, whether the architecture is even compatible with HIPAA/SOC 2/KYC-type requirements, and what's missing
A prioritized roadmap — every issue ranked by risk and effort, so you know what to fix first and what can wait
You get the written report first, then a 30-minute call to go through it, ask questions, and leave with a clear next step, whether that's you fixing it, your team fixing it, or bringing me in to do it.
This is still a diagnosis, not a build. I'm not implementing fixes as part of this audit, I'm telling you exactly what's wrong, why it matters, and in what order to handle it.
What I need from you: an architecture overview or walkthrough, read-only access to the relevant code, and a rough sense of your expected user volume and data sensitivity (e.g. "handles health records" or "handles payments").
FAQs
Ehtasham's other services
$399