n8n Integration Assessment and Workflow PlanningJulian Vale
Connect your business systems with a clear workflow specification and a practical test plan. Nexvale LLC is a five-person in-house service team led by Julian Vale, your responsible contact for the brief, scope, review, and handover.
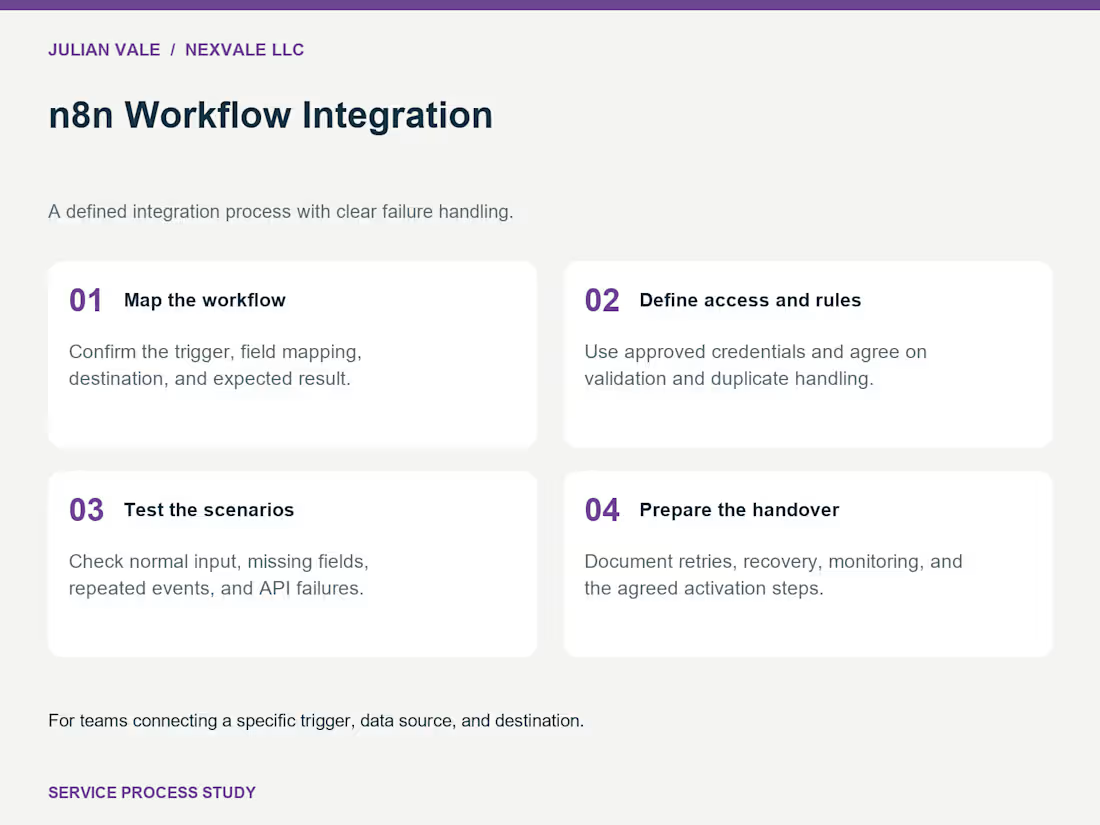
We assess one defined workflow: its trigger, source, destination, field mapping, permissions, and expected result. The plan covers input validation, missing fields, repeated events, credential and API failures, retry behavior, and duplicate-write prevention.
DELIVERABLES
You receive the workflow specification, field mapping and dependency list, failure-handling recommendations, acceptance test cases, and next implementation steps. One consolidated round of revisions within the agreed brief is included.
HOW WE WORK
We confirm the business objective and sample data, map the workflow, review dependencies and failure cases, and agree how success will be tested. One project lead coordinates the work and an organized handover.
WHAT TO SEND
The apps involved, n8n environment, trigger, sanitized sample input, expected output, frequency, any existing workflow, and acceptance criteria. Credentials remain in the agreed credential system.
Our starting hourly rate is USD 30. A fixed-price scope and delivery date follow review of the brief. The displayed duration is an estimate. Build, deployment, live writes, paid tools, and monitoring are separately scoped after review of the actual systems and test environment.
Example work

n8n Integration Assessment and Workflow PlanningJulian Vale
Contact for pricing
Duration1 week
Tags
N8N
Connect your business systems with a clear workflow specification and a practical test plan. Nexvale LLC is a five-person in-house service team led by Julian Vale, your responsible contact for the brief, scope, review, and handover.
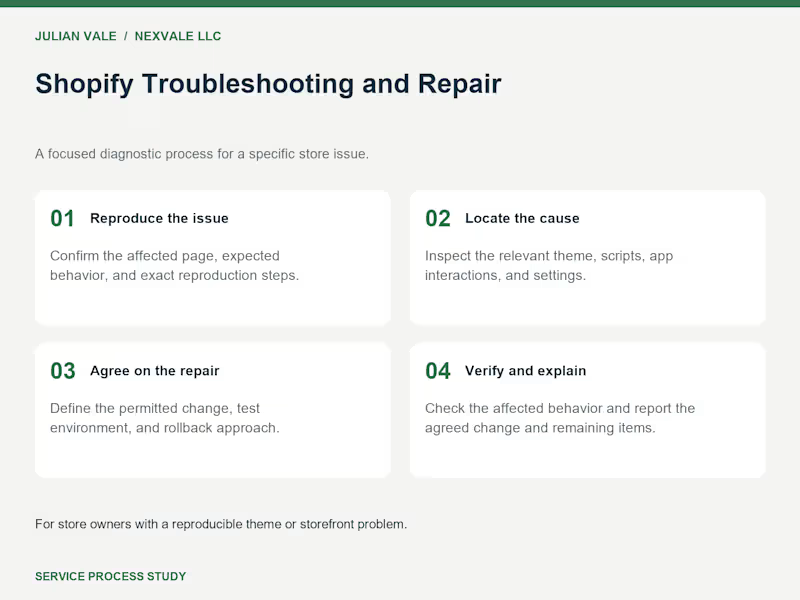
We assess one defined workflow: its trigger, source, destination, field mapping, permissions, and expected result. The plan covers input validation, missing fields, repeated events, credential and API failures, retry behavior, and duplicate-write prevention.
DELIVERABLES
You receive the workflow specification, field mapping and dependency list, failure-handling recommendations, acceptance test cases, and next implementation steps. One consolidated round of revisions within the agreed brief is included.
HOW WE WORK
We confirm the business objective and sample data, map the workflow, review dependencies and failure cases, and agree how success will be tested. One project lead coordinates the work and an organized handover.
WHAT TO SEND
The apps involved, n8n environment, trigger, sanitized sample input, expected output, frequency, any existing workflow, and acceptance criteria. Credentials remain in the agreed credential system.
Our starting hourly rate is USD 30. A fixed-price scope and delivery date follow review of the brief. The displayed duration is an estimate. Build, deployment, live writes, paid tools, and monitoring are separately scoped after review of the actual systems and test environment.
Example work
Contact for pricing