Ship Check: Production Audit for Lovable, Bolt and Replit AppsErgin K
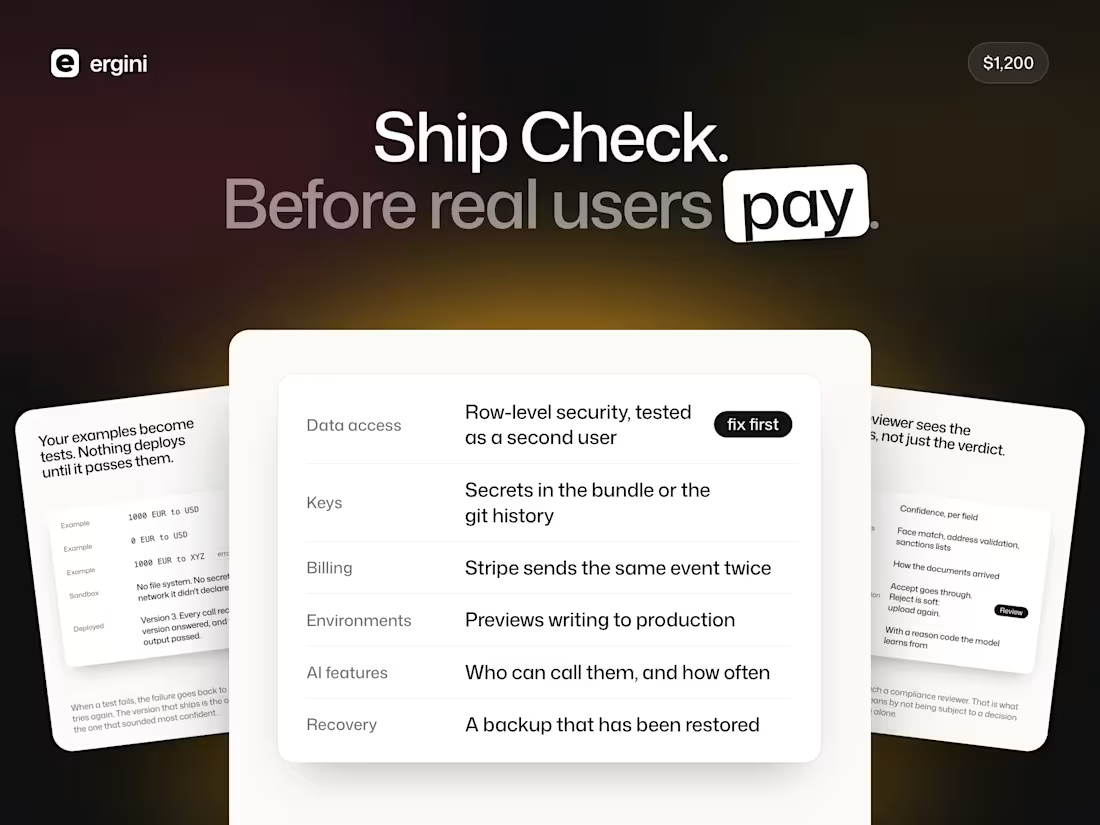
Your app works in the demo. Before more people pay for it, find out what a demo never shows.
Ship Check is a fixed-price audit of an app built in Lovable, Bolt, Replit, v0 or Base44. You get a written report that separates what exposes data or money today from what can wait, and a plan for the first.
Who this is for
Founders with real users, or about to have them, on an app built in Lovable, Bolt, Replit or Base44, and no engineer who has read the code.
Already know what needs building? Start with the Hardening Sprint directly.
What I check
Data access: row-level security on every table, tested as a second user.
Keys: secrets in the browser bundle or in the git history.
Billing: who decides someone has paid, and what happens when Stripe sends the same event twice.
Environments: whether previews and tests write to the production database.
AI features: who can call them, how often, and what a crafted message can pull out.
Recovery: whether a backup has ever been restored.
What you get
A written report with evidence for every finding, ranked by risk.
A fix-first list, and my call on keep, refactor or rebuild for each area.
A 30-minute readout call.
Anything that exposes customer data is flagged the same day, not at the end of the week.
Delivery and fee
Three working days. $1,200 flat. The full fee is credited to a Hardening Sprint that starts within 30 days of the readout.
I do the audit myself. If we fix things afterwards, I write the fixes.
Send me the app link and what's breaking.
FAQs
Starting at$1,200
Duration3 days
Tags
Base44

Bolt.new

GitHub
Lovable
Next.js
Replit
Stripe
Supabase
Vercel
Service provided by
Ergin K proPristina
- 8
- Followers
Ship Check: Production Audit for Lovable, Bolt and Replit AppsErgin K
Starting at$1,200
Duration3 days
Tags
Base44
Bolt.new
GitHub
Lovable
Next.js
Replit
Stripe
Supabase
Vercel
Your app works in the demo. Before more people pay for it, find out what a demo never shows.
Ship Check is a fixed-price audit of an app built in Lovable, Bolt, Replit, v0 or Base44. You get a written report that separates what exposes data or money today from what can wait, and a plan for the first.
Who this is for
Founders with real users, or about to have them, on an app built in Lovable, Bolt, Replit or Base44, and no engineer who has read the code.
Already know what needs building? Start with the Hardening Sprint directly.
What I check
Data access: row-level security on every table, tested as a second user.
Keys: secrets in the browser bundle or in the git history.
Billing: who decides someone has paid, and what happens when Stripe sends the same event twice.
Environments: whether previews and tests write to the production database.
AI features: who can call them, how often, and what a crafted message can pull out.
Recovery: whether a backup has ever been restored.
What you get
A written report with evidence for every finding, ranked by risk.
A fix-first list, and my call on keep, refactor or rebuild for each area.
A 30-minute readout call.
Anything that exposes customer data is flagged the same day, not at the end of the week.
Delivery and fee
Three working days. $1,200 flat. The full fee is credited to a Hardening Sprint that starts within 30 days of the readout.
I do the audit myself. If we fix things afterwards, I write the fixes.
Send me the app link and what's breaking.
FAQs
$1,200