Security audit and fix for Lovable, Bolt, Base44 and Replit appsZakaria MAMOUMI
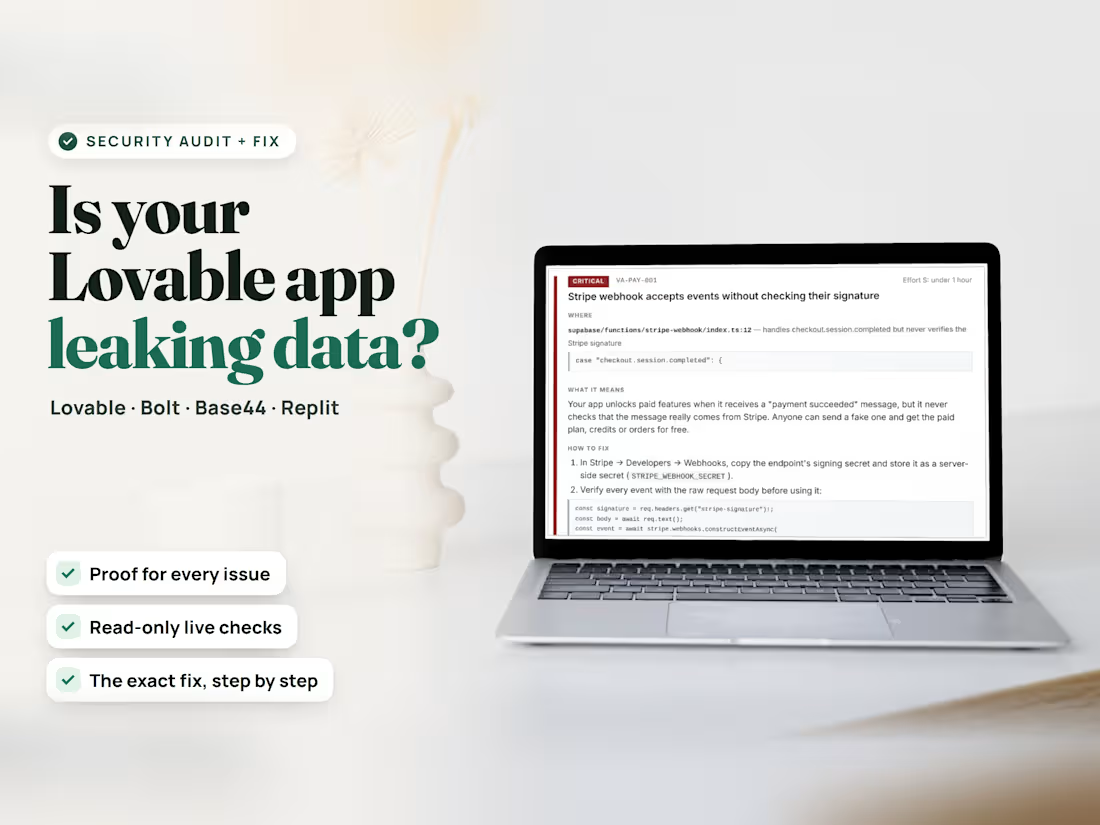
AI app builders get you from idea to live app in a weekend, but a working app can still leave your data open: database tables that anyone with your app's public key can read, secret keys sent to every visitor's browser, payment webhooks that anyone can fake, and AI features that anyone can call on your bill.
In our scan of 40 public apps built with Lovable and Bolt on Supabase (November 2026), 17 had at least one critical issue and 33 at least one high-severity issue.
How we ran it: the public code of 25 Lovable and 15 Bolt apps, read by our scanner, then every critical and high finding checked by hand. No live app was tested, and no app is named.
What you get
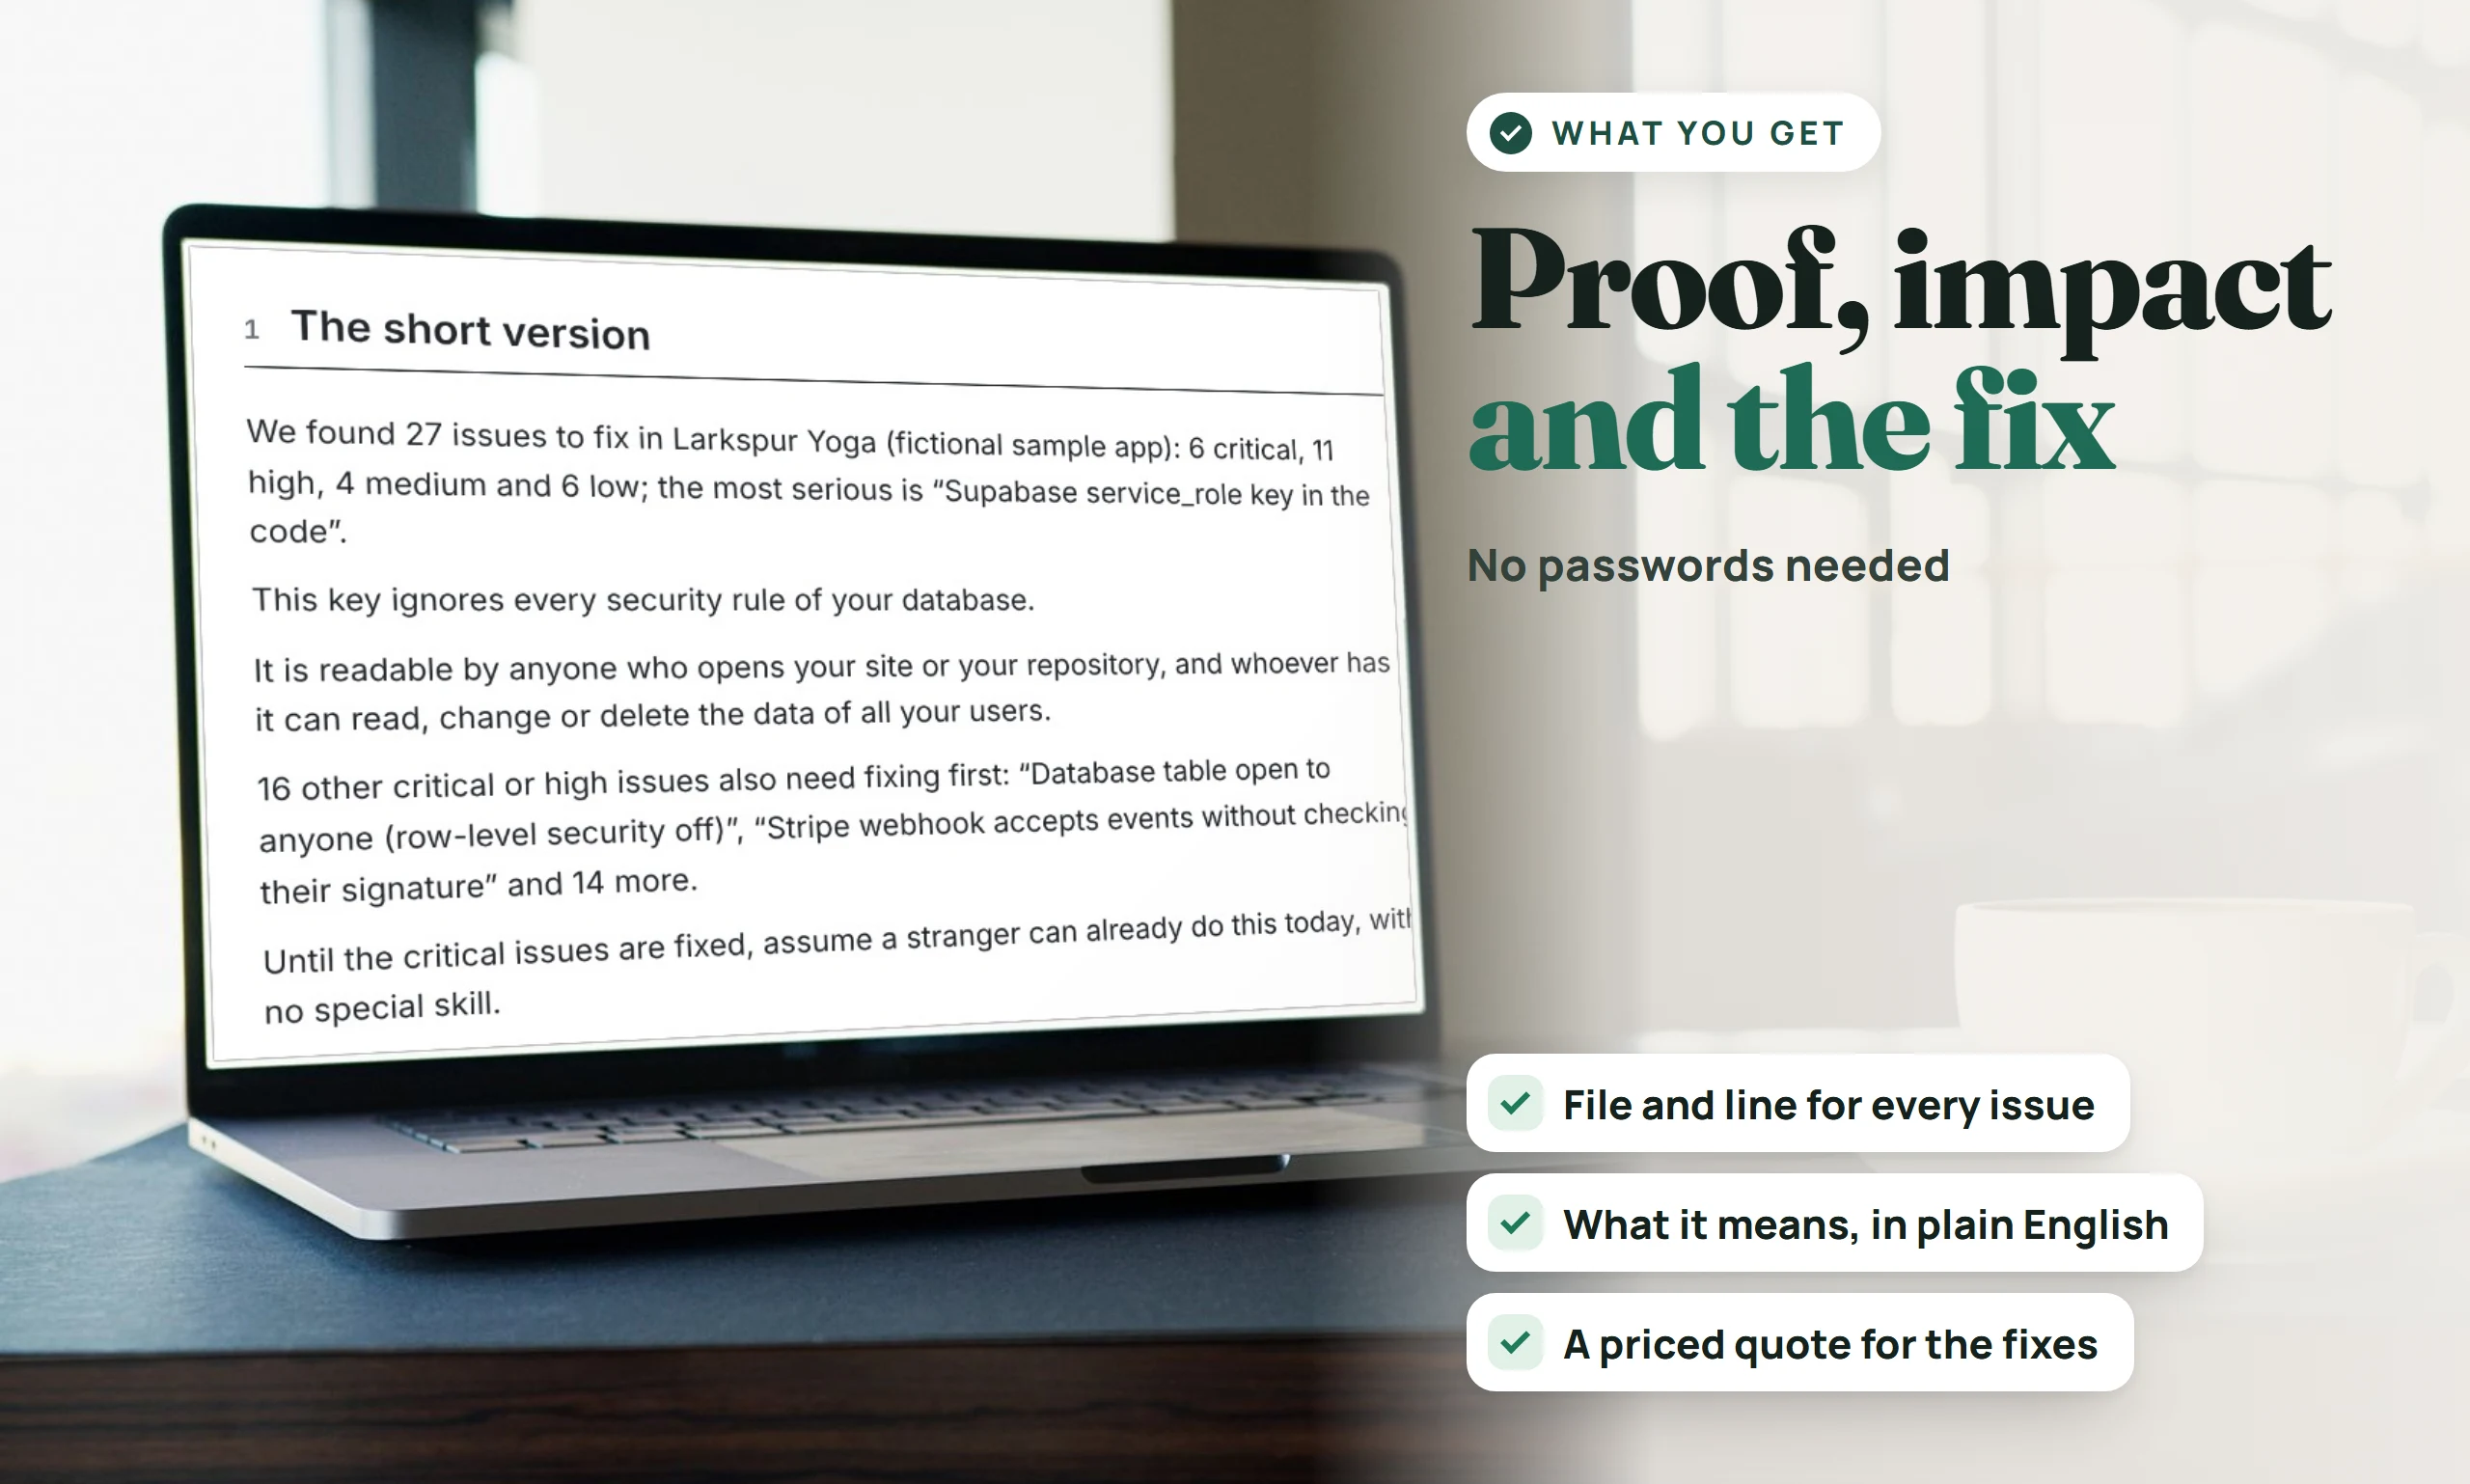
I review your code and, with your signed consent, your live app. You get a report that a non-developer can read in a few minutes:
every problem with proof: the file and line, or the live response
what it means for your business, in plain English
the exact fix, for me or your developer
a priced quote for the fixes
The report comes as a self-contained HTML file and a PDF.
Packages
Security scan + report: $145, delivered in 2 days (this listing)
Audit + urgent fixes: $395, delivered in 5 days. I fix the critical and high issues (up to about 4 hours of work), re-scan to show they are closed, and hand over a short note of what changed.
Full hardening + 1 month monitoring: $795, delivered in 10 days. I fix every issue above "info" level (up to 10 hours of work), re-scan, hand over a note, and the first month of monitoring is included.
Extra fixes are quoted from the report, from $250. Monitoring after the first month: $49/month, because each new prompt to your builder can reopen a hole. For the $395 or $795 package, message me here on Contra.
What I check
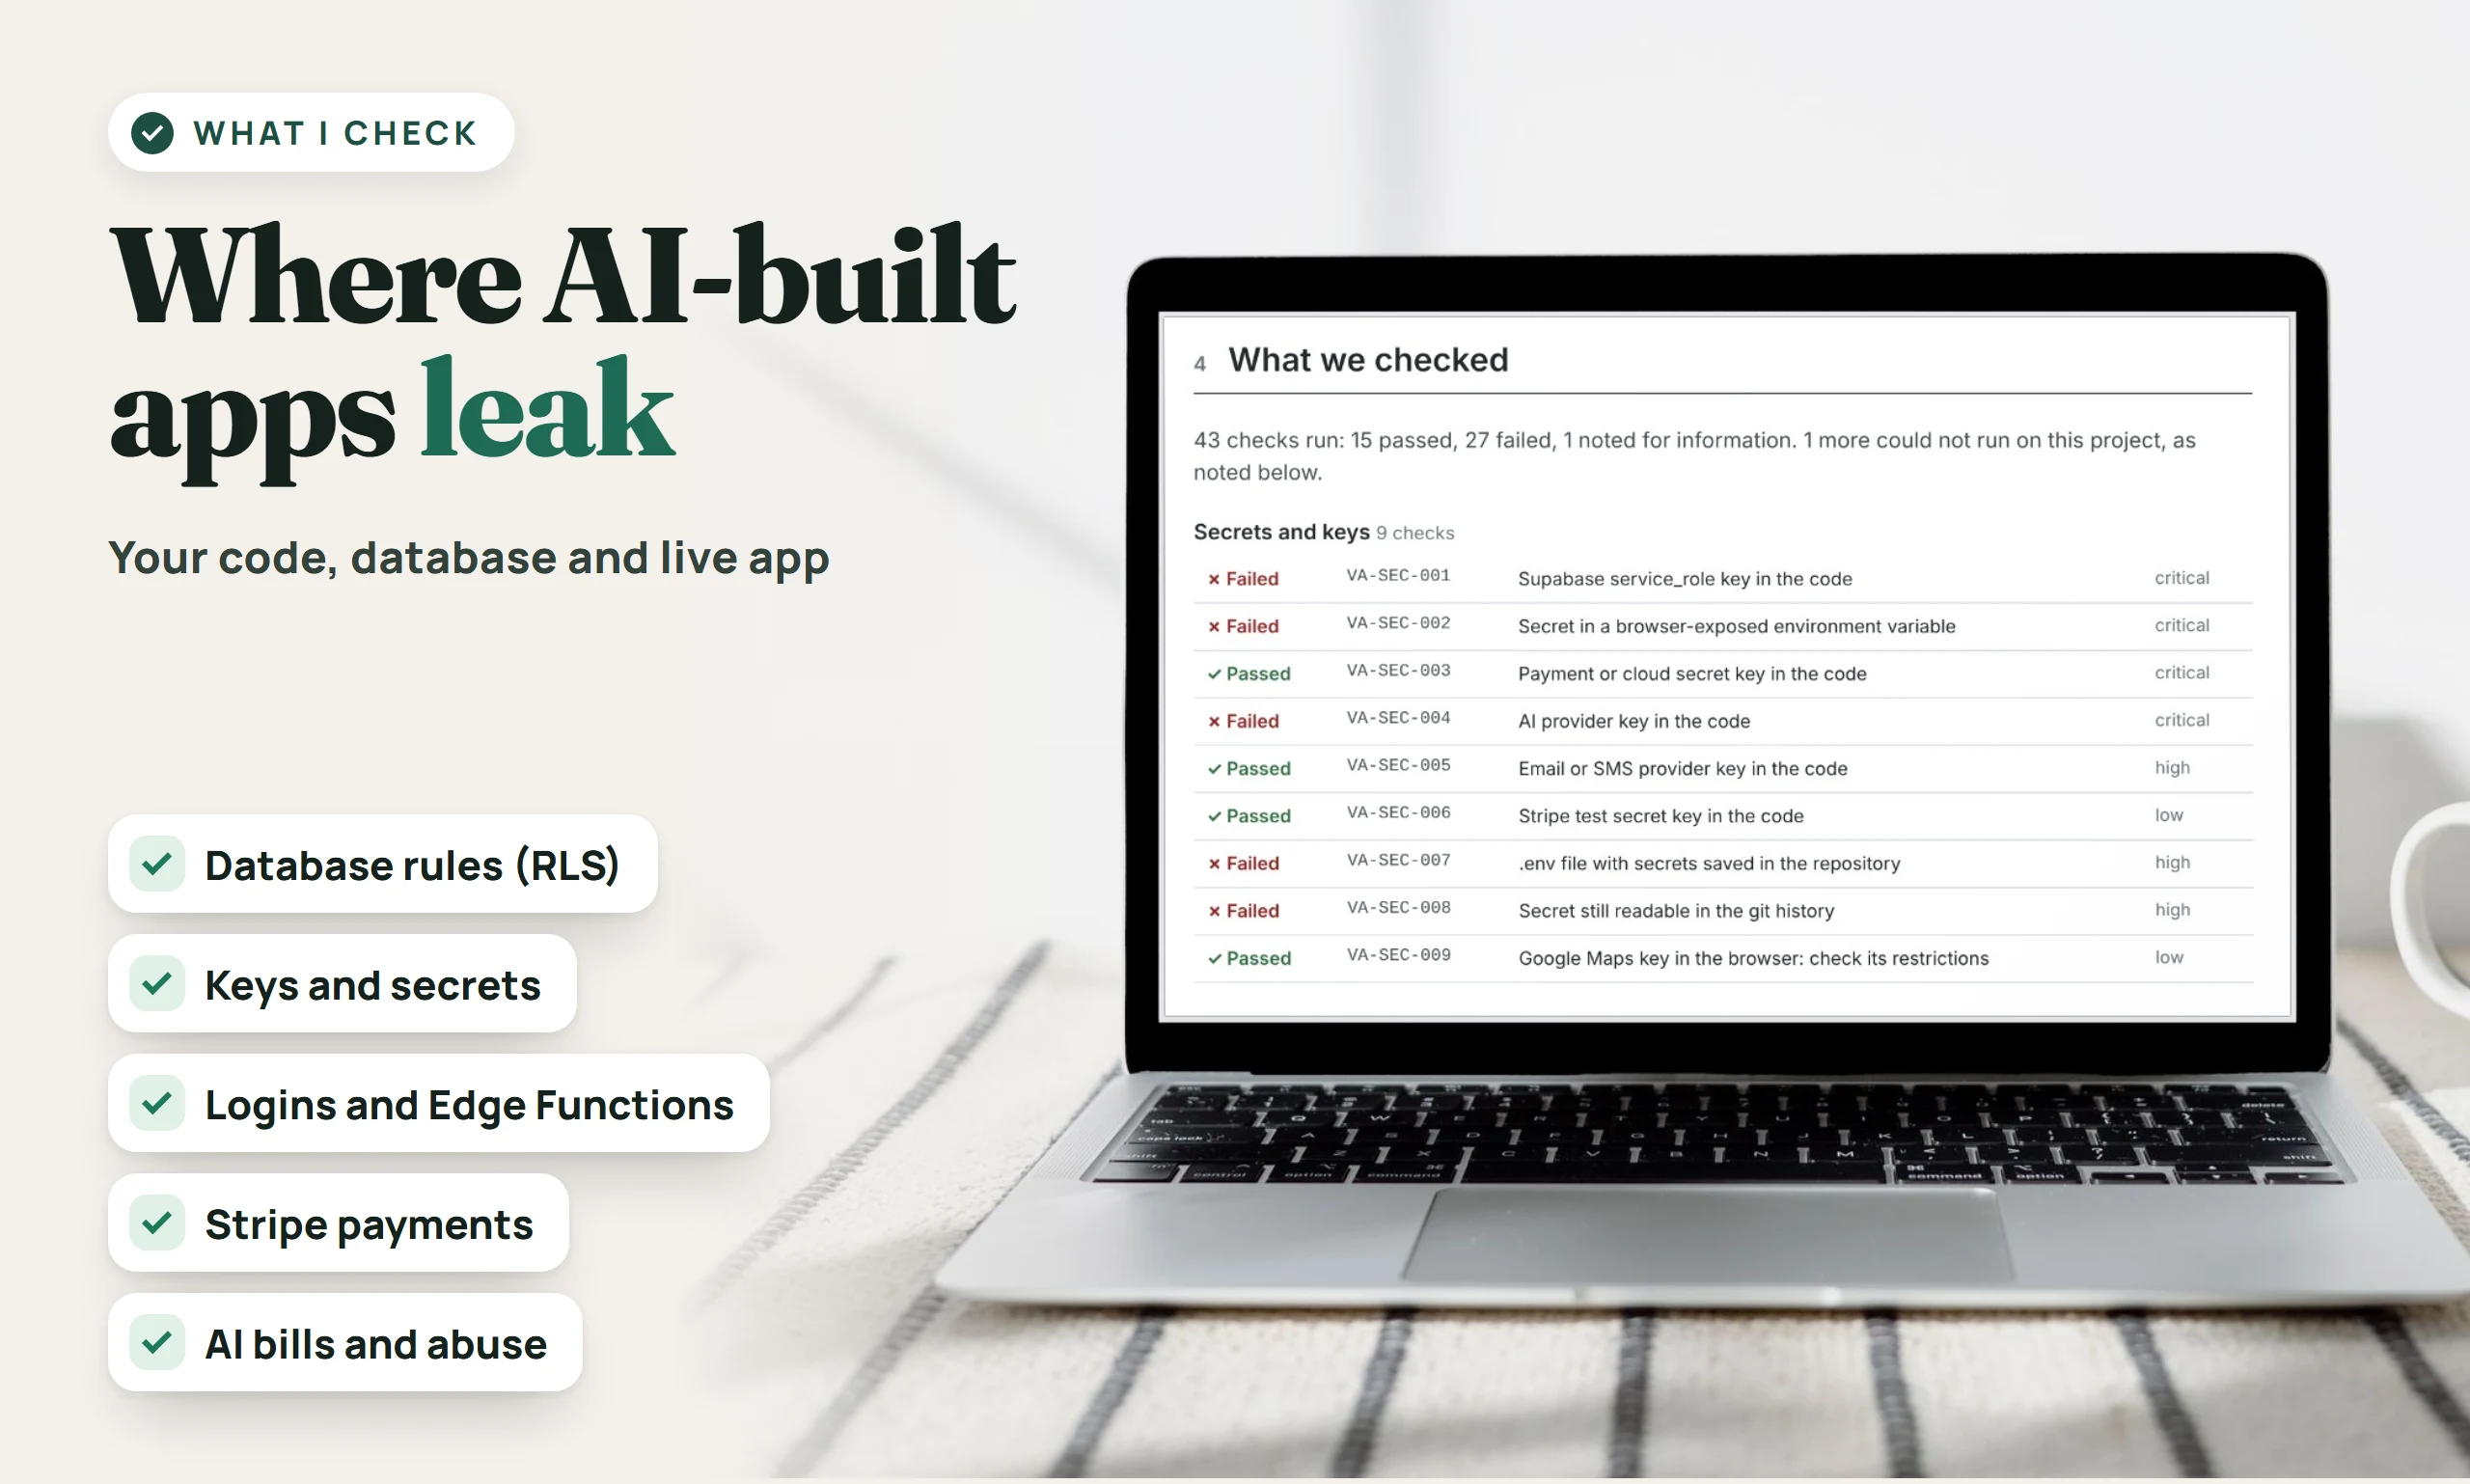
Supabase: row-level security, policies, storage buckets, database functions, views, Edge Functions and auth settings
Secrets: keys in code, .env files, git history and the live JavaScript
Payments: Stripe webhook signatures, prices taken from the browser, paid status set from the browser
Cost: AI providers called from the browser or from unprotected functions
Firebase rules, exposed files, security headers, source maps, vulnerable dependencies
What I need from you
read-only access to your code (GitHub), or a zip of the project
the address of your live app
your Supabase project URL and anon (publishable) key, the public key your app already sends to every visitor; for Firebase, the project ID
a short written authorisation for the live checks, which I send you here
Everything goes through Contra messages and attachments.
What I never do
I never ask for your passwords, your Supabase service_role or secret key, or your database password. I never change data in your live app during the audit, and I never test anything you have not authorised in writing.
An audit lowers risk; it is not a guarantee that no other flaw exists.
FAQs
Starting at$145
Duration2 days
Tags
Base44

Bolt.new

Firebase
Lovable
PostgreSQL
Replit
Stripe
Supabase
Vibe Coding
Service provided by
Zakaria MAMOUMI proBlanquefort, France
- 24
- Followers
Security audit and fix for Lovable, Bolt, Base44 and Replit appsZakaria MAMOUMI
Starting at$145
Duration2 days
Tags
Base44
Bolt.new
Firebase
Lovable
PostgreSQL
Replit
Stripe
Supabase
Vibe Coding
AI app builders get you from idea to live app in a weekend, but a working app can still leave your data open: database tables that anyone with your app's public key can read, secret keys sent to every visitor's browser, payment webhooks that anyone can fake, and AI features that anyone can call on your bill.
In our scan of 40 public apps built with Lovable and Bolt on Supabase (November 2026), 17 had at least one critical issue and 33 at least one high-severity issue.
How we ran it: the public code of 25 Lovable and 15 Bolt apps, read by our scanner, then every critical and high finding checked by hand. No live app was tested, and no app is named.
What you get
I review your code and, with your signed consent, your live app. You get a report that a non-developer can read in a few minutes:
every problem with proof: the file and line, or the live response
what it means for your business, in plain English
the exact fix, for me or your developer
a priced quote for the fixes
The report comes as a self-contained HTML file and a PDF.
Packages
Security scan + report: $145, delivered in 2 days (this listing)
Audit + urgent fixes: $395, delivered in 5 days. I fix the critical and high issues (up to about 4 hours of work), re-scan to show they are closed, and hand over a short note of what changed.
Full hardening + 1 month monitoring: $795, delivered in 10 days. I fix every issue above "info" level (up to 10 hours of work), re-scan, hand over a note, and the first month of monitoring is included.
Extra fixes are quoted from the report, from $250. Monitoring after the first month: $49/month, because each new prompt to your builder can reopen a hole. For the $395 or $795 package, message me here on Contra.
What I check
Supabase: row-level security, policies, storage buckets, database functions, views, Edge Functions and auth settings
Secrets: keys in code, .env files, git history and the live JavaScript
Payments: Stripe webhook signatures, prices taken from the browser, paid status set from the browser
Cost: AI providers called from the browser or from unprotected functions
Firebase rules, exposed files, security headers, source maps, vulnerable dependencies
What I need from you
read-only access to your code (GitHub), or a zip of the project
the address of your live app
your Supabase project URL and anon (publishable) key, the public key your app already sends to every visitor; for Firebase, the project ID
a short written authorisation for the live checks, which I send you here
Everything goes through Contra messages and attachments.
What I never do
I never ask for your passwords, your Supabase service_role or secret key, or your database password. I never change data in your live app during the audit, and I never test anything you have not authorised in writing.
An audit lowers risk; it is not a guarantee that no other flaw exists.
FAQs
$145