Secure Multi-Tenant FastAPI Backend with JWT & PostgresKrish Ardeshna
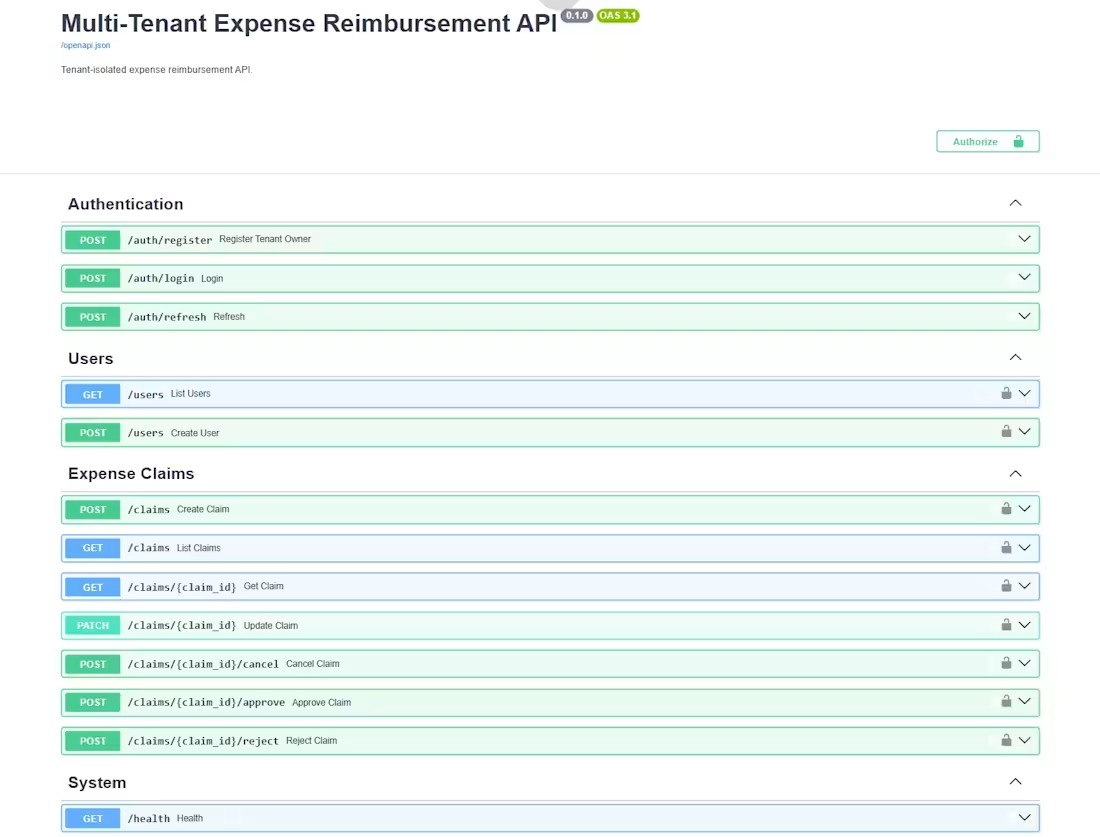
I build secure backend APIs with FastAPI JWT authentication, role-based access control, and PostgreSQL, not just a login page bolted onto a CRUD app.
What I've built:
A multi-tenant backend with JWT access + refresh tokens, admin/employee role enforcement, tenant isolation on every query, and Alembic-managed database migrations
Server-enforced business rules not just "logged in or not," but who can do what to which resource
Rate-limited login endpoint, consistent error responses, Docker Compose deployment
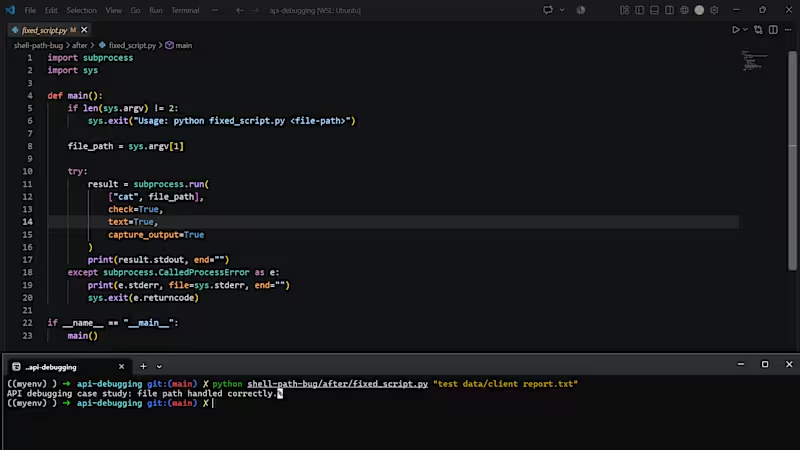
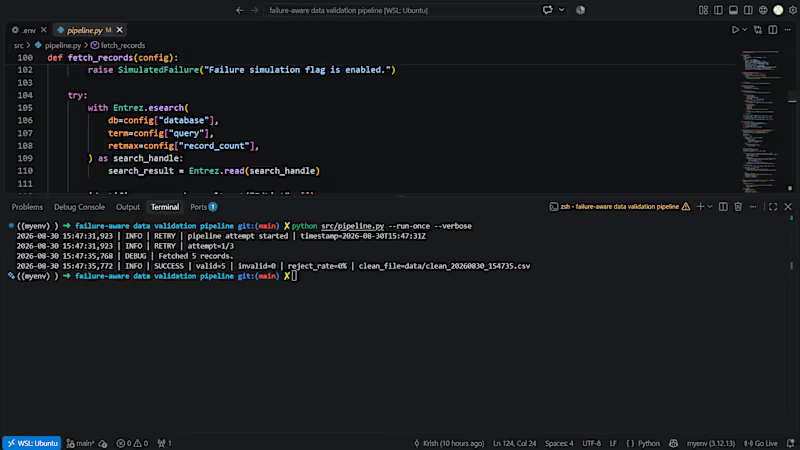
I write every line by hand and test it against a real running database, not just code that looks right. Every rule I claim is enforced, I can show you the request that proves it.
Need authentication, role-based permissions, or a backend that's actually production-shaped? Send me your requirements and I'll be honest about scope and timeline.
Contact for pricing
Duration1 week
Tags
Database Design
Docker
FastAPI
PostgreSQL
Python
API Development
Backend Engineer
JSON Web Token (JWT)
Web Security
Service provided by
Krish Ardeshna Jaipur, India
Secure Multi-Tenant FastAPI Backend with JWT & PostgresKrish Ardeshna
Contact for pricing
Duration1 week
Tags
Database Design
Docker
FastAPI
PostgreSQL
Python
API Development
Backend Engineer
JSON Web Token (JWT)
Web Security
I build secure backend APIs with FastAPI JWT authentication, role-based access control, and PostgreSQL, not just a login page bolted onto a CRUD app.
What I've built:
A multi-tenant backend with JWT access + refresh tokens, admin/employee role enforcement, tenant isolation on every query, and Alembic-managed database migrations
Server-enforced business rules not just "logged in or not," but who can do what to which resource
Rate-limited login endpoint, consistent error responses, Docker Compose deployment
I write every line by hand and test it against a real running database, not just code that looks right. Every rule I claim is enforced, I can show you the request that proves it.
Need authentication, role-based permissions, or a backend that's actually production-shaped? Send me your requirements and I'll be honest about scope and timeline.
Contact for pricing