Security Check of Your Lovable or Bolt App in 1 DayFlow Lab
You built your app in Lovable or Bolt, real customers are signing up, and you're not sure what a stranger can see. The usual gaps are tables anyone can read without an account, sign-up open to everyone, public file storage and secret keys left in the page code. When customer data leaks, you usually hear about it from a customer.
I check your app the way an outsider would, at your request and read-only: I don't sign in as your users, change anything or keep any data.
What you get in 1 day:
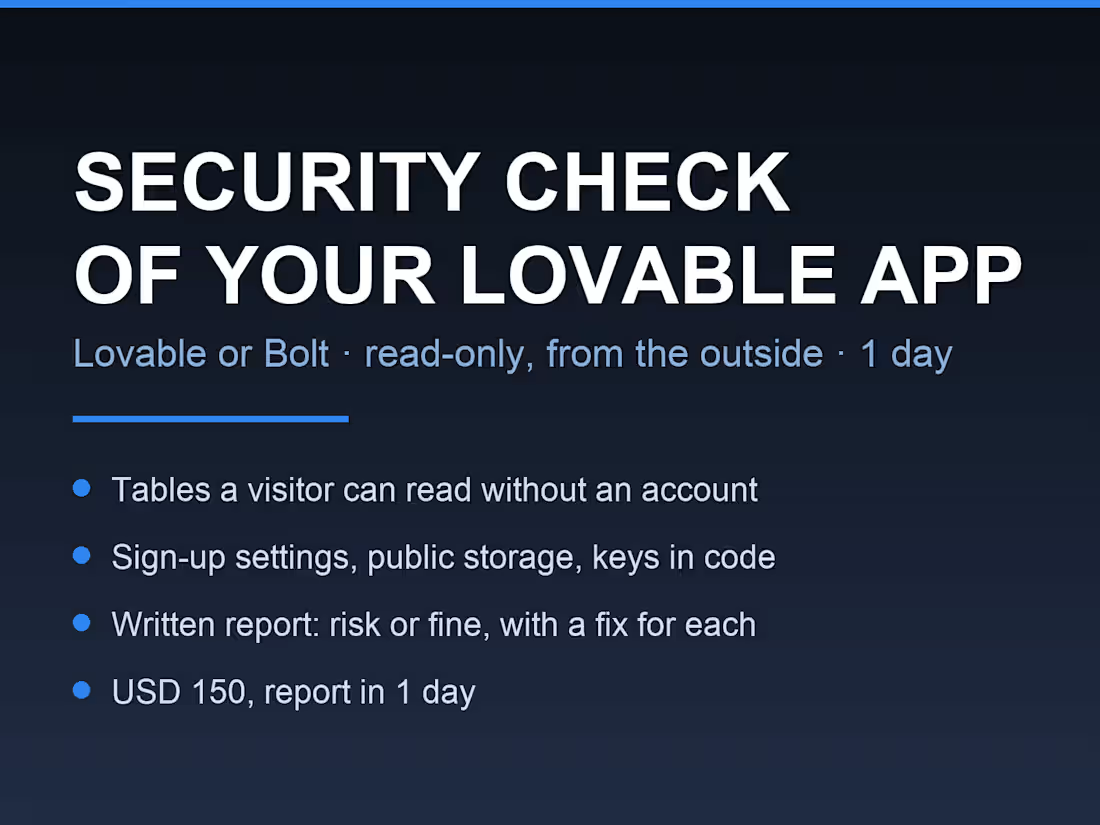
Every table your public API exposes, and how many rows a visitor without an account can read. Values are not copied.
Your sign-up and sign-in settings, public storage and keys in the front-end code.
The database functions that need a manual permission check.
A written report that marks each finding as a risk or fine, with the fix for each.
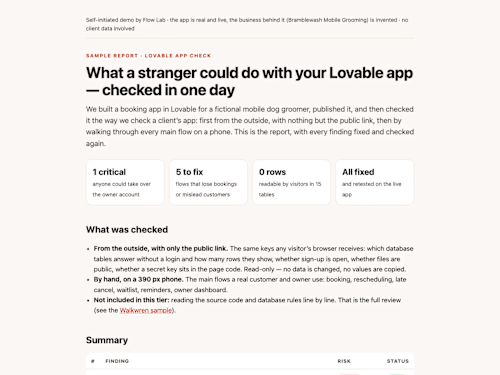
Sample report on a live Lovable app I built for a fictional business, with one critical finding and every fix retested: https://flowlab-dev.github.io/demo/lovable-check/
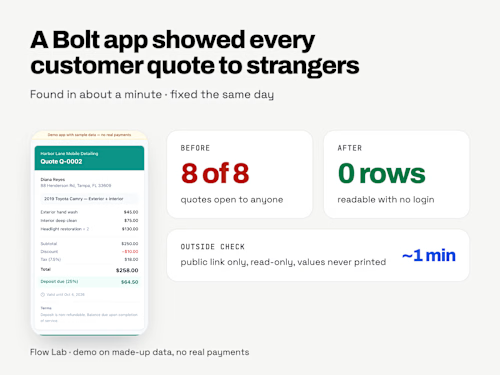
A deeper review of an AI-built React and Supabase app, with each security hole shown before and after the fix: https://flowlab-dev.github.io/work/app-rescue/
USD 150. If you want the fixes done too, I quote them at a fixed price after the report.
Also covers the Supabase change of October 30, 2026: I check that new tables have the grants your app needs and that row level security still limits what each user can see. Sample report: flowlab-dev.github.io/demo/supabase-oct30/
Example work
Starting at$150
Duration1 day
Tags
Bolt.new

Claude Code
Cursor
Lovable
Supabase
Vibe Coding
Web Developer
Service provided by
Flow Lab proBelarus
- 2
- Followers
Security Check of Your Lovable or Bolt App in 1 DayFlow Lab
Starting at$150
Duration1 day
Tags
Bolt.new
Claude Code
Cursor
Lovable
Supabase
Vibe Coding
Web Developer
You built your app in Lovable or Bolt, real customers are signing up, and you're not sure what a stranger can see. The usual gaps are tables anyone can read without an account, sign-up open to everyone, public file storage and secret keys left in the page code. When customer data leaks, you usually hear about it from a customer.
I check your app the way an outsider would, at your request and read-only: I don't sign in as your users, change anything or keep any data.
What you get in 1 day:
Every table your public API exposes, and how many rows a visitor without an account can read. Values are not copied.
Your sign-up and sign-in settings, public storage and keys in the front-end code.
The database functions that need a manual permission check.
A written report that marks each finding as a risk or fine, with the fix for each.
Sample report on a live Lovable app I built for a fictional business, with one critical finding and every fix retested: https://flowlab-dev.github.io/demo/lovable-check/
A deeper review of an AI-built React and Supabase app, with each security hole shown before and after the fix: https://flowlab-dev.github.io/work/app-rescue/
USD 150. If you want the fixes done too, I quote them at a fixed price after the report.
Also covers the Supabase change of October 30, 2026: I check that new tables have the grants your app needs and that row level security still limits what each user can see. Sample report: flowlab-dev.github.io/demo/supabase-oct30/
Example work
$150