Course members open your app with no second loginJago Westerduin
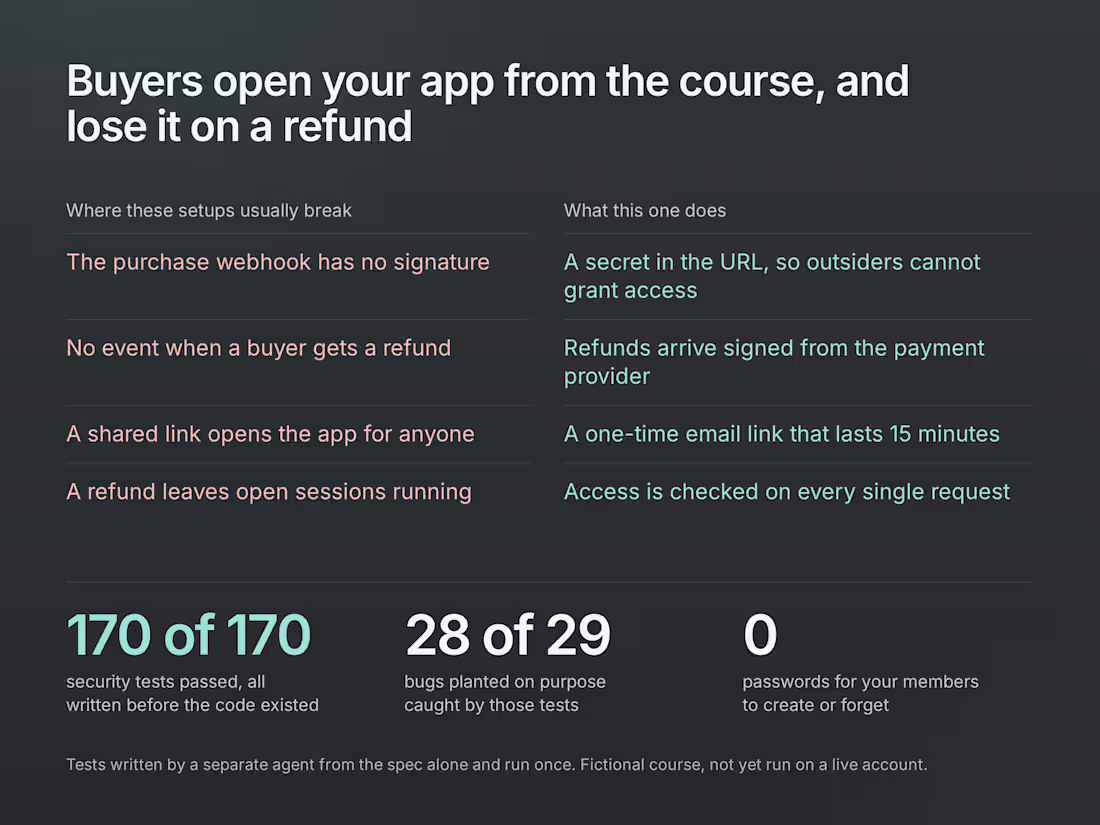
Your course lives on Kajabi or a similar platform and your app lives somewhere else. Buyers should get from one to the other without a second password, and lose access when they get their money back. That second part is where these setups quietly fail: Kajabi documents no signature on its purchase webhook and no event for a refund, so a simple connection can be forged, and refunded buyers stay inside.
What you get: a one-time email link from the course page to your app, with no password to create or forget; access that follows the money, so purchases grant it and refunds and cancellations from your payment provider end it, even for someone who is signed in; and security tests for forged purchases, reused links and shared access, with a short runbook.
Proof: in my demo a separate agent wrote 170 security tests from the spec before any code existed, and all 170 passed on the one run. To check that those tests can fail, I planted 29 bugs on purpose. They caught 28, and the one they missed still kept the visitor on the site.
The demo ran against a stand-in, so the first step on your project is checking the real events with a test purchase. 14 days of fixes after delivery.
Starting at$350
Duration1 week
Tags
Kajabi

Python
Service provided by
Jago Westerduin proThe Hague, Netherlands
Course members open your app with no second loginJago Westerduin
Starting at$350
Duration1 week
Tags
Kajabi
Python
Your course lives on Kajabi or a similar platform and your app lives somewhere else. Buyers should get from one to the other without a second password, and lose access when they get their money back. That second part is where these setups quietly fail: Kajabi documents no signature on its purchase webhook and no event for a refund, so a simple connection can be forged, and refunded buyers stay inside.
What you get: a one-time email link from the course page to your app, with no password to create or forget; access that follows the money, so purchases grant it and refunds and cancellations from your payment provider end it, even for someone who is signed in; and security tests for forged purchases, reused links and shared access, with a short runbook.
Proof: in my demo a separate agent wrote 170 security tests from the spec before any code existed, and all 170 passed on the one run. To check that those tests can fail, I planted 29 bugs on purpose. They caught 28, and the one they missed still kept the visitor on the site.
The demo ran against a stand-in, so the first step on your project is checking the real events with a test purchase. 14 days of fixes after delivery.
$350