I will secure your legacy PHP app so only your team can log inNahin Akbar
Does your business run a private app that anyone on the internet can try to log into?
That's the risk with most older internal apps. It was built for your team — an admin panel, a dashboard, a billing or inventory tool, a booking back-office, a reporting system — but it's sitting online where bots and hackers can find the login page and try all day.
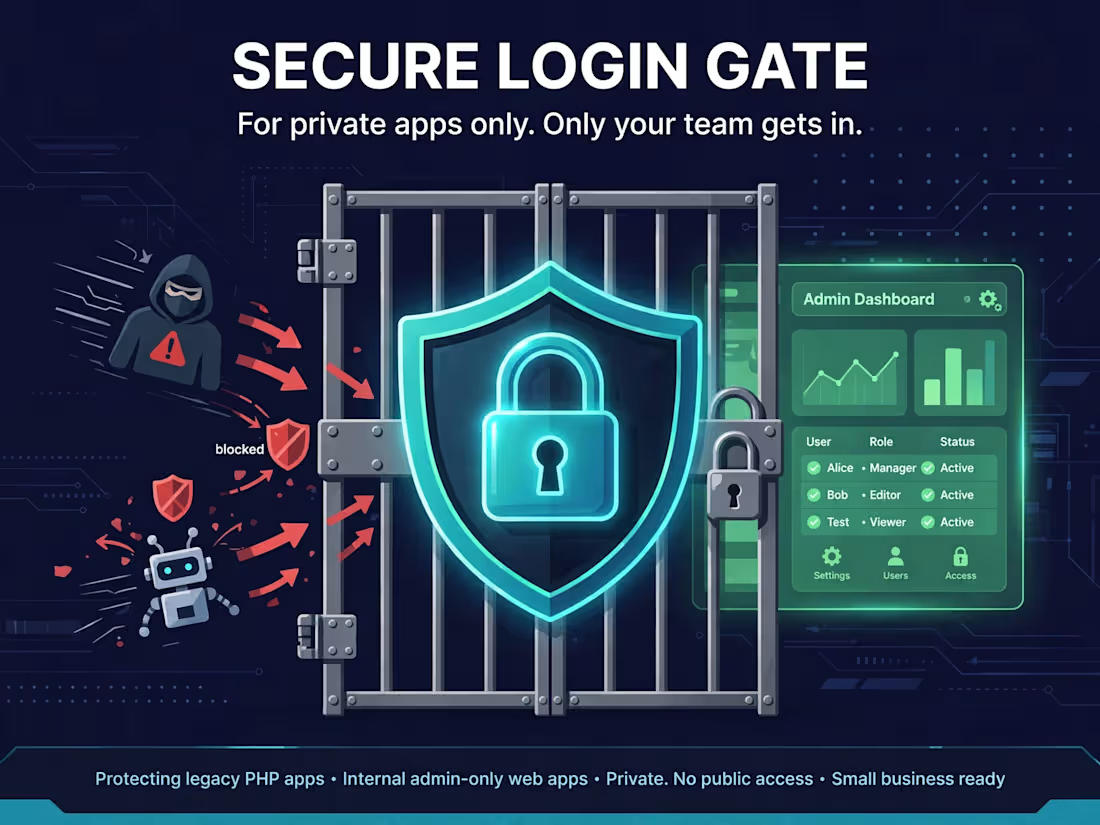
I put a secure gate in front of the whole app, so only your team can even reach it. Like locking the building, not just the office door: your team logs in properly and gets in as normal, everyone else is turned away before they can touch your app, try a password, or look for weak spots.
Why private apps are perfect for this: There's nothing public to keep open. No customers, no shop, no blog, no Google listing to worry about. Your whole app is meant to be private, so we can protect the whole thing — clean and simple. That's why I don't offer this for public WordPress sites.
This is for you if you have: an older PHP app you still rely on and don't want to rebuild, an internal admin panel / dashboard / back-office tool, a private billing, inventory, property, school, clinic or staff app, a test/staging app that should never be public — any web app only your team should ever see.
What you'll get: a quick check of how your app is exposed today, the gate set up, login with Google Workspace or Microsoft 365 if you want (no new passwords), testing that your team can get in and strangers can't, and plain-English notes on adding/removing people.
Not for: public websites, blogs, shops, or apps your customers log into.
⭐ Special note if you have WordPress
If you have a WordPress website that is mostly content and simple forms — pages, blog posts, a contact form, a quote / enquiry form — I can do something even better for you:
I can build a static copy of your public website and put it on Cloudflare Pages for your visitors, while you keep WordPress behind the scenes to edit it.
Your visitors see a fast, static website — there's no public WordPress for hackers to attack, no login page exposed, and no plugins to exploit
It loads quickly all over the world, and is very cheap (often free) to run
You and your team still log into your WordPress admin area as you do today to change pages and posts — and that admin area can be protected with the same secure gate above
When you update content in WordPress, the public static site is rebuilt / updated
Simple forms still work — we connect them safely so enquiries still reach your inbox
Message me with what the app does, who is supposed to use it, and how your team logs in today. I'll reply honestly if it's not a fit.
For technical clients: this is an OIDC login check handled by Nginx, so unauthorised requests are blocked before your app code runs — for legacy PHP, before PHP processing starts.
Contact for pricing
Duration1 week
Tags
Nginx

PHP
Backend Engineer
SSO
google login
Social Login
web security
Service provided by
Nahin Akbar Dhaka, Bangladesh
I will secure your legacy PHP app so only your team can log inNahin Akbar
Contact for pricing
Duration1 week
Tags
Nginx
PHP
Backend Engineer
SSO
google login
Social Login
web security
Does your business run a private app that anyone on the internet can try to log into?
That's the risk with most older internal apps. It was built for your team — an admin panel, a dashboard, a billing or inventory tool, a booking back-office, a reporting system — but it's sitting online where bots and hackers can find the login page and try all day.
I put a secure gate in front of the whole app, so only your team can even reach it. Like locking the building, not just the office door: your team logs in properly and gets in as normal, everyone else is turned away before they can touch your app, try a password, or look for weak spots.
Why private apps are perfect for this: There's nothing public to keep open. No customers, no shop, no blog, no Google listing to worry about. Your whole app is meant to be private, so we can protect the whole thing — clean and simple. That's why I don't offer this for public WordPress sites.
This is for you if you have: an older PHP app you still rely on and don't want to rebuild, an internal admin panel / dashboard / back-office tool, a private billing, inventory, property, school, clinic or staff app, a test/staging app that should never be public — any web app only your team should ever see.
What you'll get: a quick check of how your app is exposed today, the gate set up, login with Google Workspace or Microsoft 365 if you want (no new passwords), testing that your team can get in and strangers can't, and plain-English notes on adding/removing people.
Not for: public websites, blogs, shops, or apps your customers log into.
⭐ Special note if you have WordPress
If you have a WordPress website that is mostly content and simple forms — pages, blog posts, a contact form, a quote / enquiry form — I can do something even better for you:
I can build a static copy of your public website and put it on Cloudflare Pages for your visitors, while you keep WordPress behind the scenes to edit it.
Your visitors see a fast, static website — there's no public WordPress for hackers to attack, no login page exposed, and no plugins to exploit
It loads quickly all over the world, and is very cheap (often free) to run
You and your team still log into your WordPress admin area as you do today to change pages and posts — and that admin area can be protected with the same secure gate above
When you update content in WordPress, the public static site is rebuilt / updated
Simple forms still work — we connect them safely so enquiries still reach your inbox
Message me with what the app does, who is supposed to use it, and how your team logs in today. I'll reply honestly if it's not a fit.
For technical clients: this is an OIDC login check handled by Nginx, so unauthorised requests are blocked before your app code runs — for legacy PHP, before PHP processing starts.
Contact for pricing