Software Supply Chain Security & Secrets ToolingMircea Stefanescu
Make build outputs and application secrets easier to control and inspect. I can integrate artifact checks, secret access and operational visibility into an agreed development workflow.
Possible deliverables — final scope agreed per project:
Software supply chain checks
SBOM generation, vulnerability and license checks, signed artifacts and provenance, tamper-rejection tests and release policies.
Technology: CycloneDX, Trivy, Grype, Cosign, Jenkins, policy checks
Demonstration scope: These are implemented pipeline controls, not an independent security audit or compliance certification.
Secrets integration and operational visibility
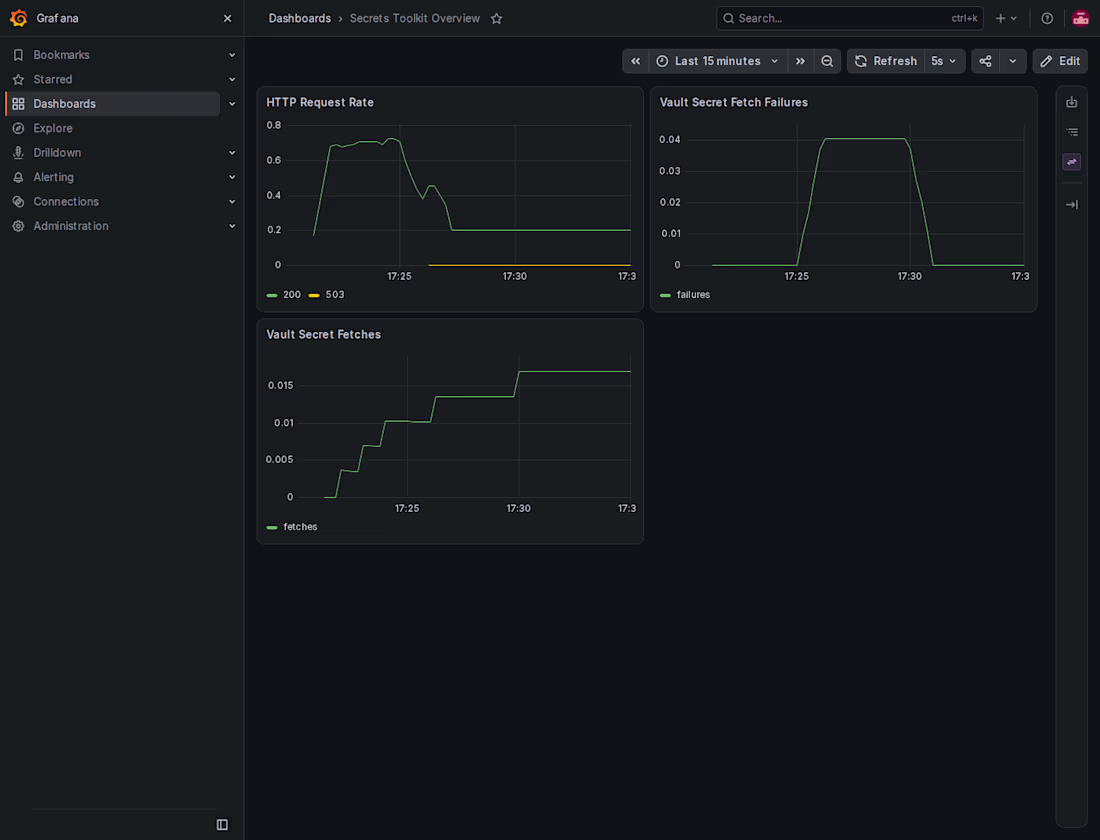
Vault AppRole integration, access policies, rotation, audit logs, dashboards and tested recovery procedures.
Technology: Vault, Terraform, Node.js, Elasticsearch, Prometheus, Grafana
Demonstration scope: KMS and regional failover are local demonstrations. No live cloud certification or compliance assurance is claimed.
How we start
Send a short description of your existing system, the problem, your expected outcome and target date through Contra. I will assess fit before proposing deliverables, acceptance criteria, schedule and pricing. Related custom software needs are welcome when the work is a good fit. Remote collaboration and English documentation.
The cover is an original screenshot from my portfolio demonstration, not a customer result. External hosting or provider usage, if needed for your project, must be agreed separately.
Explore all service areas: https://stefanescumircea1990.wordpress.com/software-services/
Timeline: the displayed one-week estimate is for a small initial milestone. The actual scope and schedule are confirmed before accepting work; larger implementations are planned in separate milestones.
How we work and verify the first milestone
Before work starts, we agree a small first milestone, required inputs, acceptance checks, price, delivery date and an update cadence. For implementation work, the handover can include the agreed source or configuration, relevant test results, setup notes and known limits. The final scope is confirmed before accepting the project.
For security and secrets tooling: agree the specific control, allowed and denied cases, required evidence and recovery needs. This is implementation work, not independent certification or a guarantee of complete security.
Contact for pricing
Duration1 week
Tags
DevOps Engineer
Service provided by
Mircea Stefanescu Bucharest, Romania
Software Supply Chain Security & Secrets ToolingMircea Stefanescu
Contact for pricing
Duration1 week
Tags
DevOps Engineer
Make build outputs and application secrets easier to control and inspect. I can integrate artifact checks, secret access and operational visibility into an agreed development workflow.
Possible deliverables — final scope agreed per project:
Software supply chain checks
SBOM generation, vulnerability and license checks, signed artifacts and provenance, tamper-rejection tests and release policies.
Technology: CycloneDX, Trivy, Grype, Cosign, Jenkins, policy checks
Demonstration scope: These are implemented pipeline controls, not an independent security audit or compliance certification.
Secrets integration and operational visibility
Vault AppRole integration, access policies, rotation, audit logs, dashboards and tested recovery procedures.
Technology: Vault, Terraform, Node.js, Elasticsearch, Prometheus, Grafana
Demonstration scope: KMS and regional failover are local demonstrations. No live cloud certification or compliance assurance is claimed.
How we start
Send a short description of your existing system, the problem, your expected outcome and target date through Contra. I will assess fit before proposing deliverables, acceptance criteria, schedule and pricing. Related custom software needs are welcome when the work is a good fit. Remote collaboration and English documentation.
The cover is an original screenshot from my portfolio demonstration, not a customer result. External hosting or provider usage, if needed for your project, must be agreed separately.
Explore all service areas: https://stefanescumircea1990.wordpress.com/software-services/
Timeline: the displayed one-week estimate is for a small initial milestone. The actual scope and schedule are confirmed before accepting work; larger implementations are planned in separate milestones.
How we work and verify the first milestone
Before work starts, we agree a small first milestone, required inputs, acceptance checks, price, delivery date and an update cadence. For implementation work, the handover can include the agreed source or configuration, relevant test results, setup notes and known limits. The final scope is confirmed before accepting the project.
For security and secrets tooling: agree the specific control, allowed and denied cases, required evidence and recovery needs. This is implementation work, not independent certification or a guarantee of complete security.
Contact for pricing