Full Web Application Penetration Test – StandardWunmi Aladesanmi
You've built your web app. Now, can it survive a real attack?
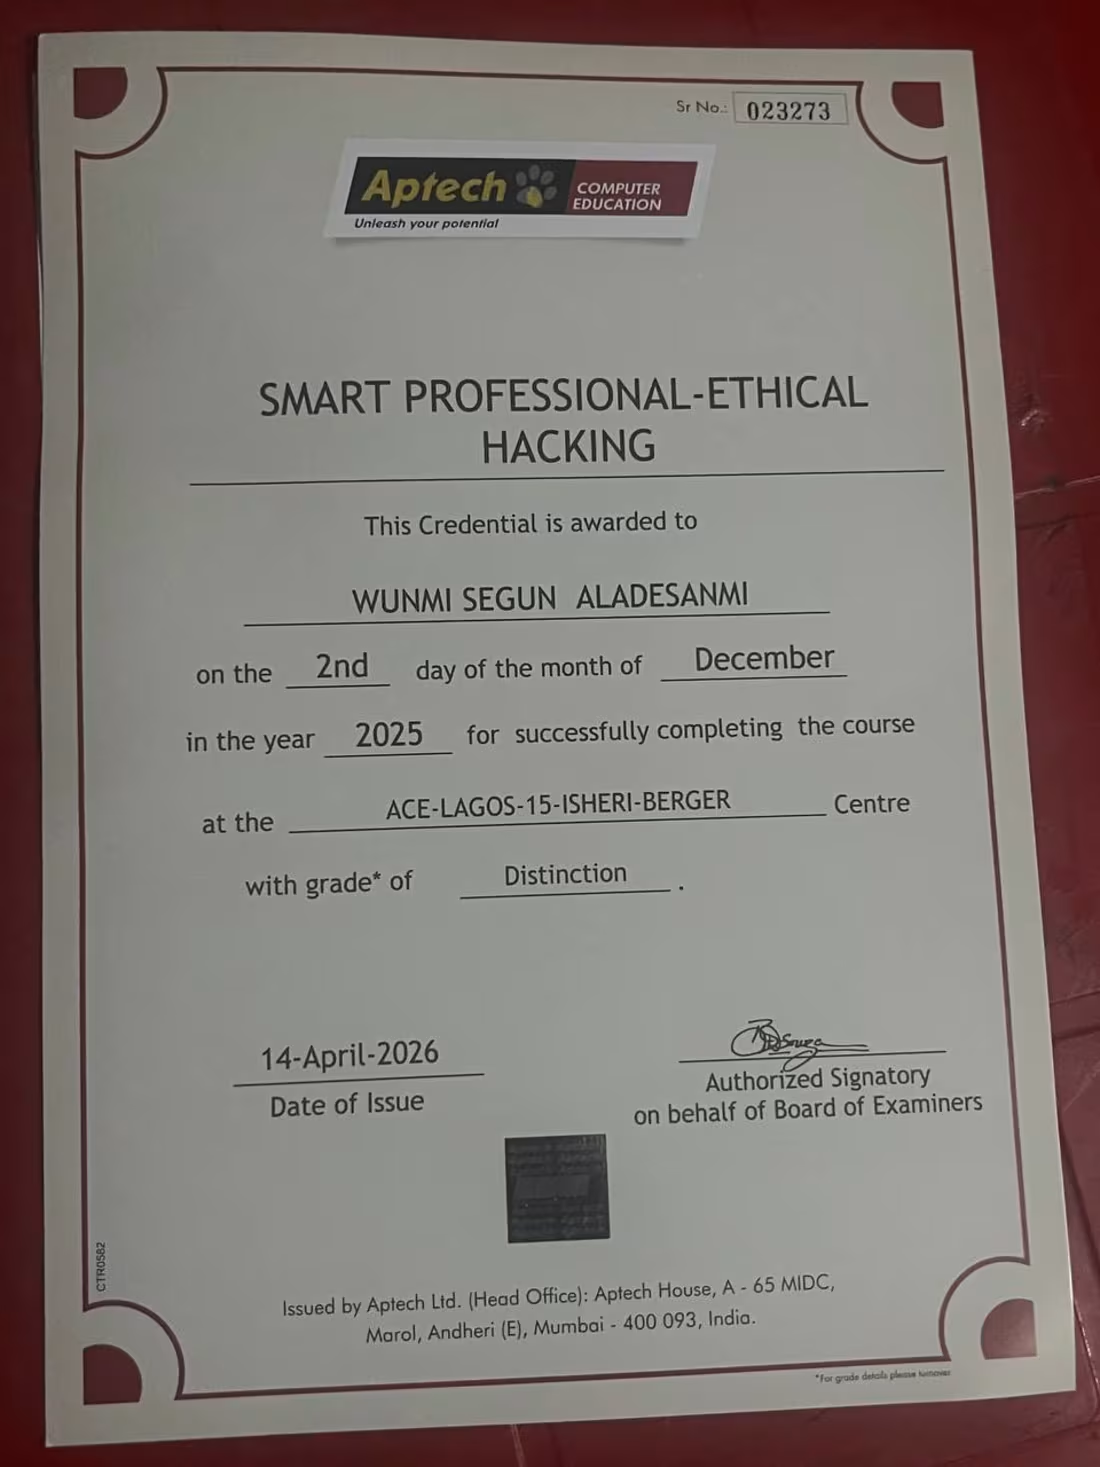
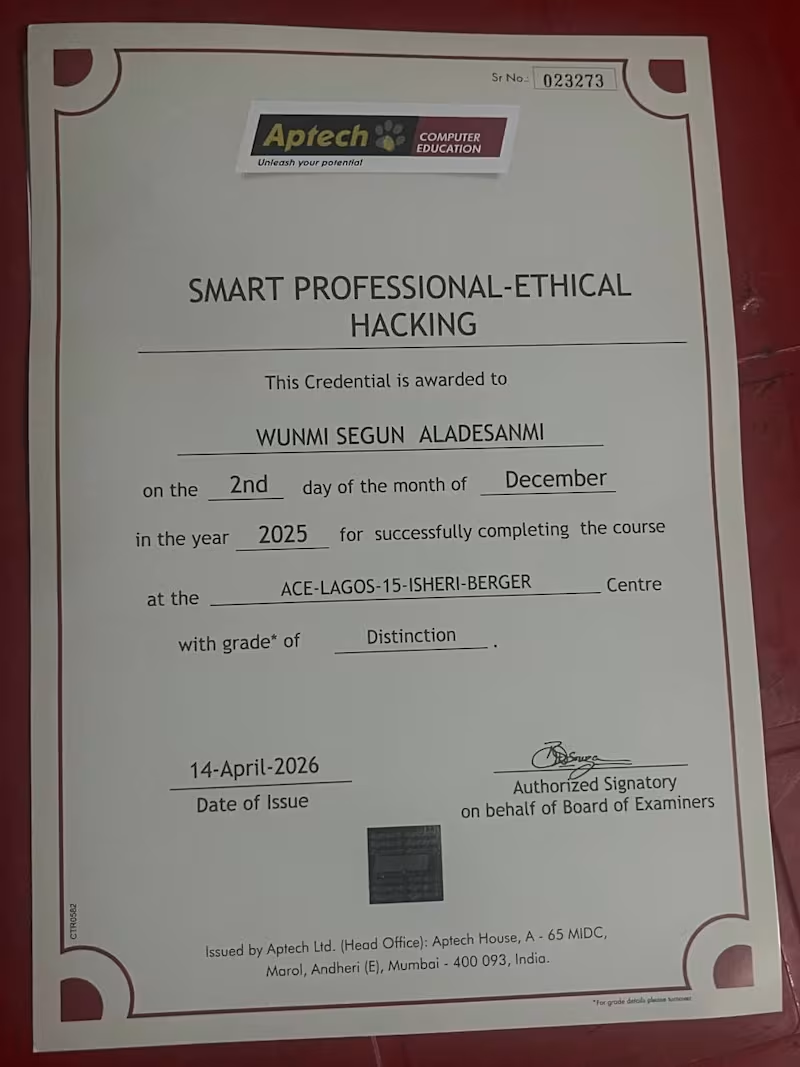
I'm Wunmi, a Certified Ethical Hacker (APTECH, Distinction, 2025). I have a proven track record of finding and reporting security vulnerabilities for Apple, AWS, Google, Grammarly, Shopify, and Coinbase. Companies trust me because I think like an adversary, not just a scanner.
🔍 What I'll Do for You
In this package, I will perform a thorough manual penetration test of your web application and its APIs. I go far beyond automated scans by manually checking for the vulnerabilities that matter most:
OWASP Top 10 (SQLi, XSS, CSRF, SSRF, etc.)
Broken Authentication & Session Management
Business Logic Flaws & Privilege Escalation (IDOR)
API Security (REST & GraphQL)
📦 What You Will Receive
Within 2 weeks, you will get a comprehensive PDF report that includes:
Executive Summary: A clear overview for your leadership team.
Detailed Findings: Each vulnerability with a CVSS score, proof-of-concept screenshots, and a clear description of the business impact.
Step-by-Step Fixes: Actionable, developer-friendly guidance to remediate every issue.
✅ Why Work With Me?
Proven Expertise: Certified Ethical Hacker with real-world bug bounty wins for Fortune 500 companies.
Legal & Professional: I will sign your NDA. All work is governed by a signed Rules of Engagement (ROE) to ensure a safe, authorized, and confidential engagement.
Clear Communication: I deliver reports that bridge the gap between security and development teams.
⚖️ Before You Order, I Require:
A signed Rules of Engagement (ROE) agreement outlining the scope.
Written authorization to test (a staging environment is preferred, or explicit approval for production).
📩 Ready to secure your application? Message me to define your scope and get started.
FAQs
Wunmi's other services
Starting at$750
Duration2 weeks
Tags
Burp Suite

Kali Linux

OWASP
Cybersecurity Specialist
API security
ethical hacking
penetration testing
vulnerability assessment
web application security
Service provided by
Wunmi Aladesanmi Lagos, Nigeria
- 1
- Followers
Full Web Application Penetration Test – StandardWunmi Aladesanmi
Starting at$750
Duration2 weeks
Tags
Burp Suite
Kali Linux
OWASP
Cybersecurity Specialist
API security
ethical hacking
penetration testing
vulnerability assessment
web application security
You've built your web app. Now, can it survive a real attack?
I'm Wunmi, a Certified Ethical Hacker (APTECH, Distinction, 2025). I have a proven track record of finding and reporting security vulnerabilities for Apple, AWS, Google, Grammarly, Shopify, and Coinbase. Companies trust me because I think like an adversary, not just a scanner.
🔍 What I'll Do for You
In this package, I will perform a thorough manual penetration test of your web application and its APIs. I go far beyond automated scans by manually checking for the vulnerabilities that matter most:
OWASP Top 10 (SQLi, XSS, CSRF, SSRF, etc.)
Broken Authentication & Session Management
Business Logic Flaws & Privilege Escalation (IDOR)
API Security (REST & GraphQL)
📦 What You Will Receive
Within 2 weeks, you will get a comprehensive PDF report that includes:
Executive Summary: A clear overview for your leadership team.
Detailed Findings: Each vulnerability with a CVSS score, proof-of-concept screenshots, and a clear description of the business impact.
Step-by-Step Fixes: Actionable, developer-friendly guidance to remediate every issue.
✅ Why Work With Me?
Proven Expertise: Certified Ethical Hacker with real-world bug bounty wins for Fortune 500 companies.
Legal & Professional: I will sign your NDA. All work is governed by a signed Rules of Engagement (ROE) to ensure a safe, authorized, and confidential engagement.
Clear Communication: I deliver reports that bridge the gap between security and development teams.
⚖️ Before You Order, I Require:
A signed Rules of Engagement (ROE) agreement outlining the scope.
Written authorization to test (a staging environment is preferred, or explicit approval for production).
📩 Ready to secure your application? Message me to define your scope and get started.
FAQs
Wunmi's other services
$750