I will audit your cybersecurity posture & identify critical gapsAbdul Nafay Sarmad
You cannot fix security gaps you don't know exist.
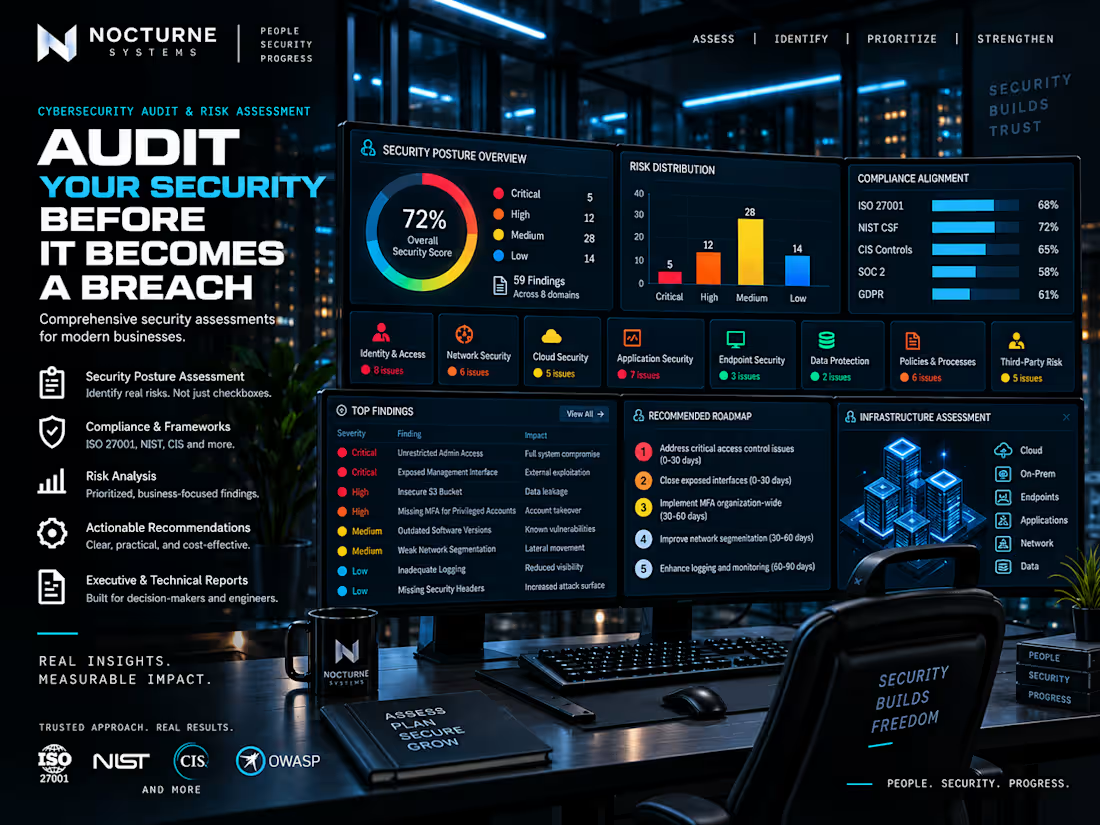
I perform structured cybersecurity assessments to identify weaknesses across your infrastructure, applications, cloud environment, identity controls, policies, operational processes, and security architecture.
This is designed for organizations that need an independent view of their security posture before an audit, certification effort, major deployment, customer assessment, or security investment.
Areas I can review include:
Identity and access management
Endpoint security
Network architecture and segmentation
Cloud security controls
Application security
Logging and monitoring
Backup and recovery
Vulnerability management
Incident-response readiness
Security policies and procedures
Third-party risk
Privileged-access controls
Security awareness processes
Governance and compliance alignment
Assessments can be mapped against frameworks such as NIST CSF, CIS Controls, ISO 27001, and relevant organizational requirements.
What you receive
Executive-level security summary
Detailed technical findings
Risk-ranked issues
Evidence and observations
Recommended remediation actions
Prioritized security roadmap
The goal isn't a 90-page PDF nobody reads. You get a practical answer to three questions:
What's wrong? What matters most? What should we fix first?
Contact for pricing
Duration1 week
Tags
NIST
Risk Assessment
Cloud Security Engineer
Cybersecurity Specialist
Security Engineer
Compliance
GRC
ISO 27001
Security Audit
Service provided by
Abdul Nafay Sarmad Karachi, Pakistan
I will audit your cybersecurity posture & identify critical gapsAbdul Nafay Sarmad
Contact for pricing
Duration1 week
Tags
NIST
Risk Assessment
Cloud Security Engineer
Cybersecurity Specialist
Security Engineer
Compliance
GRC
ISO 27001
Security Audit
You cannot fix security gaps you don't know exist.
I perform structured cybersecurity assessments to identify weaknesses across your infrastructure, applications, cloud environment, identity controls, policies, operational processes, and security architecture.
This is designed for organizations that need an independent view of their security posture before an audit, certification effort, major deployment, customer assessment, or security investment.
Areas I can review include:
Identity and access management
Endpoint security
Network architecture and segmentation
Cloud security controls
Application security
Logging and monitoring
Backup and recovery
Vulnerability management
Incident-response readiness
Security policies and procedures
Third-party risk
Privileged-access controls
Security awareness processes
Governance and compliance alignment
Assessments can be mapped against frameworks such as NIST CSF, CIS Controls, ISO 27001, and relevant organizational requirements.
What you receive
Executive-level security summary
Detailed technical findings
Risk-ranked issues
Evidence and observations
Recommended remediation actions
Prioritized security roadmap
The goal isn't a 90-page PDF nobody reads. You get a practical answer to three questions:
What's wrong? What matters most? What should we fix first?
Contact for pricing